Skip to content
October 31, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
NVIDIA Patches Triton Inference Server Vulnerabilities Critical Triton Inference Server vulnerabilities diagram showing denial of service risks
  • Vulnerability Report

NVIDIA Patches Triton Inference Server Vulnerabilities

Do Son September 10, 2026 0

NVIDIA fixed critical Triton Inference Server vulnerabilities. Patch your Triton Inference Server vulnerabilities now to stop denial of service attacks.
Apache Artemis Vulnerabilities Demand Immediate Action Apache Artemis vulnerabilities and ActiveMQ Artemis flaws
  • Vulnerability Report

Apache Artemis Vulnerabilities Demand Immediate Action

Do Son September 10, 2026 0

Critical Apache Artemis vulnerabilities, including CVE-2026-67593 and other ActiveMQ Artemis flaws, expose systems to denial of service and data exposure.
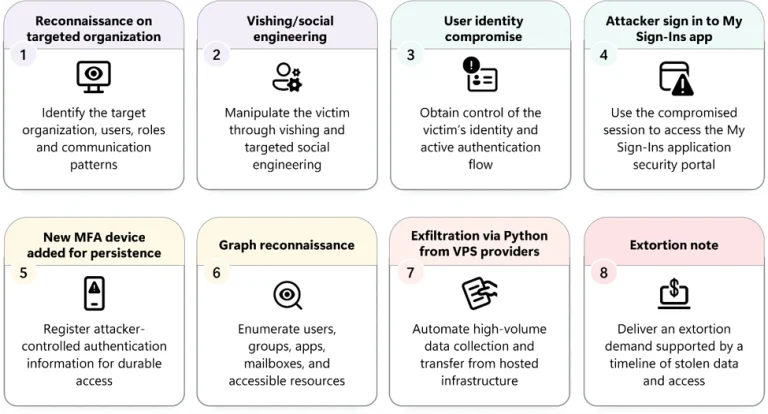
Passkey Social Engineering Attacks Breach Enterprise Cloud Data Diagram illustrating passkey social engineering and passkey social engineering attacks
  • Cybercriminals

Passkey Social Engineering Attacks Breach Enterprise Cloud Data

Do Son September 10, 2026 0

Microsoft warned of passkey social engineering attacks hitting tenants. Learn how passkey social engineering targets enterprise cloud identities.
Arista Patches Critical Arista EOS Vulnerabilities Overview of critical Arista EOS vulnerabilities impacting network switches
  • Vulnerability Report

Arista Patches Critical Arista EOS Vulnerabilities

Do Son September 10, 2026 0

Arista released fixes for critical Arista EOS vulnerabilities. Learn how these Arista EOS vulnerabilities impact enterprise switches and edge devices.
UEFI Shell Flaw Causes Secure Boot Bypass Vulnerability Secure Boot bypass vulnerability exploitation using UEFI Shell flaw
  • Vulnerability Report

UEFI Shell Flaw Causes Secure Boot Bypass Vulnerability

Do Son September 10, 2026 0

A critical Secure Boot bypass vulnerability via a UEFI Shell flaw exposes servers to code execution. Discover how CVE-2026-33197 impacts devices.
MongoDB Patches 24 Server Vulnerabilities, One Critical MongoDB Server vulnerabilities dashboard showing a critical authorization bypass and unauthenticated denial of service flaws
  • Vulnerability Report

MongoDB Patches 24 Server Vulnerabilities, One Critical

Do Son September 10, 2026 0

MongoDB fixed 24 MongoDB Server vulnerabilities, including a critical auth bypass (CVE-2026-82067) and unauthenticated denial of service flaws. Patch now.
Critical Okta Vulnerabilities Patched Across Multiple Tools Diagram showing critical Okta vulnerabilities and authorization bypass flaws
  • Vulnerability Report

Critical Okta Vulnerabilities Patched Across Multiple Tools

Do Son September 10, 2026 0

Okta fixed critical Okta vulnerabilities across multiple tools. Patch these Okta vulnerabilities today to prevent code execution and authorization bypass.
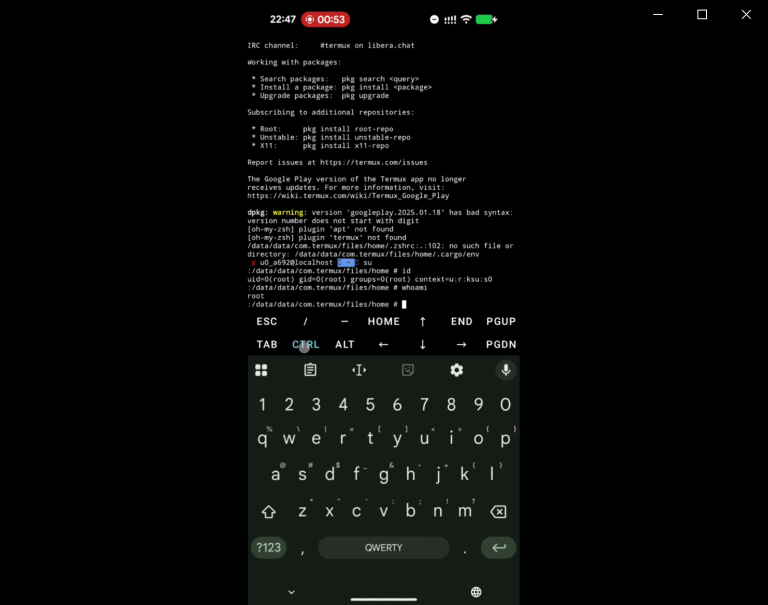
LSPromise Exploit Chain Enables Complete Android Rooting Diagram detailing the stages of the LSPromise exploit chain on Android
  • Vulnerability Report

LSPromise Exploit Chain Enables Complete Android Rooting

Do Son September 10, 2026 0

The LSPromise exploit chain provides a 100% success rate for local privilege escalation to root on Android 17. Details and PoC are publicly disclosed.
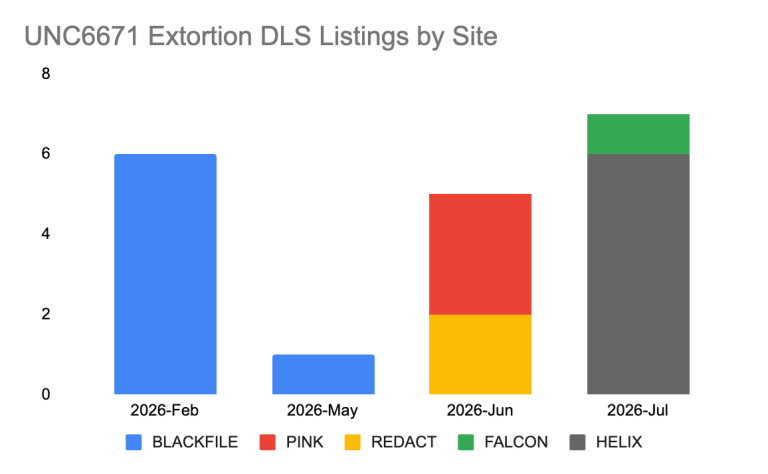
PREY-0058: Microsoft 365 Vishing Attacks Extort Firms A diagram illustrating how Microsoft 365 vishing attacks fuel the PREY-0058 extortion campaign targeting executives.
  • Cybercriminals

PREY-0058: Microsoft 365 Vishing Attacks Extort Firms

Do Son September 9, 2026 0

Discover how the PREY-0058 extortion campaign uses Microsoft 365 vishing attacks and AiTM tactics to bypass MFA, steal cloud data, and demand high ransoms.
CVE-2026-0310: PAN-OS Buffer Overflow Flaw Allows Execute Arbitrary Code with Root Privileges PAN-OS buffer overflow flaw CVE-2026-0310
  • Vulnerability Report

CVE-2026-0310: PAN-OS Buffer Overflow Flaw Allows Execute Arbitrary Code with Root Privileges

Do Son September 9, 2026 0

A new PAN-OS buffer overflow flaw, tracked as CVE-2026-0310, exposes firewalls to remote code execution. Patch your network devices immediately.

Boost Website Speed with Image Optimization: A Practical Guide for Magento Stores tech
  • Technique

Boost Website Speed with Image Optimization: A Practical Guide for Magento Stores

Do Son September 9, 2026 0
Website speed is vital for the success of an online store, as customers want product pages to...
Read More Read more about Boost Website Speed with Image Optimization: A Practical Guide for Magento Stores
Cisco FMC Vulnerabilities Actively Exploited in the Wild Diagram showing Cisco FMC vulnerabilities CVE-2026-20079 and CVE-2026-20316
  • Vulnerability Report

Cisco FMC Vulnerabilities Actively Exploited in the Wild

Do Son September 9, 2026 0

Cisco Talos warns of Cisco FMC vulnerabilities actively exploited in the wild. Attackers chain CVE-2026-20079 and CVE-2026-20316 to deploy ransomware.
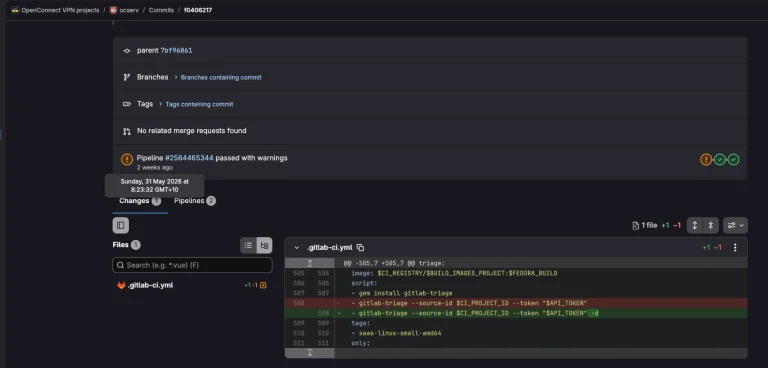
GnuTLS Token Leak Threatens Open Source Supply Chain GnuTLS token leak and GitLab CI artifact exposure code snippet
  • Data Leak

GnuTLS Token Leak Threatens Open Source Supply Chain

Do Son September 9, 2026 0

A critical GnuTLS token leak via a GitLab CI artifact exposure put major Linux distributions at risk. Learn how this supply chain vulnerability occurred.
Streaming Security Risks That Start in the Browser cover_streaming_security_v2
  • Technique

Streaming Security Risks That Start in the Browser

Do Son September 9, 2026 0
Streaming is now part of everyday web use, which also makes it useful cover for attackers. A...
Read More Read more about Streaming Security Risks That Start in the Browser
CVE-2026-85102 & 85103: Check Point VPN Flaws 9.8 CVSS RCE Diagram showing critical Check Point VPN vulnerabilities CVE-2026-85102 and CVE-2026-85103
  • Vulnerability Report

CVE-2026-85102 & 85103: Check Point VPN Flaws 9.8 CVSS RCE

Do Son September 9, 2026 0

Check Point fixed critical Check Point VPN vulnerabilities. Update gateways to prevent remote code execution under CVE-2026-85102 and CVE-2026-85103.
SpyCloud 2026 Identity Threat Report Finds Non-Human Identities Are Now the Leading Path into the Enterprise Logo_Press_Release_1024x720_1788535831W7aLsMTYY5
  • Press Release

SpyCloud 2026 Identity Threat Report Finds Non-Human Identities Are Now the Leading Path into the Enterprise

cybernewswire September 9, 2026 0
Austin, Texas / USA, 9th September 2026, CyberNewswire
Read More Read more about SpyCloud 2026 Identity Threat Report Finds Non-Human Identities Are Now the Leading Path into the Enterprise
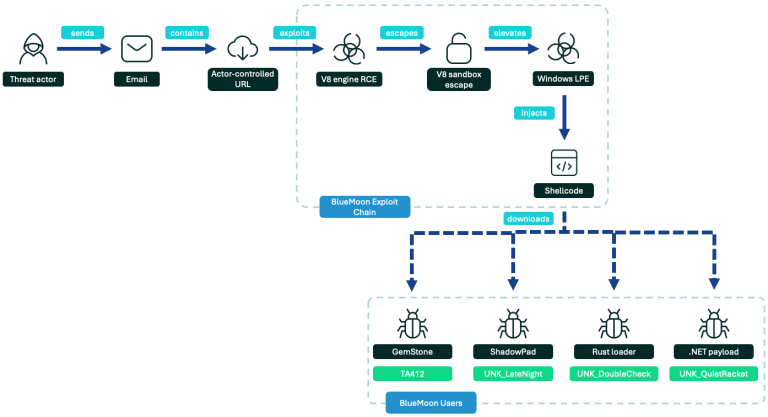
BlueMoon Exploit Kit Chains Chrome and Windows Zero-Days Diagram of BlueMoon exploit kit campaigns deploying the BlueMoon exploit kit against Chrome
  • Cybercriminals

BlueMoon Exploit Kit Chains Chrome and Windows Zero-Days

Do Son September 9, 2026 0

Espionage groups use the BlueMoon exploit kit in new attacks. Discover how BlueMoon exploit kit campaigns exploit Chrome zero-days.
Google Overhauls European Search Engine Results Google European search engine revamp interface and Digital Markets Act compliance changes
  • Technology

Google Overhauls European Search Engine Results

Do Son September 9, 2026 0

Google announces a European search engine revamp to avoid EU Digital Markets Act fines. Discover how these major layout changes downgrade user experience.
Cisco Secure Boot Bypass Details and PoC Exploit Disclosed Cisco Secure Boot bypass vulnerability diagram showing UEFI shell
  • Vulnerability Report

Cisco Secure Boot Bypass Details and PoC Exploit Disclosed

Do Son September 9, 2026 0

Details and PoC for a Cisco Secure Boot bypass vulnerability are public. Learn how this Cisco Secure Boot bypass affects UCS servers and appliances.
September 2026 Android Security Bulletin Fixes Critical System RCE Flaws Critical Android security vulnerabilities addressed in security bulletin
  • Vulnerability Report

September 2026 Android Security Bulletin Fixes Critical System RCE Flaws

Do Son September 9, 2026 0

The September 2026 Android Security Bulletin patches critical RCE flaws like CVE-2026-28604 in the System component. Update to patch level 2026-09-05.
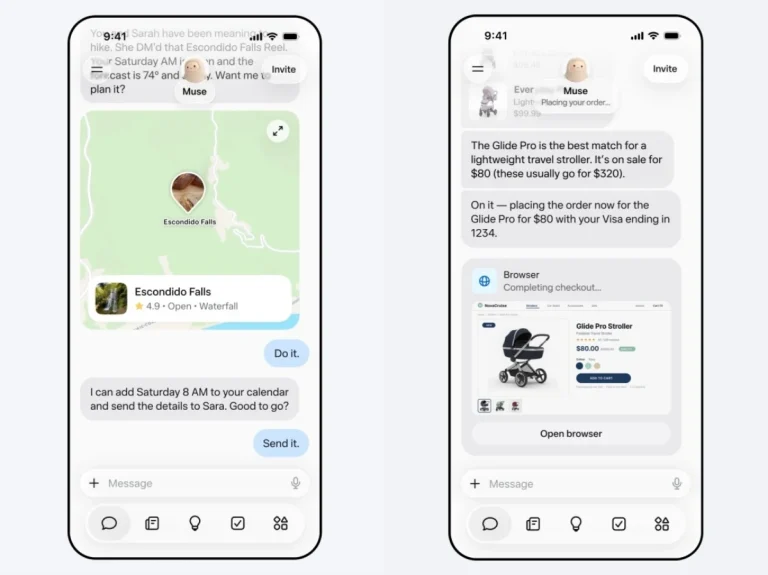
Meta Launches Muse: A Personal AI Agent That Acts on Your Behalf Meta Muse personal AI agent running on Muse Secure VM for autonomous task management
  • Technology

Meta Launches Muse: A Personal AI Agent That Acts on Your Behalf

Do Son September 9, 2026 0

Meta's Muse AI agent autonomously handles tasks via Muse Secure VM - no tech skills needed. Free in the US on iOS, Android, and web.

The Real Cost of a Data Breach vs. Building Security In From Day One Browser fingerprint
  • Technique

The Real Cost of a Data Breach vs. Building Security In From Day One

Do Son September 9, 2026 0

What a data breach actually costs vs. what building security in from day one costs — a line-item comparison for security and IT leaders.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-48383CVSS 10.0
    Adobe Experience Manager is affected by an Incorrect Authorization vulnerability that could result in arbitrary code execution in...
    📅 Updated: Oct 31, 2026
  • CVE-2026-75732CVSS 9.9
    Adobe Experience Manager is affected by an Incorrect Authorization vulnerability that could result in arbitrary code execution in...
    📅 Updated: Oct 31, 2026
  • CVE-2026-83662CVSS 9.3
    Adobe Experience Manager is affected by a reflected Cross-Site Scripting (XSS) vulnerability. An attacker could exploit this vulnerability...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119261CVSS 9.6
    Improper input validation in Skia in Google Chrome prior to 156.0.8078.79 allowed a remote attacker to potentially execute...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119263CVSS 9.6
    Memory corruption in GarbageCollection in Google Chrome prior to 156.0.8078.79 allowed a remote attacker to potentially execute arbitrary...
    📅 Updated: Oct 31, 2026
  • CVE-2026-89078CVSS 9.9
    GitLab has remediated an issue in GitLab CE/EE affecting all versions from 19.2 before 19.2.7, 19.3 before 19.3.3,...
    📅 Updated: Oct 31, 2026
  • CVE-2026-93577CVSS 9.9
    GitLab has remediated an issue in GitLab CE/EE affecting all versions from 19.2 before 19.2.7, 19.3 before 19.3.3,...
    📅 Updated: Oct 31, 2026
  • CVE-2026-110264CVSS 10.0
    An issue has been discovered in GitLab CE/EE affecting all versions from 7.0 before 18.11.13, 19.0 before 19.0.10,...
    📅 Updated: Oct 31, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.