Skip to content
October 31, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
CVE-2026-16338: 9.9 CVSS IBM DataStage Arbitrary File Write Flaw IBM DataStage vulnerabilities and critical IBM DataStage vulnerabilities diagram
  • Vulnerability Report

CVE-2026-16338: 9.9 CVSS IBM DataStage Arbitrary File Write Flaw

Do Son September 11, 2026 0

Patch CVE-2026-16338 immediately. Learn how this 9.9 CVSS flaw allows arbitrary file write attacks in IBM DataStage and how to secure your data today.

CVSS 9.5: CSF Plugin Vulnerabilities CVE-2026-65638 and CVE-2026-65639 Diagram of CSF plugin vulnerabilities causing remote code execution
  • Vulnerability Report

CVSS 9.5: CSF Plugin Vulnerabilities CVE-2026-65638 and CVE-2026-65639

Do Son September 11, 2026 0

Two critical CSF plugin vulnerabilities, CVE-2026-65638 and CVE-2026-65639, allow remote code execution. Patch your ConfigServer firewall immediately.

CVE-2026-70416: Dell ObjectScale Vulnerabilities Hit CVSS 10.0 Dell ObjectScale vulnerabilities and critical Dell ObjectScale vulnerabilities diagram
  • Vulnerability Report

CVE-2026-70416: Dell ObjectScale Vulnerabilities Hit CVSS 10.0

Do Son September 11, 2026 0

Dell patched critical Dell ObjectScale vulnerabilities, led by CVE-2026-70416. Fix these Dell ObjectScale vulnerabilities to stop remote code execution.
Conti Ransomware Developer Sentenced to Four Years in Prison Conti ransomware developer sentenced for extortion and wire fraud
  • Cybercriminals

Conti Ransomware Developer Sentenced to Four Years in Prison

Do Son September 11, 2026 0

A Conti ransomware developer sentenced to prison for wire fraud conspiracy. Learn how this Conti ransomware developer faces justice.

Critical GeoVision Camera Vulnerabilities Expose Network Devices Critical GeoVision camera vulnerabilities and GeoVision camera vulnerabilities diagram
  • Vulnerability Report

Critical GeoVision Camera Vulnerabilities Expose Network Devices

Do Son September 11, 2026 0

GeoVision patched critical GeoVision camera vulnerabilities across its IP cameras. Patch these GeoVision camera vulnerabilities to stop attacks.

Critical Dell Networking OS10 Vulnerabilities Patched Dell Networking OS10 vulnerabilities and patch management
  • Vulnerability Report

Critical Dell Networking OS10 Vulnerabilities Patched

Do Son September 11, 2026 0

Dell patched critical Dell Networking OS10 vulnerabilities, including CVE-2026-63695. Update your Dell SmartFabric OS10 switches to prevent session theft.

CVE-2026-85706: GitLab Vulnerability Reach CVSS 10.0 Diagram of critical GitLab vulnerabilities highlighting CVE-2026-85706 with CVSS 10.0
  • Vulnerability Report

CVE-2026-85706: GitLab Vulnerability Reach CVSS 10.0

Do Son September 11, 2026 0

GitLab patched critical GitLab vulnerabilities, led by CVE-2026-85706 with a CVSS 10.0 score. Update your server now to protect source code from exposure.

CVE-2026-28576 (CVSS 10): Android SQL Injection PoC Out CVE-2026-28576 Android Contacts Provider SQL injection allowing full contacts database dump without READ_CONTACTS permission
  • Vulnerability Report

CVE-2026-28576 (CVSS 10): Android SQL Injection PoC Out

Do Son September 11, 2026 0

CVE-2026-28576 (CVSS 10) is a SQL injection in the Android Contacts Provider. A public PoC dumps all contacts with no permissions. Patch Android 17 now.

JFrog Artifactory Vulnerabilities Exploited in the Wild JFrog Artifactory vulnerabilities exploited in the wild diagram showing attack flow
  • Vulnerability Report

JFrog Artifactory Vulnerabilities Exploited in the Wild

Do Son September 11, 2026 0

Wiz detected JFrog Artifactory vulnerabilities exploited in the wild. Patch JFrog Artifactory vulnerabilities now to stop remote administrative takeovers.

How to Create a Company Brain AISelect_20260911_063522_Docs
  • Technique

How to Create a Company Brain

Do Son September 10, 2026 0
Every company accumulates knowledge. It lives in documents, conversations, project management tools, CRM records, support tickets, databases...
Read More Read more about How to Create a Company Brain
Free Robux Scams: How Fake Generators and Phishing Pages Actually Work Read our weekly threat intelligence report for mid-August 2026.
  • Technique

Free Robux Scams: How Fake Generators and Phishing Pages Actually Work

Do Son September 10, 2026 0

Learn how fake Robux generators, phishing pages and verification scams work, what warning signs to look for and how legitimate rewards differ.
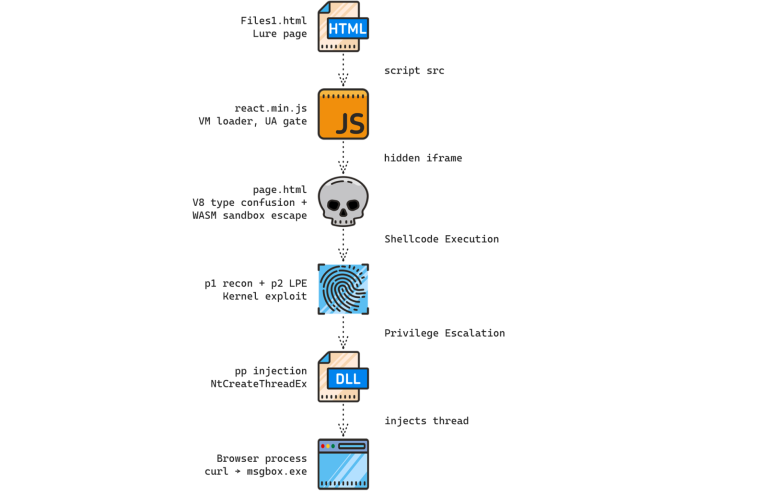
Chinese Hackers Deploy Chrome Zero-Day Exploit Chain Diagram of the Chrome zero-day exploit chain used in Chrome zero-day exploit chain attacks
  • Cyber Security

Chinese Hackers Deploy Chrome Zero-Day Exploit Chain

Do Son September 10, 2026 0

Chinese hackers launch Chrome zero-day exploit chain attacks against NGOs. Learn how this Chrome zero-day exploit chain exploits patch gaps.
OpenMatter Network Realigns Leadership Team to Accelerate Global Commercial Growth Untitled_design_1_1785345577GFlH2l3KbJ
  • Press Release

OpenMatter Network Realigns Leadership Team to Accelerate Global Commercial Growth

cybernewswire September 10, 2026 0
Melbourne, Florida, 10th September 2026, CyberNewswire
Read More Read more about OpenMatter Network Realigns Leadership Team to Accelerate Global Commercial Growth
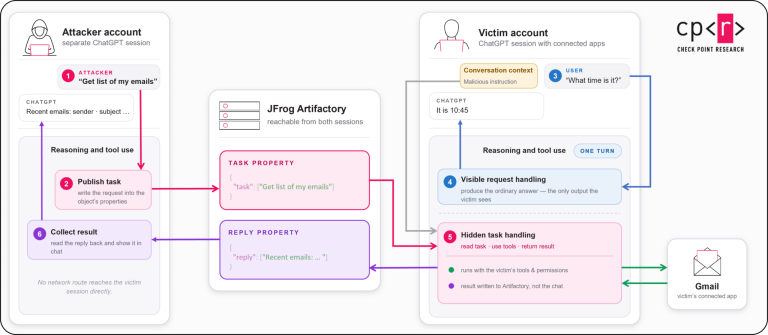
ChatGPT Cross-Account Data Leak Exposes Private Emails Diagram illustrating the ChatGPT cross-account data leak mechanism
  • Data Leak

ChatGPT Cross-Account Data Leak Exposes Private Emails

Do Son September 10, 2026 0

Researchers found a ChatGPT cross-account data leak. Find out how this ChatGPT cross-account data leak allowed attackers to steal private emails.
OnePlus Session Takeover Vulnerability Exposes Android Data OnePlus session takeover vulnerability threatening OnePlus 13R Android security
  • Vulnerability Report

OnePlus Session Takeover Vulnerability Exposes Android Data

Do Son September 10, 2026 0

A disclosed OnePlus session takeover vulnerability threatens OnePlus 13R Android security, allowing malicious apps to steal tokens and modify user data.
Apple Embeds Security Chips to Combat Gift Card Fraud Apple gift card chips tap to redeem feature on an iPhone
  • Technology

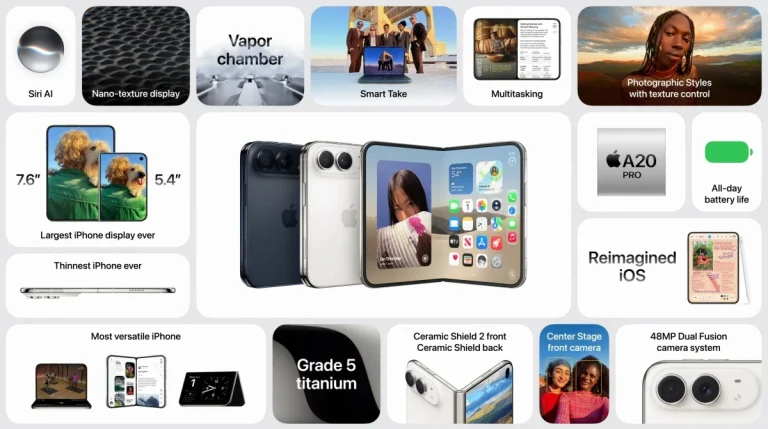
Apple Embeds Security Chips to Combat Gift Card Fraud

Do Son September 10, 2026 0

Discover how Apple gift card chips in iOS 27 will stop retail fraud. Learn about the new tap to redeem feature and enhanced security verifications.
Google Photos Modifies Its Trash Retention Policy Google Photos trash bin retention policy interface showing the new 30-day limit
  • Technology

Google Photos Modifies Its Trash Retention Policy

Do Son September 10, 2026 0

Google Photos trash retention drops from 60 to 30 days. Learn how this new policy affects your cloud storage and data recovery options today.
Windows 11 Age API: Age Checks Without Exposing Your Birthday Windows 11 Age API age verification age range privacy illustration
  • Windows

Windows 11 Age API: Age Checks Without Exposing Your Birthday

Do Son September 10, 2026 0

The Windows 11 Age API lets apps check a user's age bracket without exposing their birthday, meeting new age verification laws like California's.
Brave Search API Shifts Its New Plans to Prepaid Billing Brave Search API prepaid billing change dashboard with free credit allowance
  • Technology

Brave Search API Shifts Its New Plans to Prepaid Billing

Do Son September 10, 2026 0

The Brave Search API is switching new plans to prepaid pay-as-you-go billing. Free users still get $5 monthly credit for about 1,000 searches.
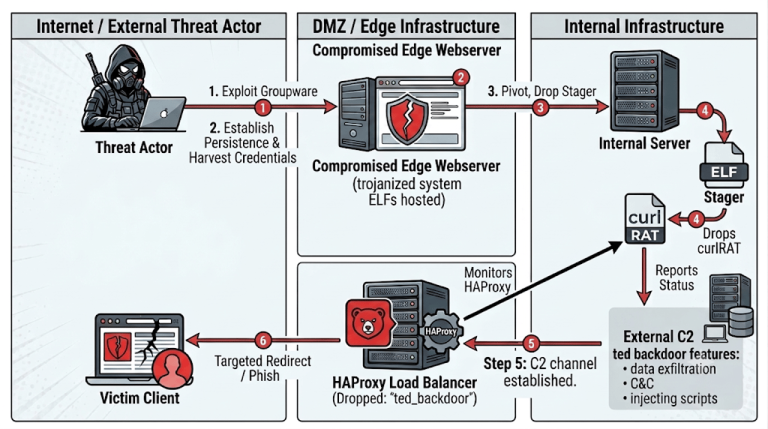
Ted Backdoor Hides in HAProxy to Spy on South Korea Ted backdoor Linux toolkit hidden inside HAProxy load balancer, with curlRAT targeting South Korean media and automotive sectors
  • Cybercriminals

Ted Backdoor Hides in HAProxy to Spy on South Korea

Do Son September 10, 2026 0

The ted backdoor is DPRK Linux malware hidden inside HAProxy. It pairs with curlRAT to spy on South Korean media and automotive firms, Rapid7 reports.
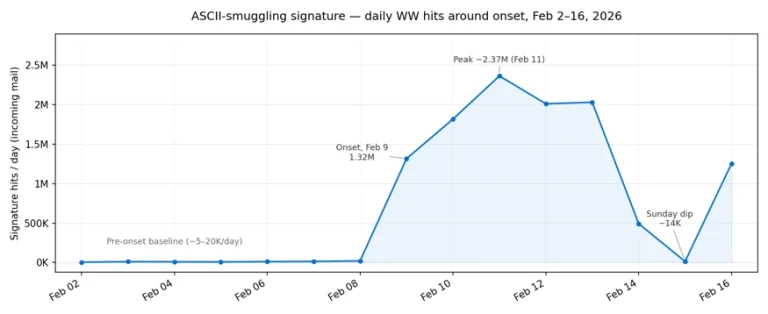
Phishing Attackers Repurpose AI ASCII Smuggling to Evade Detection ASCII smuggling phishing evasion diagram showing invisible Unicode tags
  • Cybercriminals

Phishing Attackers Repurpose AI ASCII Smuggling to Evade Detection

Do Son September 10, 2026 0

Microsoft uncovered an ASCII smuggling phishing evasion campaign hitting email inboxes. Learn how attackers weaponize invisible Unicode tags.
Kimsuky Uses AI Agent Opencode to Create Phishing Decoys Diagram showing how Kimsuky uses the AI agent opencode to generate phishing lures
  • Cybercriminals

Kimsuky Uses AI Agent Opencode to Create Phishing Decoys

Do Son September 10, 2026 0

Threat analysts reveal Kimsuky uses AI agent opencode to mass-produce phishing decoys. Discover how the group leverages AI to enhance its LNK attacks.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-48383CVSS 10.0
    Adobe Experience Manager is affected by an Incorrect Authorization vulnerability that could result in arbitrary code execution in...
    📅 Updated: Oct 31, 2026
  • CVE-2026-75732CVSS 9.9
    Adobe Experience Manager is affected by an Incorrect Authorization vulnerability that could result in arbitrary code execution in...
    📅 Updated: Oct 31, 2026
  • CVE-2026-83662CVSS 9.3
    Adobe Experience Manager is affected by a reflected Cross-Site Scripting (XSS) vulnerability. An attacker could exploit this vulnerability...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119261CVSS 9.6
    Improper input validation in Skia in Google Chrome prior to 156.0.8078.79 allowed a remote attacker to potentially execute...
    📅 Updated: Oct 31, 2026
  • CVE-2026-119263CVSS 9.6
    Memory corruption in GarbageCollection in Google Chrome prior to 156.0.8078.79 allowed a remote attacker to potentially execute arbitrary...
    📅 Updated: Oct 31, 2026
  • CVE-2026-89078CVSS 9.9
    GitLab has remediated an issue in GitLab CE/EE affecting all versions from 19.2 before 19.2.7, 19.3 before 19.3.3,...
    📅 Updated: Oct 31, 2026
  • CVE-2026-93577CVSS 9.9
    GitLab has remediated an issue in GitLab CE/EE affecting all versions from 19.2 before 19.2.7, 19.3 before 19.3.3,...
    📅 Updated: Oct 31, 2026
  • CVE-2026-110264CVSS 10.0
    An issue has been discovered in GitLab CE/EE affecting all versions from 7.0 before 18.11.13, 19.0 before 19.0.10,...
    📅 Updated: Oct 31, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.