
 Do Son
Microsoft has announced that it is officially opening its internal Xbox Game Publishing Guide to the public—a...
Latest news

To comply with the EU Digital Markets Act (DMA), Meta has announced that WhatsApp will soon become...

Amazon has announced that its satellite communications initiative, formerly known as Project Kuiper, will be officially rebranded...

Sender Policy Framework (SPF) is a vital component of modern email authentication protocols, designed to combat email...

The Symfony project has released security updates to address a newly disclosed vulnerability affecting its widely used...

A newly disclosed high-severity vulnerability in the Cisco Catalyst Center Virtual Appliance could allow attackers with low-level...

Apple has announced the launch of a new App Store Mini Apps Partner Program, offering reduced fees...
“Is it working?” It can be easy to drop an AI SOC agent into your environment and...

Cybersecurity firms are sounding the alarm over a critical vulnerability in Fortinet FortiWeb, the company’s Web Application...
ASUS has released an urgent security advisory addressing a critical authentication bypass vulnerability affecting several models in...

Tracked as UNC5537, this financially motivated threat actor has systematically compromised hundreds of Snowflake customer accounts

CVE-2024-5452 enables attackers to remotely manipulate the entire application state, potentially leading to complete system takeover

Mustang Panda has been conducting a series of targeted attacks since April 2024, focusing on entities with interests in tax compliance and education

A newly released proof-of-concept (PoC) exploit has heightened concerns about a critical vulnerability (CVE-2024-29849)

A security researcher has published a proof-of-concept (PoC) exploit code targeting a recent important severity vulnerability (CVE-2024-30043)

A surge in cyber activity associated with the Sticky Werewolf group, a threat actor with suspected geopolitical or hacktivist ties
A series of critical vulnerabilities in the popular Netgear WNR614 N300 router, exposing users to significant security risks

A new variant of an ongoing cryptojacking campaign targeting misconfigured Kubernetes clusters has been uncovered
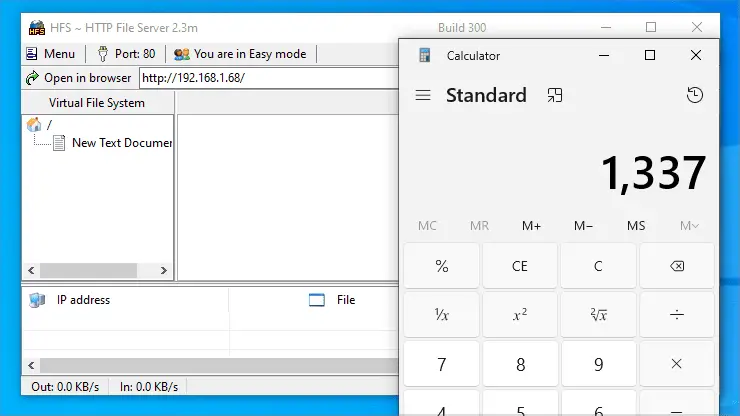
A critical vulnerability, identified as CVE-2024-23692, has been discovered in Rejetto HTTP File Server (HFS) versions 2.x

FortiGuard Labs has recently identified a new phishing campaign deploying a variant of the notorious Agent Tesla malware

Bitdefender, a leading cybersecurity provider, has addressed a vulnerability (CVE-2024-4177) in its GravityZone Console On-Premise product

eSentire's Threat Response Unit (TRU) has unveiled a persistent and sophisticated cyber campaign employing the notorious more_eggs malware

A critical vulnerability (CVE-2024-5480) has been discovered in PyTorch's distributed RPC (Remote Procedure Call) framework

TRU has unveiled a sophisticated attack campaign utilizing counterfeit KMSPico activators to deliver the notorious Vidar Stealer malware

chip design giant Arm has disclosed a critical zero-day vulnerability (CVE-2024-4610) actively being exploited in the wild

watchTowr published the technical details and a PoC exploit code for a recently disclosed critical vulnerability (CVE-2024-4577) in PHP

The vulnerability, tracked as CVE-2024-4577, could potentially allow unauthenticated attackers to take full control of affected PHP servers

Sophos researchers have uncovered a sophisticated and long-running cyberespionage campaign, dubbed Operation Crimson Palace

The attack begins with hackers compromising websites and inserting malicious code, often through the legitimate WordPress plugin "Hustle."

CVE-2023-33246 in RocketMQ versions 5.1.0 and below, allowing attackers to remotely execute code and download the notorious Muhstik malware
The vulnerabilities, tracked as CVE-2024-20404 and CVE-2024-20405, could be exploited by unauthenticated, remote attackers to carry out SSRF and stored XSS attacks

Researchers have identified a concerning resurgence of attacks targeting known vulnerabilities in the ThinkPHP web application framework