
 Do Son
Qualcomm has announced the launch of its first processor series designed specifically for industrial-grade computers (Industrial PCs,...
Latest news

OpenAI has announced the release of GPT-5.1, a major revision within the GPT-5 generation, designed not only...

Apple has recently released the macOS Tahoe 26.2 Developer Beta, within which a new feature known as...

Microsoft is gradually weaving a wide range of artificial intelligence capabilities into Windows 11, with the most...

The Socket Threat Research Team has uncovered a highly sophisticated malicious Chrome extension posing as an Ethereum...

NVIDIA has released an important security update for its NeMo Framework, addressing two high-severity vulnerabilities that expose...

The Amazon Threat Intelligence team has uncovered a highly sophisticated threat campaign exploiting multiple zero-day vulnerabilities in...

A new malware distribution trend is emerging across the macOS threat landscape, according to fresh research from...

Zoho Corporation has released an urgent security advisory addressing a critical severity SQL injection vulnerability affecting Analytics...

Microsoft has patched a newly disclosed local privilege escalation (LPE) vulnerability affecting the Host Process for Windows...

Trustwave SpiderLabs has uncovered a dangerous cyberattack campaign targeting users of the popular network scanning tool, Advanced IP Scanner

ReversingLabs researchers uncovered a malicious open-source package on the Python Package Index (PyPI) called xFileSyncerx

RansomHub attackers gained initial access by exploiting the Zerologon vulnerability (CVE-2020-1472), which grants domain administrator privileges

Cybersecurity researchers have uncovered a novel cryptojacking campaign dubbed "Commando Cat," actively targeting Docker Remote API servers

The impact of CVE-2024-5171 and CVE-2024-5197 is significant due to the widespread use of libaom and libvpx in various applications

A CoinMiner, a type of malware that hijacks systems to mine cryptocurrency, unwittingly left a backdoor open

A massive DNS probing operation, dubbed "Secshow," has been underway since June 2023, targeting open DNS resolvers worldwide

ASEC has recently identified a phishing campaign leveraging HTML files distributed via email to execute malicious commands on targeted systems

This vulnerability, designated as CVE-2024-4295, carries a severity rating of 9.8 (CVSS), making it a prime target for exploitation

Kali Linux, the renowned open-source, Debian-based Linux distribution, has officially released its latest version, Kali Linux 2024.2

Trend Micro's threat-hunting team has uncovered a new Linux variant of the TargetCompany ransomware, marking a significant escalation

Parrot OS 6.1 brings a slew of improvements and upgrades designed to bolster system performance, stability, and security
In a recent wave of cyberattacks, TikTok has confirmed a zero-day vulnerability within its direct messaging system has been exploited
Security researcher published the technical details and a proof-of-concept (PoC) code for a vulnerability, identified as CVE-2023-3390
CVE-2024-36522 discovered in earlier versions of Apache Wicket, stemmed from a potential XSLT injection attack, enabling malicious actors to RCE
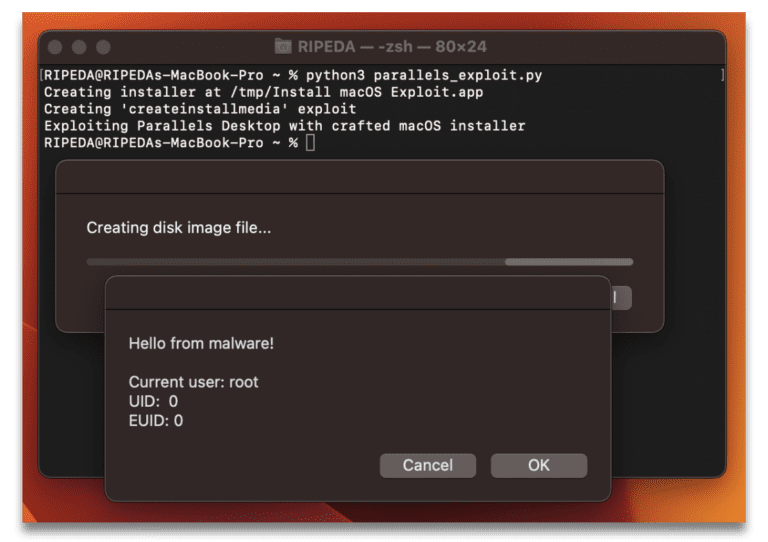
The technical details and a proof-of-concept (PoC) exploit code for a vulnerability (CVE-2024-34331) in Parallels Desktop for Mac

UNC1151 employed DLL loaders that downloaded an encrypted JPG file, which was then decrypted to deploy a final payload executable.
Successful exploitation of the CVE-2024-4332 vulnerability could lead to unauthorized information disclosure or modification

Security researcher Zeyad Azima has recently published a proof-of-concept exploit code for the CVE-2024-27348 vulnerability

Tenable Research has uncovered a significant vulnerability within Microsoft Azure's Service Tags functionality

Due to the critical severity of vulnerabilities CVE-2024-29972, CVE-2024-29973, and CVE-2024-29974, Zyxel has made patches available

A security researcher has published details and proof-of-concept (PoC) code for a macOS CVE-2024-27822 vulnerability