
 Do Son
Researchers from the AhnLab Security Intelligence Center (ASEC) have uncovered a new malware campaign exploiting Remote Monitoring...
Latest news

Google has released an important security update for Chrome Stable Channel, addressing a high-severity vulnerability in the...

Broadcom has announced a strategic partnership with the AI startup CAMB.AI to jointly develop an entirely new...

Apache OpenOffice has released a crucial security patch, version 4.1.16, to address a flurry of security vulnerabilities...

The Apache Software Foundation (ASF) has released an important security update for Apache OFBiz, its open-source enterprise...

Microsoft has released its November 2025 Patch Tuesday, addressing a total of 68 vulnerabilities, including a high-priority...

Milvus, a leading open-source vector database that powers AI and large-scale search applications, has disclosed a critical...

Rockwell Automation has released a critical security advisory addressing a severe privilege escalation vulnerability (CVE-2025-11862, CVSS 9.9)...

Meta’s AI FAIR team has unveiled a groundbreaking achievement in the field of Automatic Speech Recognition (ASR)...

According to the latest reports, Samsung has reportedly made last-minute adjustments to the physical dimensions of the...
Critical Security Advisory: Mitel MiCollab Vulnerabilities Exposed (CVE-2024-35285 & CVE-2024-35286)
Critical Security Advisory: Mitel MiCollab Vulnerabilities Exposed (CVE-2024-35285 & CVE-2024-35286)
The vulnerabilities, tracked as CVE-2024-35285 and CVE-2024-35286, have been assigned the highest severity rating of 9.8 on the CVSS

Netskope Threat Labs has revealed a disturbing trend of malicious actors exploiting Cloudflare Workers to launch sophisticated phishing campaigns

The flaw, designated as CVE-2024-5274 (CVSS 8.8), was recently patched by Google after being exploited in the wild

In a parallel effort, Sharp Dragon targeted governmental organizations in the Caribbean, using compromised networks from Southeast Asia

The vulnerability, designated CVE-2024-26289 and assigned a CVSS score of 9.8 (critical), stems from the deserialization of untrusted data

CVE-2024-5035 allows for remote code execution (RCE) due to command injection and buffer overflow issues in the rftest binary

In the cybersecurity field, web application firewalls (WAFs) are pivotal in defending web applications from malicious attacks....

Forcepoint X-Labs has issued an urgent warning regarding a surge in sophisticated phishing emails targeting government departments across the APAC region

Technical details and a proof-of-concept (PoC) exploit code have emerged about a security flaw (CVE-2024-2961) in GNU C Library

Experts have exposed a new ransomware threat named ShrinkLocker, which cleverly exploits Microsoft's built-in BitLocker encryption tool

Security researcher Guillaume André with Synacktiv has detailed a high-severity vulnerability, CVE-2024-26238 (CVSS 7.8)

NetbyteSEC Detecx (NBS) team exposed a sophisticated malware campaign orchestrated by the notorious SharpPanda APT group

Google Cloud has publicly addressed an incident in which a misconfiguration during the setup of a GCVE private cloud

In addition to CVE-2024-27842, Wang Tielei has also released a PoC exploit for CVE-2023-40404, a privilege escalation flaw in macOS Sonoma

Mandiant has revealed a concerning trend among China-linked cyber espionage groups: the use of ORB networks to enhance their espionage capabilities

CVE-2024-25737 and CVE-2024-25738, are both rated with a high CVSS score of 9.1, indicating the potential for significant damage if exploited

CatDDoS-related gangs have leveraged a wide array of vulnerabilities across multiple vendor devices like Apache, Cisco, D-Link, Huawei, ...

The researchers likened the analysis of Unfading Sea Haze's malware arsenal to a "museum exposition of cyberespionage relics,"

One of the most notable aspects of CLOUD#REVERSER is its use of Google Drive and Dropbox for C2 communication and data exfiltration
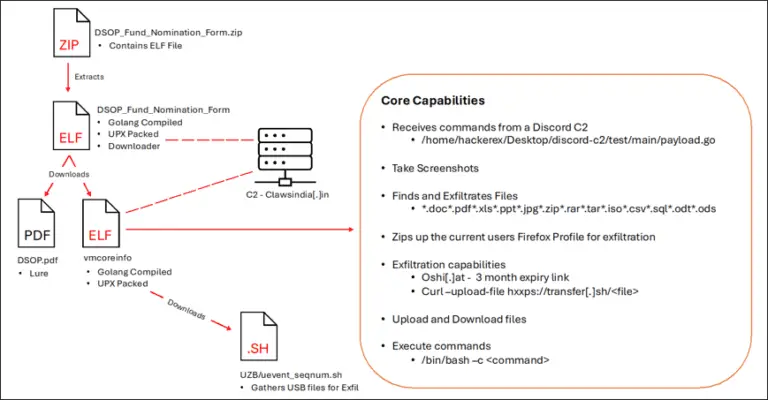
Researchers revealed a sustained campaign by Pakistani-based cyber espionage group APT36 targeting critical Indian government
Data governance and cybersecurity are closely connected. As a vital part of cybersecurity mechanisms, solutions, and actions,...

Security researcher Matthias Gerstner has discovered a critical vulnerability (CVE-2024-5148) in GNOME Remote Desktop