
 Do Son
Analysts at GreyNoise Intelligence have reported a sharp, coordinated surge in attacks exploiting vulnerabilities across PHP and...
Latest news

The national incident response team CERT Polska has uncovered a new strain of Android-based NFC relay malware,...

Researchers from Trustwave SpiderLabs’ Cyber Threat Intelligence team have identified the formation of a new federated threat...
The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has added two new vulnerabilities—CVE-2025-11371 in Gladinet CentreStack and...

Google has begun introducing deeper Gemini model integration into its Google Translate service. In the latest version...

The RedDrip team at QiAnXin Threat Intelligence Center has released a new report detailing a multi-year series...

A newly disclosed critical vulnerability (CVE-2025-11953, CVSS 9.8) in the React Native Community CLI exposes developers to...

A critical-severity Local File Inclusion (LFI) flaw in the popular WordPress plugin ShopLentor – WooCommerce Builder for...

 cybernewswire
Delaware, United States, 4th November 2025, CyberNewsWire


IBM has announced its definitive agreement to acquire HashiCorp Inc., a leader in multi-cloud infrastructure automation

In the latest wave of tech-sector layoffs, Google has made significant cuts to teams working on key development tools like Flutter, Python

A serious security vulnerability (CVE-2024-32656) foun in Ant Media Server, a popular streaming solution used by thousands of organizations
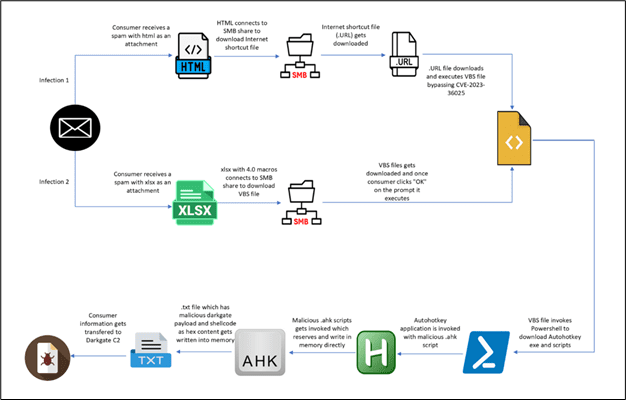
DarkGate, identified as a Remote Access Trojan (RAT), poses a formidable threat due to its array of functionalities including data theft

Researchers from HiddenLayer have discovered a significant vulnerability in the R programming language, tracked as CVE-2024-27322

Threat research team has identified a sophisticated new Remote Access Trojan (RAT) targeting Android devices

Modzero unveiled a series of severe vulnerabilities in MailCleaner, a widely-used email filtering appliance designed to protect against spam

If left unpatched, the CVE-2024-33891 (CVSS 8.8) vulnerability allows attackers to bypass authentication completely

Akamai security researchers highlight the shocking scale of phishing scams impersonating the United States Postal Service (USPS)
Avast has been hit with a hefty $14.8 million fine by the ÚOOÚ for alleged violations of the European Union's General Data Protection Regulation (GDPR)
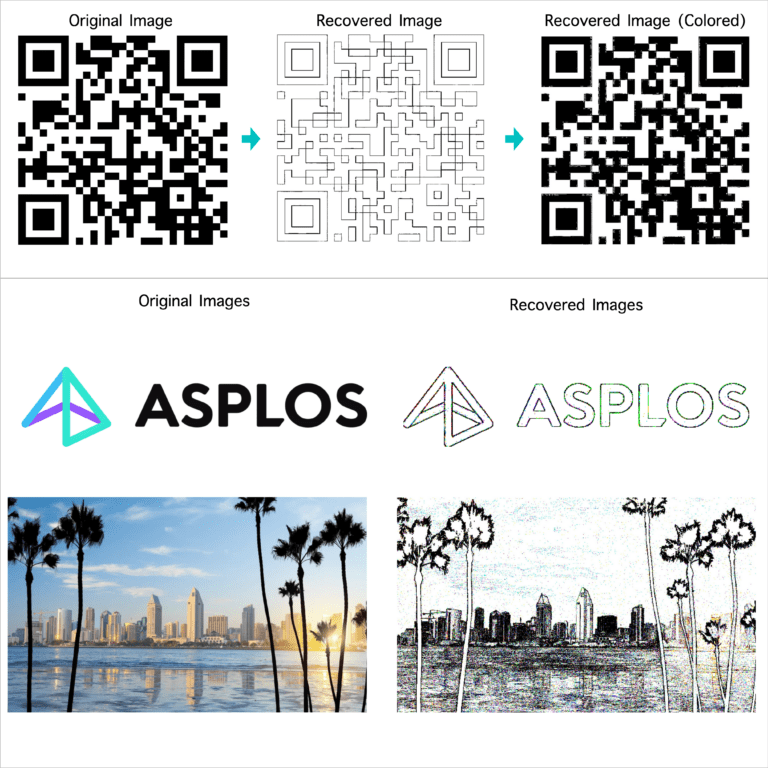
The Pathfinder attack exposes two high-resolution side-channel attacks leveraging the Conditional Branch Predictor (CBP)

CVE-2024-32766 (CVSS 10) is an OS command injection, a technique where attackers can send malicious commands to a vulnerable system

The vulnerability, now patched, resided in Telegram's "Mini App" system. These mini web applications, designed to run within Telegram

Cybersecurity researcher shared technical details and PoC exploit for a high-severity EoP flaw (CVE-2024-26218) bug affecting Windows Kernel.

Cato Networks reported intercepting several attempts aimed at installing the XMRig cryptocurrency mining malware using this vulnerability

troubling cyber campaign, dubbed FROZEN#SHADOW, threat actors have leveraged the relatively unknown SSLoad malware

Sources within Google reveal that the company recently laid off its dedicated Python maintenance team.

Mitel's Security Bulletin 24-0011-001 details a critical stored XSS vulnerability in the Ignite component of MiContact Center Business

Security researcher has released PoC exploit code for CVE-2024-21345, a high-severity Windows Kernel Elevation of Privilege vulnerability

Security experts at eSentire have sounded the alarm on a new wave of FakeBat malware attacks. Threat actors are refining their methods

Security researchers have sounded the alarm, cutting through misinformation to expose a dangerous new development in the LightSpy malware

A serious security vulnerability in Webmin, a widely used web-based system administration tool for Unix-like servers, has been discovered