
 Do Son
Koi Security has uncovered a massive supply-chain campaign dubbed PhantomRaven, which has silently infected the npm ecosystem...
Latest news

Beijing-based XLab has unveiled the discovery of RPX_Client, a previously undocumented module linked to the PolarEdge ORB...

Palo Alto Networks’ Unit 42 Threat Intelligence team has uncovered a sophisticated new malware family dubbed Airstalk,...

The Symantec Threat Hunter Team has uncovered two major cyber intrusions in Ukraine attributed to Russian-aligned threat...

Progress Software Corporation has issued a security advisory warning of a high-severity vulnerability in its MOVEit Transfer...

 cybernewswire
Silver Spring, USA/ Maryland, 30th October 2025, CyberNewsWire

Microsoft recently released its Q1 FY2026 financial results, revealing that surging demand for cloud and AI services...

Shortly after last week’s large-scale AWS outage, Microsoft’s Azure cloud platform also experienced a significant service disruption,...

OpenAI has officially announced the expansion of its AI video creation platform, Sora App, into the Asian...

Earlier in 2025, OpenAI released its own open-source artificial intelligence models, namely GPT-OSS-20B and GPT-OSS-120B, both of...

Check Point Research has lifted the veil of anonymity surrounding two cybercrime actors responsible for recent Agent Tesla malware campaigns

VMware has released critical security patches to address multiple vulnerabilities in its SD-WAN (Software-Defined Wide Area Network) solution
A new report highlights a disturbing increase in targeted phishing attacks launched by a loosely affiliated group of cybercriminals

The flaw, designated CVE-2024-3159, involves an out-of-bounds memory access vulnerability in the V8 JavaScript engine.

A new report from McAfee Labs reveals a troubling evolution in the PikaBot malware campaign, showcasing an alarming range of infection vectors
The vulnerability, designated CVE-2024-2879 with a CVSS score of 9.8, could allow unauthenticated attackers to inject malicious SQL code

A newly updated variant of the StrelaStealer malware is actively targeting organizations across Europe, according to a recent report
The flaw, designated as CVE-2024-2389, could give attackers unfettered access to sensitive network infrastructure.

The flaw, tracked as CVE-2024-29834, enables unauthorized users to make changes to sensitive data streams and system access rules.
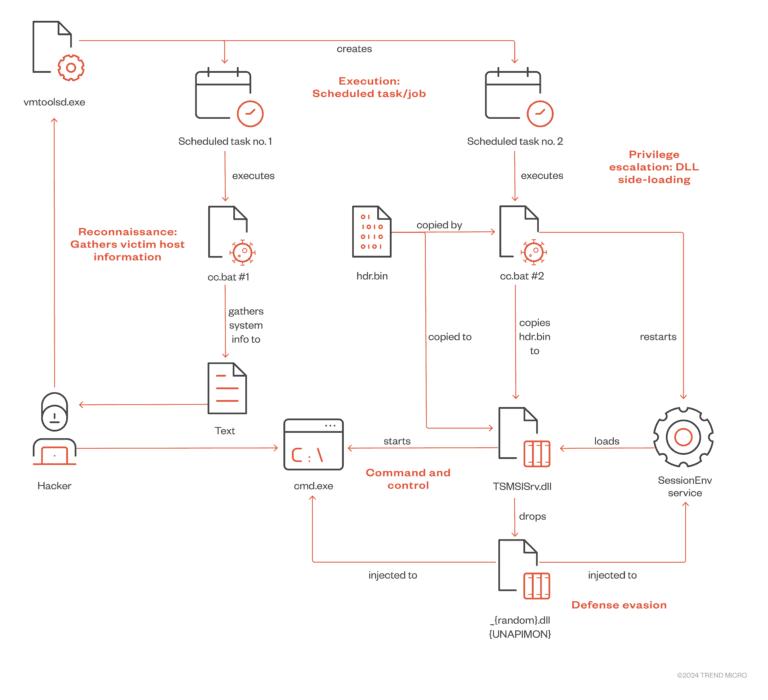
In a cyberespionage campaign attributed to Earth Freybug, security researchers from Trend Micro observed a unique malware, dubbed UNAPIMON

Octopus Deploy has released a security advisory and subsequent patches to address a critical vulnerability (CVE-2024-2975

The most serious of these vulnerabilities (CVE-2024-21473) carries a CVSS score of 9.8 and could allow attackers to corrupt device memory

JumpServer has recently been found to contain CVE-2024-29201 and CVE-2024-29202 that could allow attackers to execute arbitrary code remotely

Successful exploitation of CVE-2023-6154 (CVSS 7.8) requires the attacker to have local access to the target machine.

A new report released by AhnLab Security Intelligence Center (ASEC) uncovers a disturbing tactic hackers are using to spread malware
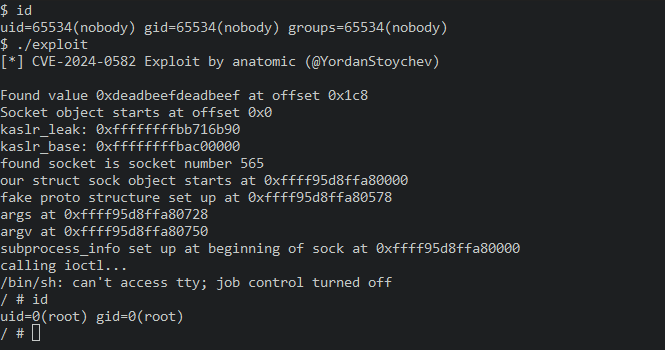
Researchers have provided a detailed analysis of the CVE-2024-0582 vulnerability, including a proof-of-concept (PoC) exploit

In a startling discovery, the Phylum Research Team has exposed a malicious npm package masquerading as a legitimate toolkit

CVE-2024-23538 and CVE-2024-23539: These vulnerabilities stem from improper neutralization of special elements used in an SQL command

Cisco has issued a critical warning about a widespread password spraying campaign targeting Remote Access VPN (RAVPN)

A report by CyberArk reveals a sinister trend: the rise of 'infostealer' malware specifically designed to steal web session cookies.

The CVE-2024-27281 vulnerability could allow attackers to execute arbitrary code remotely on systems using affected versions of RDoc
A severe backdoor vulnerability (designated CVE-2024-3094) has been unearthed in versions 5.6.0 and 5.6.1 of the widely used XZ