
 Do Son
When users subscribe to iCloud, their photo libraries can be automatically uploaded in the background without any...
Latest news

Microsoft Bing Wallpaper is a desktop application developed by Microsoft, designed around Bing’s Image of the Day...

 cybernewswire
London, United Kingdom, 27th October 2025, CyberNewsWire

According to a report by The Information, following its ventures into text, image, and video generation, OpenAI...
 Dan Agbo
Sergei Beliachkov, who managed security for 7,000+ users as a virtual CISO and later launched the service...

Google has recently introduced a powerful new feature for Canvas, the free interactive workspace built into its...

According to reports, as processor performance continues to advance, Apple is planning to integrate the vapor chamber...

Amazon recently unveiled two cutting-edge innovations designed for its operations network—the “Blue Jay” multi-arm robotic collaboration system...

In his latest Power On newsletter, Bloomberg journalist Mark Gurman revealed that Apple’s plans to expand its...

The European Commission has formally accused Meta (parent company of Facebook and Instagram) and TikTok of violating...

Magnet Goblin is a financially motivated threat actor demonstrating proficiency in swiftly exploiting 1-day software vulnerabilities

Hong Kong is facing an increasingly complex phishing threat landscape. Hackers are employing sophisticated techniques to impersonate banks

The Balada Injector campaign, a sophisticated malware operation, has set its sights on exploiting a vulnerability within the WordPress plugin

Kontrol and Elock locks, both utilizing firmware from the company Sciener, have been found riddled with security vulnerabilities

While India faces a surge in these pig-butchering scams, the phenomenon is not confined by geography. Similar tactics have been deployed in Taiwan

NarniaRAT boasts information-stealing capabilities and swiftly conscripts the compromised machine into the Fenix Botnet.

CVE-2023-42662: Exposure of Access Tokens (CVSS 9.3) Rated critical, this flaw compromises Artifactory's Single Sign-On (SSO) feature

CVE-2024-2044 in pgAdmin 4 could have allowed a remote, authenticated attacker to execute arbitrary code on affected systems

A severe security vulnerability (CVE-2024-28222) has been uncovered in Veritas NetBackup, the widely used enterprise backup solution

The fallout from the devastating hacker attack on IT provider Xplain continues as the NCSC publishes a detailed report on the leaked data

A flaw (CVE-2024-27295) was found in Directus, a versatile open-source content management platform favored by developers
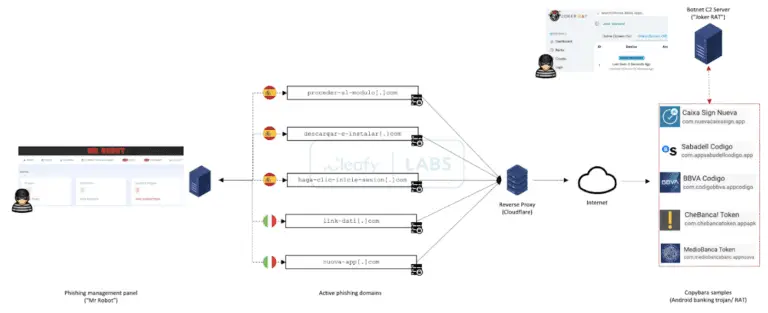
Copybara campaign unfolds in a series of meticulously executed stages. TAs are weaponizing a combination of social engineering, phishing infrastructure

Akamai offers a proof-of-concept (PoC) Theme file and video, aiding in understanding and replicating the CVE-2024-21320 vulnerability.

Attackers are becoming increasingly adept at weaponizing trusted resources and services, as seen in a recent Python-based infostealer campaign

A vulnerability (CVE-2024-25111, CVSS 8.6) has been uncovered that could allow malicious actors to cripple Squid-powered systems

TA4903 cybercriminal group has displayed a consistent pattern of sophisticated phishing tactics in pursuit of sensitive corporate data

A newly discovered critical vulnerability (CVE-2024-27917) in Shopware 6, a widely used open-source e-commerce platform

Cado Security Labs' recent discovery exposed a complex malware campaign zeroing in on Linux servers misconfigured with popular cloud services

Qualcomm has released a security bulletin this month, patching 16 flaws – including two critical flaws (CVE-2023-28578 and CVE-2023-28582)

The proof of concept (PoC) for exploiting CVE-2024-27302 is alarmingly straightforward, underscoring the vulnerability's severity

Japanese school uniform retailer Kanko Online Shop has disclosed a data breach affecting its Kanko Online Shop Harajuku Select Square

GhostSec aims to fund further operations, leveraging a variety of tactics from ransomware to DoS attacks to achieve their objectives.