
 Do Son
The well-known online forum Reddit has announced legal action against Perplexity, SerApi, OxyLabs, and AWMProxy, accusing these...
Latest news

Renowned analyst Ming-Chi Kuo recently released a supply chain report revealing that sales of Apple’s newly launched...

Earlier this month, Microsoft released a Windows 11 cumulative update addressing several known feature issues and security...

The fierce standoff between Apple and the European Union over the Digital Markets Act (DMA) has officially...

With the rapid advancement and widespread adoption of cutting-edge AI generation tools such as OpenAI’s Sora 2,...

The Internet Systems Consortium (ISC) has issued patches for three high-severity vulnerabilities impacting the BIND 9 DNS...

Atlassian has released patches addressing a high-severity Path Traversal vulnerability (CVE-2025-22167) affecting Jira Software Data Center and...
Symantec Exposes Chinese APT Overlap: Zingdoor, ShadowPad, and KrustyLoader Used in Global Espionage

Symantec Exposes Chinese APT Overlap: Zingdoor, ShadowPad, and KrustyLoader Used in Global Espionage
Symantec’s investigation uncovered a complex web of interconnected Chinese espionage operations, with infrastructure and tooling overlapping multiple...

Researchers from Socket’s Threat Research Team have uncovered an active homoglyph typosquat on NuGet impersonating the widely...

Security researcher Batuhan Er from HawkTrace has detailed a critical remote code execution (RCE) vulnerability in Microsoft...

The campaign investigated demonstrates Turla's focus on targeted attacks. This 'Pelmeni Wrapper' loads the next stage payload.
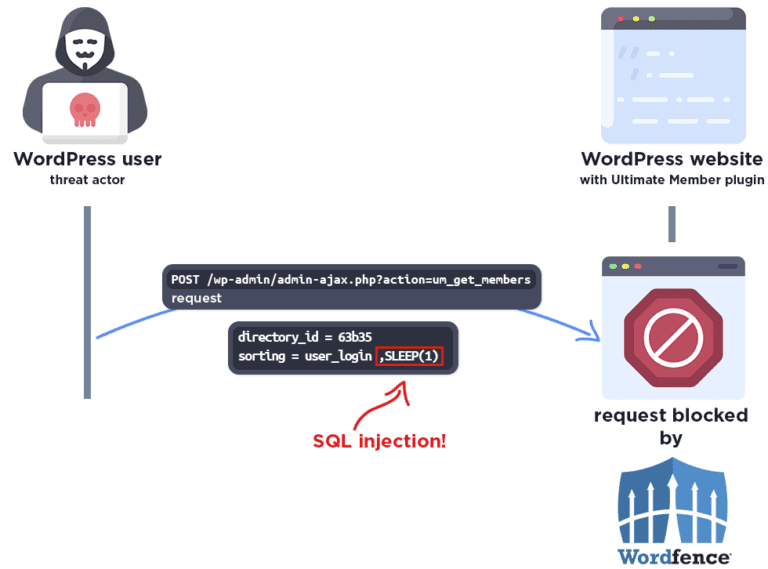
CVE-2024-1071 (CVSS 9.8), underscoring the grave risk it poses to websites utilizing this widely adopted plugin

The recently disclosed vulnerabilities in ScreenConnect (CVE-2024-1709, CVE-2024-1708) necessitate immediate action

In an era where digital transactions are ubiquitous, the significance of safeguarding these interactions cannot be overstated....

A high-severity vulnerability, designated CVE-2024-26582, has been discovered within the Transport Layer Security subsystem of the Linux kernel

The CVE-2024-23204 vulnerability existed in macOS and iOS devices running versions before macOS Sonoma 14.3, iOS 17.3, and iPadOS 17.3

VOLTZITE, a threat group known for persistent targeting of global critical infrastructure sectors, continues to refine its methods

The notorious 8220 Gang has resurfaced, targeting cloud infrastructure in a campaign demonstrating significant advancements

Researchers at Talos and CERT.NGO have pulled back the curtain on new malicious components deployed by the notorious Turla APT group

Trustwave SpiderLabs' Email Security team has uncovered a sophisticated Phishing-as-a-Service (PaaS) platform known as Tycoon Group

CVE-2024-23349 in the way Apache Answer handles question summaries could allow malicious actors to embed harmful code

The primary malware, dubbed "TrollAgent," was a data thief developed in GoLang and capable of stealing a wide array of information

Lucifer DDoS botnet is exploiting misconfigurations and vulnerabilities in Apache Hadoop and Apache Druid (CVE-2021-25646)

CVE-2024-25124 (CVSS 9.4) stems from allowing wildcard origins (*) in CORS configurations while simultaneously enabling credentials

Carpet-Bombing DDoS attacks inundate entire CIDR blocks, cloaking their malicious intent in a veil of complexity and making detection

Rhino Security Labs uncovered this flaw (CVE-2024-1212, CVSS 10) – an unauthenticated RCE allowing attackers to complete a system takeover

OpenVPN has released version 2.6.9 for Windows, Mac, and Linux, addressing a severe privilege escalation vulnerability (CVE-2023-7235)

Masquerading an internal sale of a BMW vehicle, APT29 distributed over 200 emails, embedding the RAR file that served as the Trojan horse

CVE-2024-1709 (CVSS Score 10): An authentication bypass that offers attackers unhindered backdoor entry to critical systems

Domains associated with Operation Texonto were found linked to potential influence operations aimed at Russian citizens

The Spring Framework, a cornerstone of countless enterprise Java applications, recently revealed a significant vulnerability (CVE-2024-22243)

Atlassian has released a security update addressing CVE-2024-21678 (CVSS 8.5), a high-severity stored cross-site scripting vulnerability