
 Do Son
The U.S. Secret Service announced it has dismantled a sprawling telecommunications threat network across the New York...
Latest news

At the Snapdragon Summit 2025 in Hawaii, Qualcomm President and CEO Cristiano Amon declared that AI will...

Not every user’s PC comes equipped with a dedicated graphics card, which is why many still rely...

Cybersecurity researcher Jeremiah Fowler has discovered a massive unprotected database containing highly sensitive insurance and vehicle-related records....

CISA this week added CVE-2025-10585, a high-severity type-confusion flaw in Google’s V8 JavaScript engine, to its Known...

The Open Source Security Foundation (OpenSSF), together with several prominent open-source and software foundations, has issued a...
Salesforce has published a security advisory detailing a high-severity flaw in its Salesforce-CLI installer (sf-x64.exe). The vulnerability,...

Researchers at Rapid7 have disclosed a critical permission bypass vulnerability in OnePlus OxygenOS, tracked as CVE-2025-10184. The...

The issue of AI systems harvesting website and publisher content without compensation for training models or generating...

Apple has officially confirmed that iOS 26’s Digital ID feature will support the addition of passports, allowing...

CVE-2023-43261 could allow attackers to expose sensitive information and gain unauthorized access to devices

Google and Microsoft confirmed that two zero-day vulnerabilities, CVE-2023-4863 and CVE-2023-5217 have been maliciously exploited in the wild

The vulnerability, tracked as CVE-2023-5288 (CVSS score of 9.8), could allow remote attackers to reconfigure or disrupt the devices.

Google’s bulletin sheds light on two bugs, specifically CVE-2023-4863 and CVE-2023-4211, believed to be under limited targeted exploitation
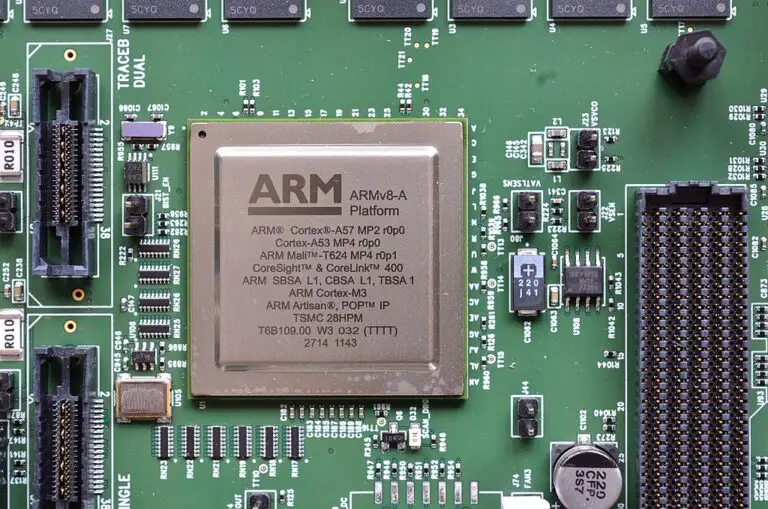
Arm's fix for CVE-2023-4211 has been incorporated into Android and Pixel devices. Google reacted, releasing the patch for its Pixel devices

The CVE-2023-43654 vulnerability in question is a server-side request forgery (SSRF) in PyTorch TorchServe.

Cyber security attacks are at an all-time high. Businesses are often targets or fall victim to attacks. Click here for the risks to keep an eye on.

Currently, Encrypted Client Hello has been embraced by major browsers: Google Chrome and Mozilla Firefox. For Safari: Support is forthcoming.

Menorah malware was spotted playing a crucial role in a recent targeted phishing attack demonstrating the group's undiminished proclivity

the ransomware group RansomedVC has ostentatiously claimed to have successfully infiltrated Sony's systems

The Cl0p ransomware group exploited a popular SQL injection vulnerability (CVE-2023-34362) within the MOVEit file transfer solution

This newfound vulnerability (CVE-2023-41081), graded as "important" in severity, is of particular concern.

The digital realm experienced a wave of unease as Mozilla revealed a critical zero-day vulnerability in its flagship Firefox web browser

Tracked as CVE-2018-14667, this vulnerability has received an alarming severity score of 9.8/10 from Red Hat
The diversity of dietary supplements is increasing every day, but omega-3 continues to remain one of the...

With a towering CVSS score of 9.8, the CVE-2023-42115 vulnerability unveils a gateway for remote attackers to embed arbitrary codes

CVE-2023-42121 allows remote attackers unbridled access to execute arbitrary code on affected installations of the Control Web Panel

A PoC code for a macOS CVE-2023-32364 vulnerability could be exploited to escape a sandbox and execute code within the Terminal

CVE-2023-20109 could allow an authenticated, remote attacker to execute arbitrary code on an affected device or cause the device to crash

The CVE-2023-20252 vulnerability resides in the Security Assertion Markup Language (SAML) APIs of Cisco Catalyst SD-WAN Manager

Google recently revealed in a security advisory that a zero-day vulnerability, designated as CVE-2023-5217, is being actively exploited.

CVE-2023-40044 (CVSS: 10) is a pre-authenticated remote command execution vulnerability that affects versions prior to 8.7.4 and 8.8.2