
 Do Son
A new study from a ZeroSalarium security researcher sheds light on a new technique to bypass endpoint...
Latest news

The LastPass Threat Intelligence, Mitigation, and Escalation (TIME) team has issued a warning about an ongoing infostealer...
As generative AI continues to evolve toward lighter and more localized deployments, Meta has announced the open-sourcing...

Although Apple’s new iPhone 17 series and iPhone Air have only just launched this year, market attention...

Security researcher Ezzer17 published a clear, methodical write-up that walks through the root cause, the partial fixes,...

Researchers at Silent Push have identified a newly emerging malware loader dubbed CountLoader, which they assess to...
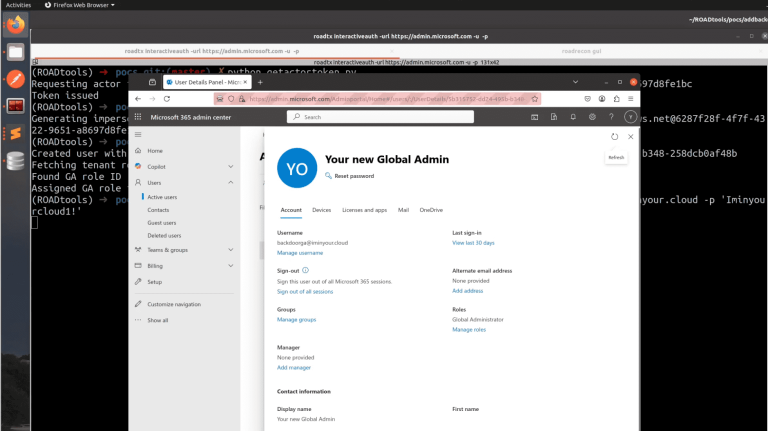
CVE-2025-55241: Microsoft Entra ID Flaw with CVSS 10.0 Could Have Compromised Every Tenant Worldwide
CVE-2025-55241: Microsoft Entra ID Flaw with CVSS 10.0 Could Have Compromised Every Tenant Worldwide
In one of the most significant discoveries of 2025, security researcher Dirk-jan Mollema revealed a vulnerability in...
The Varonis Threat Labs team has published an eye-opening report about a persistent vulnerability in how modern...

A new report from Insikt Group reveals that CopyCop, also known as Storm-1516, is rapidly expanding its...

The AhnLab Security Intelligence Center (ASEC) has released a detailed analysis of BlackLock, a relatively new ransomware...
CVE-2023-35674 could significantly elevate local privileges, all without the need for any user interaction or additional execution privileges
Are you always having trouble keeping track of where and how your company is spending its money?...

In today’s rapidly evolving business landscape, leveraging the full potential of the software at your company’s disposal...

A vulnerability (CVE-2023-28072) with a CVSS score of 7.8 was identified in versions of Dell Alienware Command Center prior to 5.5.51.0

A cybersecurity researcher has released the details, and a proof-of-concept (PoC) exploit for a high-severity vulnerability (CVE-2023-28229)

Anonymous Sudan, previously known for launching multiple DDoS attacks against Microsoft, recently targeted 'X' (formerly Twitter)

A cybersecurity researcher has released the details, and a PoC exploit for a critical severity vulnerability (CVE-2023-34039)

CVE‑2023‑25528 (CVSS: 8.8) - A web server plugin flaw could cause a stack overflow, potentially leading to arbitrary code execution

The landscape of technology in law enforcement has undergone transformations in police organizations worldwide. These changes have...

Synacktiv has released a proof-of-concept (PoC) exploit for a high-severity vulnerability (CVE-2023-35001) that exists in the Linux kernel

CVE-2023-4696 (CVSS score of 9.8) allows a nefarious actor to modify another user’s data, including passwords

At its core, CVE-2023-38036 allows malevolent actors to send a deviously crafted message to the Wavelink Avalanche Manager

As technological advancements are reshaping industries and customer interactions, one aspect remains constant: the threat of fraud....

CVE-2023-40595 vulnerability allows an attacker to execute a specially crafted query that can then be used to serialize untrusted data

CVE-2023-40596 allows an attacker to escalate their privileges on a Windows machine by abusing an insecure path reference in a DLL file
The CVE-2023-20900 vulnerability allows a malevolent actor, positioned in a man-in-the-middle (MITM) network setup between the vCenter server

Starting a business is an exhilarating yet demanding endeavor. As an entrepreneur, there are several essential questions...

In July 2023, JPCERT identified and christened this technique "MalDoc in PDF", which ingeniously sidesteps detection

CVE-2023-41265 allows attackers to elevate privileges by tunneling HTTP requests, granting them access to send HTTP requests

Revealed in May this year, this flaw is exploited to release the Kinsing malware and a cryptominer, posing significant risks for users

ClamAV versions 1.1.x prior to 1.1.2, 1.0.x prior to 1.0.3, and 0.103.x earlier than 0.103.10 are affected by this vulnerability

Emerging in the 1990s, Virtual Private Networks (VPNs) were conceptualized to establish transient, secure connections over public...