Skip to content
November 1, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Adobe Campaign Classic CVE-2026-48331 Scores CVSS 10.0 for Arbitrary Code Execution Adobe Campaign Classic arbitrary code execution vulnerability CVE-2026-48331 CVSS 10.0 security update
  • Vulnerability Report

Adobe Campaign Classic CVE-2026-48331 Scores CVSS 10.0 for Arbitrary Code Execution

Do Son August 4, 2026 0

Adobe patched critical Adobe Campaign Classic flaws. CVE-2026-48331 scores CVSS 10.0 and enables arbitrary code execution. Update to build 9399 now.
Multiple Apache NiFi Vulnerabilities Fixed in Version 2.11.0 Diagram showing Apache NiFi vulnerabilities and patch details
  • Vulnerability Report

Multiple Apache NiFi Vulnerabilities Fixed in Version 2.11.0

Do Son August 4, 2026 0

Apache NiFi vulnerabilities, including CVE-2026-68979, CVE-2026-62354, and CVE-2026-68981, expose users to code execution and resource consumption.
CVE-2026-58048: cPanel Root SQL Execution Flaw Patched cPanel root SQL execution vulnerability CVE-2026-58048 database privilege escalation diagram
  • Vulnerability Report

CVE-2026-58048: cPanel Root SQL Execution Flaw Patched

Do Son August 4, 2026 0

CVE-2026-58048 lets cPanel users run SQL commands in root context, CVSS 9.4. A second flaw, CVE-2026-58047, enables request smuggling.
CVE-2026-18577: N-central Account Takeover Exploited in the Wild N-central account takeover vulnerability CVE-2026-18577 exploited via authentication bypass
  • Vulnerability Report

CVE-2026-18577: N-central Account Takeover Exploited in the Wild

Do Son August 3, 2026 0

CVE-2026-18577 is being exploited in the wild for N-central account takeover. An incomplete patch let attackers gain admin access. Update to 2026.3.1.7.
CVE-2026-18574: Check Point Authentication Bypass Hits Management Server Check Point authentication bypass vulnerability CVE-2026-18574 on Security Management Server
  • Vulnerability Report

CVE-2026-18574: Check Point Authentication Bypass Hits Management Server

Do Son August 3, 2026 0

CVE-2026-18574 is a Check Point authentication bypass rated CVSS 9.3, letting attackers run commands as admin. Patch via the latest Jumbo Hotfix.
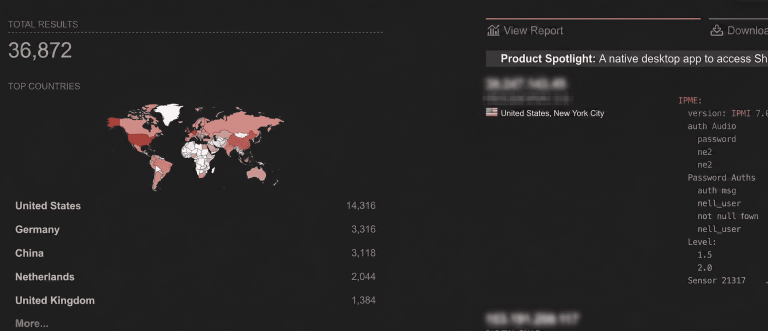
36,872 Exposed BMCs Leak Password Hashes and Face In-the-Wild Attacks via CVE-2013-4786 Map of 36,872 exposed BMCs leaking IPMI hashes via CVE-2013-4786 across data centers
  • Vulnerability Report

36,872 Exposed BMCs Leak Password Hashes and Face In-the-Wild Attacks via CVE-2013-4786

Do Son August 3, 2026 0

LAVA found 36,872 exposed BMCs leaking IPMI password hashes via CVE-2013-4786. Some are already exploited in the wild. Here is how to lock them down.
SICK InspectorP6xx Flaw CVE-2026-11841 Could Lead to Full Device Compromise SICK InspectorP6xx vulnerability CVE-2026-11841 exposing internal files via SOPAS FileSystemAccess
  • Vulnerability Report

SICK InspectorP6xx Flaw CVE-2026-11841 Could Lead to Full Device Compromise

Do Son August 3, 2026 0

CVE-2026-11841 lets an unauthenticated attacker reach internal files on SICK InspectorP6xx devices, risking device compromise. CVSS 9.4. Update to 5.4.0.
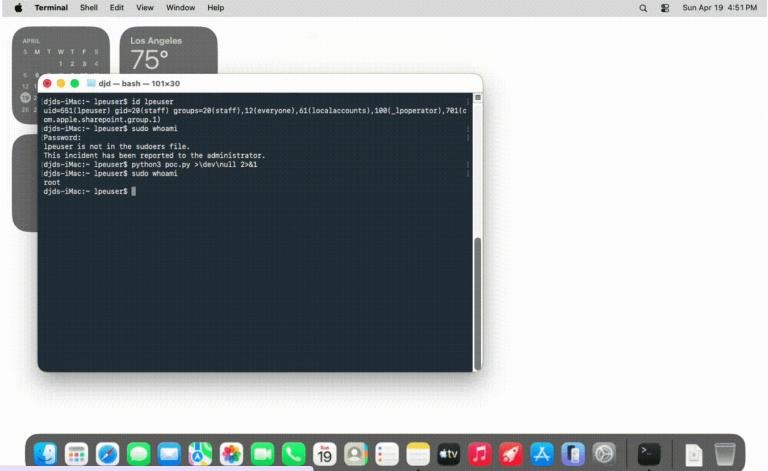
CVE-2026-39875: Public PoC Lets a Malicious macOS App Gain Root Privileges macOS privilege escalation via CVE-2026-39875 CUPS flaw with public proof-of-concept exploit gaining root
  • Vulnerability Report

CVE-2026-39875: Public PoC Lets a Malicious macOS App Gain Root Privileges

Do Son August 3, 2026 0

Details and PoC exploit code for CVE-2026-39875 are now public. This macOS privilege escalation flaw lets a malicious app gain root. Patch now.
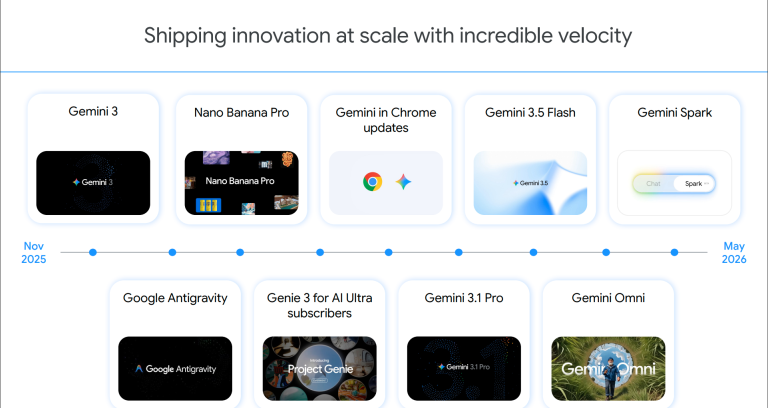
Alphabet Q2 2026 Revenue Hits $119.8B as Pichai Confirms Gemini 4 Alphabet Q2 2026 earnings showing 82 percent Google Cloud growth and CEO Sundar Pichai confirming pretraining has begun on the Gemini 4 model
  • Technology

Alphabet Q2 2026 Revenue Hits $119.8B as Pichai Confirms Gemini 4

Do Son August 3, 2026 0

Alphabet posted $119.8 billion in Q2 2026 revenue on 82% cloud growth, and CEO Sundar Pichai confirmed pretraining has begun on Gemini 4.
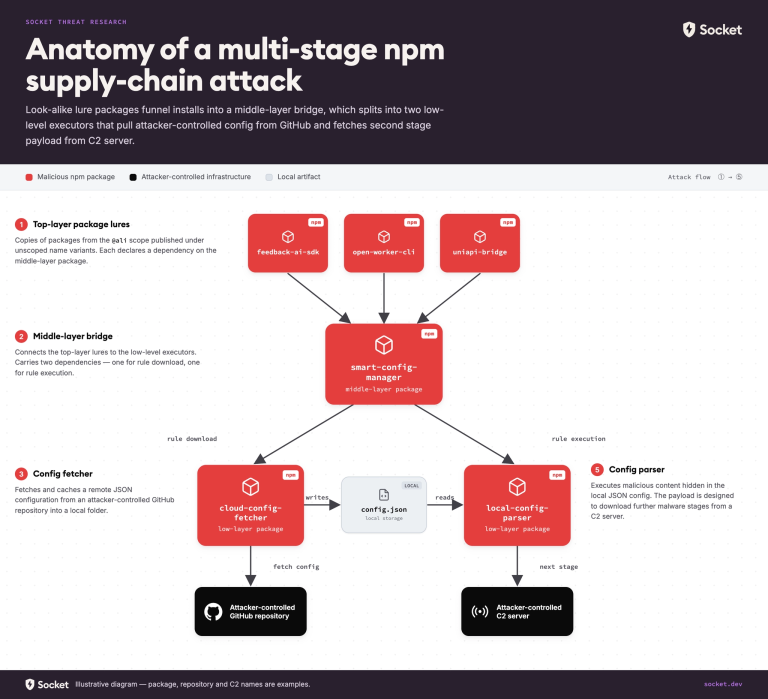
npm Supply Chain Attack Delivers a Cross-Platform RAT to Alibaba Developers npm supply chain attack delivering a cross-platform RAT via malicious npm packages targeting Alibaba developers
  • Malware

npm Supply Chain Attack Delivers a Cross-Platform RAT to Alibaba Developers

Do Son August 3, 2026 0

A distributed npm supply chain attack dropped a cross-platform RAT on Alibaba developers. Socket found malicious npm packages hiding loader code.
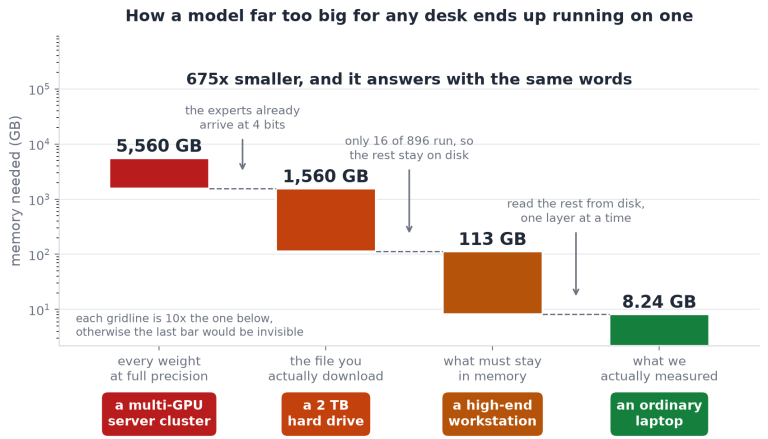
Running Kimi K3 in C: Local AI Inference on 8GB RAM Kimi K3 in C inference engine running locally on CPU
  • Technology

Running Kimi K3 in C: Local AI Inference on 8GB RAM

Do Son August 3, 2026 0

Developer FareedKhan built a C99 engine to run the massive Kimi K3 model on a single CPU with 8GB RAM using NVMe streaming.
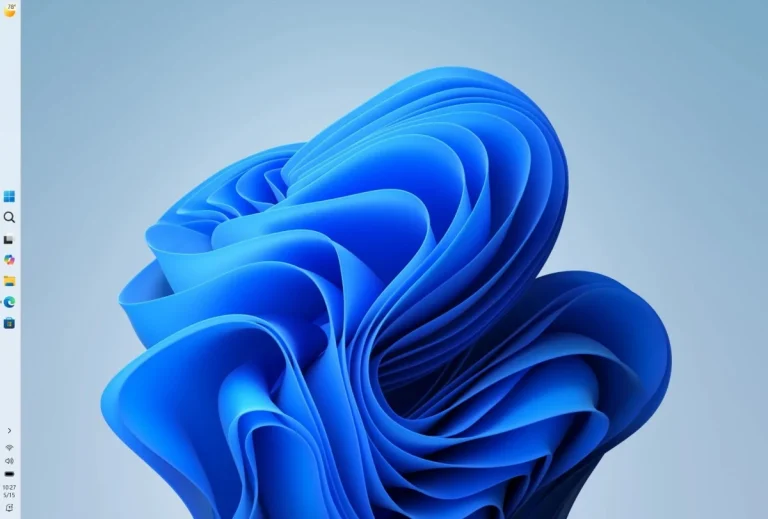
Windows 11 Custom Taskbar: Move It Anywhere Again Windows 11 custom taskbar settings showing top and side placement options
  • Windows

Windows 11 Custom Taskbar: Move It Anywhere Again

Do Son August 3, 2026 0

Discover the returning Windows 11 custom taskbar feature. Microsoft finally allows users to move their taskbars to any screen edge in the latest Beta build.
Tengu Botnet Is a Modernized Mirai Variant That Fights to Stay on IoT Devices C2Looper Rust backdoor diagram showing GitHub command-and-control and ClickFix ransomware infection chain
  • Malware

Tengu Botnet Is a Modernized Mirai Variant That Fights to Stay on IoT Devices

Do Son August 3, 2026 0

Nozomi details the Tengu botnet, a modernized Mirai variant. This IoT malware adds encrypted C2, proxy, anti-analysis, and self-defense to resist removal.
CastleLoader Malware Now Delivers NeedleStealer Wallet and Browser Spoofers CastleLoader malware infection chain delivering NeedleStealer crypto wallet spoofer and NetSupport RAT
  • Malware

CastleLoader Malware Now Delivers NeedleStealer Wallet and Browser Spoofers

Do Son August 3, 2026 0

CastleLoader malware now delivers NeedleStealer, a Rust crypto wallet spoofer and Golang browser hijacker. Arctic Wolf tracks three new campaigns.
Debian 13 Kernel Update Fixes 68 Flaws, Four Rated Critical Debian 13 Linux kernel security update DSA-6405-1 fixing 68 vulnerabilities including four critical use-after-free flaws in net/sched, NVMe/TCP, and SMC-R
  • Linux

Debian 13 Kernel Update Fixes 68 Flaws, Four Rated Critical

Do Son August 3, 2026 0

Debian 13 pushes a kernel update fixing 68 vulnerabilities including four critical use-after-free flaws. Upgrade to kernel 6.12.100-1 and reboot now.
Devastating ColdCard Wallet Hack Costs Investors Millions ColdCard wallet hack visualization showing compromised Bitcoin hardware security
  • Vulnerability Report

Devastating ColdCard Wallet Hack Costs Investors Millions

Do Son August 3, 2026 0

A devastating ColdCard wallet hack has cost investors nearly $100 million. A critical firmware flaw allowed hackers to drain Bitcoin funds effortlessly.
OpenAI Astra Math Breakthrough: A New Era of Scientific Discovery OpenAI Astra math breakthrough concept visualization
  • Technology

OpenAI Astra Math Breakthrough: A New Era of Scientific Discovery

Do Son August 3, 2026 0

Discover the OpenAI Astra math breakthrough. This next-gen AI model solved ten complex, decades-old mathematical problems, reshaping scientific research.
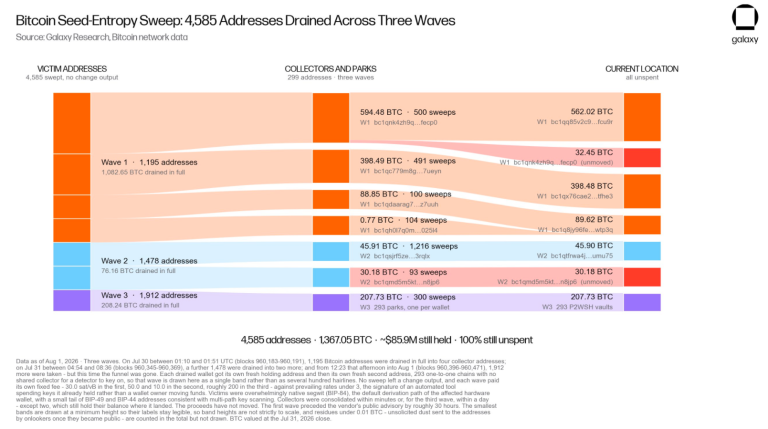
COLDCARD Exploit Grows to 1,367 BTC Stolen Across Three Waves COLDCARD hardware wallet exploit growing to 1,367 BTC stolen across three attack waves from 4,585 wallets, tracked by Galaxy Research on-chain analysis
  • Cybercriminals

COLDCARD Exploit Grows to 1,367 BTC Stolen Across Three Waves

Do Son August 3, 2026 0

The COLDCARD seed flaw theft has climbed to 1,367 BTC across three attack waves and 4,585 wallets, with the third wave using harder-to-trace P2WSH addresses.
.web TLD Finally Reaches the DNS Root After a Decade of Disputes .web TLD delegated to the DNS root by ICANN after a decade of legal disputes, with Verisign planning to open domain registration in late 2026
  • Technology

.web TLD Finally Reaches the DNS Root After a Decade of Disputes

Do Son August 3, 2026 0

ICANN has delegated the .web TLD to the DNS root, ending a decade of legal battles. Verisign plans to open registration in the second half of 2026.
Google Developing Dynamic Patching to Update Chrome Without a Restart Google Chrome dynamic patching technology replacing background sub-processes with updated versions to apply security fixes without a full browser restart
  • Technology

Google Developing Dynamic Patching to Update Chrome Without a Restart

Do Son August 3, 2026 0

Google is building dynamic patching for Chrome, replacing background sub-processes with updated versions so security fixes land without a full restart.
SonicWall SMA Exploit Chain Now Fuels INC Ransomware Attacks SonicWall SMA exploit chain diagram showing wsproxy bypass leading to INC Ransomware root access
  • Malware

SonicWall SMA Exploit Chain Now Fuels INC Ransomware Attacks

Do Son August 3, 2026 0

A SonicWall SMA exploit chain (CVE-2026-15409, CVE-2026-15410) grants root access and now feeds INC Ransomware attacks. Patch to 12.5.0-02835+.
Fedora 46 to Enable Shadow Stack by Default on x86-64 Systems Fedora 46 enabling Intel CET shadow stack protection by default on x86-64 systems to block ROP attacks, delayed from Fedora 45 for driver compatibility
  • Linux

Fedora 46 to Enable Shadow Stack by Default on x86-64 Systems

Do Son August 3, 2026 0

Fedora 46 will enable Intel CET shadow stack protection by default on x86-64 systems, blocking ROP attacks with minimal performance cost.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-112353CVSS 6.2
    GFI KerioConnect (Kerio Connect) before 10.0.8 Patch 2 contains a stored cross-site scripting vulnerability in the Webmail component...
    Watchtower Verified📅 Updated: Oct 29, 2026
  • CVE-2026-116779CVSS 9.8
    Summary `sofia_presence_handle_sip_i_message()` splits the To user of an inbound SIP MESSAGE on `+` and treats the left half...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-98432CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: ipv4: free inet_opt and ireq_opt after an RCU...
    📅 Updated: Oct 31, 2026
  • CVE-2026-118636CVSS 9.8
    **UNSUPPORTED WHEN ASSIGNED**  JavaNativeMessageDecoder in the MINA 3.0 codec module calls ObjectInputStream.readObject() on frame bytes with no class...
    📅 Updated: Oct 31, 2026
  • CVE-2026-120209CVSS 9.3
    AJ-Report through 1.7.1 signs share tokens with a hard-coded JWT secret, allowing attackers to forge valid Share-Tokens offline....
    📅 Updated: Oct 31, 2026
  • CVE-2026-120201CVSS 9.3
    Jpom 2.10.0 through 2.11.12 contains an authentication bypass vulnerability that allows unauthenticated attackers to gain super-administrator access by...
    📅 Updated: Oct 31, 2026
  • CVE-2026-69399CVSS 9.9
    Unintended proxy or intermediary in Azure Arc allows an authorized attacker to elevate privileges over a network.
    📅 Updated: Oct 31, 2026
  • CVE-2026-113380CVSS 9.3
    In the RingRTC library before 2.72.0 for Signal, a peer that saturates a call's FSM queue can interfere...
    📅 Updated: Oct 31, 2026
  • CVE-2026-99153CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: scsi: libiscsi: Validate the ITT reflected in a...
    📅 Updated: Oct 31, 2026
  • CVE-2026-99154CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: scsi: libiscsi: Reject a negative task index from...
    📅 Updated: Oct 31, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.