Skip to content
November 2, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Cursor Builds General AI Agent to Rival Claude Cowork Cursor AI general purpose agent competing with Claude Cowork for desktop computer control
  • Technology

Cursor Builds General AI Agent to Rival Claude Cowork

Do Son July 13, 2026 0

Cursor is reportedly building a general-purpose AI agent to challenge Claude Cowork, expanding from coding into full computer control.

Weekly CVE Report: 1,571 New Flaws and 6 Actively Exploited Bugs (July 6–12, 2026) weekly CVE report actively exploited vulnerabilities
  • Weekly Recap

Weekly CVE Report: 1,571 New Flaws and 6 Actively Exploited Bugs (July 6–12, 2026)

Do Son July 13, 2026 0

Our weekly CVE report: 1,571 new flaws and 6 actively exploited vulnerabilities hit CISA KEV, including ColdFusion and Joomla RCE.

Mycelium Framework: First AI-as-a-Service Botnet TanStack Typosquatting npm Supply Chain Attack Axios Supply Chain Attack npm Poisoning eScan Supply Chain Attack Antivirus Compromise APT-36, NCERT WhatsApp Advisory FBI alert, Salesforce Salt Typhoon, APT group ConnectWise ScreenConnect hack Nation-state cyberattack FortiGate Leak - zkLend vulnerability - TRIPLESTRENGTH Threat Actor Group Dark Storm
  • Malware

Mycelium Framework: First AI-as-a-Service Botnet

Do Son July 13, 2026 0

Discover how the Mycelium Framework transforms infected machines into a malicious AI-as-a-Service botnet for distributed computing and automated exploits.
CVE-2026-49844: Apache Log4j Emits Invalid JSON Logs Apache Log4j CVE-2026-49844 flaw producing invalid JSON in log4j-api output
  • Vulnerability Report

CVE-2026-49844: Apache Log4j Emits Invalid JSON Logs

Do Son July 13, 2026 0

A new Apache Log4j flaw, CVE-2026-49844, makes log4j-api emit invalid JSON from non-finite numbers. Patch to 2.25.5 or 2.26.1 now.
decompress npm Vulnerability CVE-2026-53486 (CVSS 9.1) Threatens 2.8 Million Weekly Downloads decompress npm vulnerability CVE-2026-53486 path traversal in Node.js archive extraction
  • Vulnerability Report

decompress npm Vulnerability CVE-2026-53486 (CVSS 9.1) Threatens 2.8 Million Weekly Downloads

Do Son July 12, 2026 0

A decompress npm vulnerability (CVE-2026-53486, CVSS 9.1) lets crafted archives write files outside the target folder via path traversal. Patch now.
State of Exploited Vulnerabilities — Q2 2026 75 CVEs confirmed exploited in Q2 2026. Microsoft leads with 15, Ivanti tops EPSS at 99%. Full breakdown by vendor, CWE, and publication-to-exploit gap.
  • Report

State of Exploited Vulnerabilities — Q2 2026

Do Son July 11, 2026 0

75 CVEs confirmed exploited in Q2 2026. Microsoft leads with 15, Ivanti tops EPSS at 99%. Full breakdown by vendor, CWE, and publication-to-exploit gap.

Apache IoTDB Fixes Path Traversal and Authentication Bypass Flaws (CVE-2026-24014) Apache IoTDB vulnerabilities path traversal and authentication bypass in DataNode RPC
  • Vulnerability Report

Apache IoTDB Fixes Path Traversal and Authentication Bypass Flaws (CVE-2026-24014)

Do Son July 11, 2026 0

Three Apache IoTDB vulnerabilities include a critical path traversal (CVE-2026-24014) and an authentication bypass. Upgrade to 2.0.8 now.

Silver Fox Ghost Distributor Delivers MODBEACON Trojan to Chosen Targets Harvester APT Linux Backdoor OT Cyberattack Iranian APT Operation Olalampo MuddyWater APT Prince of Persia APT, Tonnerre v50 Patchwork APT, DLL Sideloading Subtle Snail, cyber espionage ShadowSilk, cyber espionage Volt Typhoon APT Group - Chinese Cybersecurity Firm
  • Cyber Security

Silver Fox Ghost Distributor Delivers MODBEACON Trojan to Chosen Targets

Do Son July 11, 2026 0

Silver Fox's Ghost distributor delivers MODBEACON, a modular Rust trojan, to picked targets in Operation Phnom Penh, per Qianxin. Here's what to know.
Apache Camel Vulnerabilities Expose Routes to Header Injection and SSRF Apache Camel vulnerabilities diagram showing header injection and server-side request forgery attack flow across Camel routes
  • Vulnerability Report

Apache Camel Vulnerabilities Expose Routes to Header Injection and SSRF

Do Son July 10, 2026 0

Four Apache Camel vulnerabilities allow header injection, server-side request forgery, secret disclosure, and an authentication bypass. Patch to 4.21.0 now.
Gardyn IoT Hub Flaw CVE-2026-13768 (CVSS 10) Enables Unauthenticated Remote Code Execution Gardyn IoT Hub advisory graphic showing CVE-2026-13768 remote code execution risk on smart garden devices
  • Vulnerability Report

Gardyn IoT Hub Flaw CVE-2026-13768 (CVSS 10) Enables Unauthenticated Remote Code Execution

Do Son July 10, 2026 0

CISA warns of a Gardyn IoT Hub flaw. CVE-2026-13768 (CVSS 10) enables unauthenticated remote code execution on smart garden devices. Update now.
FreeBSD Patches Three Kernel Flaws That Enable Local Privilege Escalation FreeBSD privilege escalation advisory chart highlighting a kernel use-after-free and two local root flaws
  • Vulnerability Report

FreeBSD Patches Three Kernel Flaws That Enable Local Privilege Escalation

Do Son July 10, 2026 0

Three FreeBSD privilege escalation flaws, including a kernel use-after-free, let local users gain root. Patch FreeBSD 14 and 15 now.
Kafka Authentication Bypass in the OAUTHBEARER JWT Path Kafka authentication bypass through OAUTHBEARER JWT replay on Apache Kafka 4.0.x brokers
  • Vulnerability Report

Kafka Authentication Bypass in the OAUTHBEARER JWT Path

Do Son July 10, 2026 0

A Kafka authentication bypass lets attackers replay expired JWTs against 4.0.x brokers. The OAUTHBEARER path checks nbf but not exp. No fix yet.
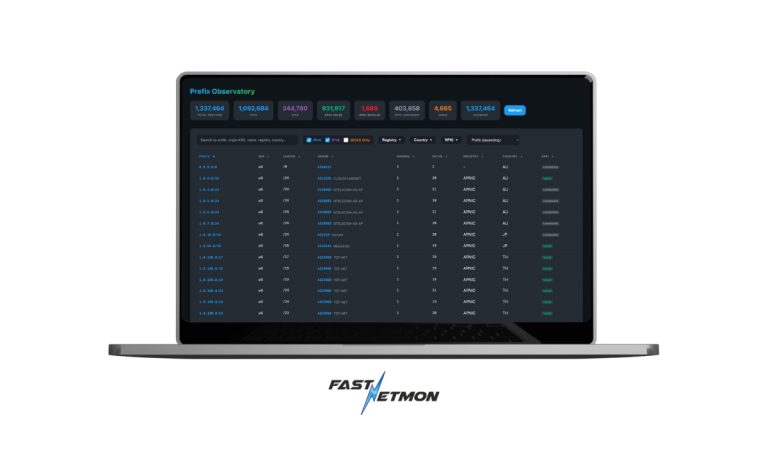
FastNetMon Launches Netomics, a Self-Hosted Routing Intelligence Platform Netomics_Self-hosted_Routing_Intelligence_for_Netw_1783602857g1YFYzWQZz
  • Press Release

FastNetMon Launches Netomics, a Self-Hosted Routing Intelligence Platform

cybernewswire July 10, 2026 0
London, United Kingdom, 10th July 2026, CyberNewswire
Read More Read more about FastNetMon Launches Netomics, a Self-Hosted Routing Intelligence Platform
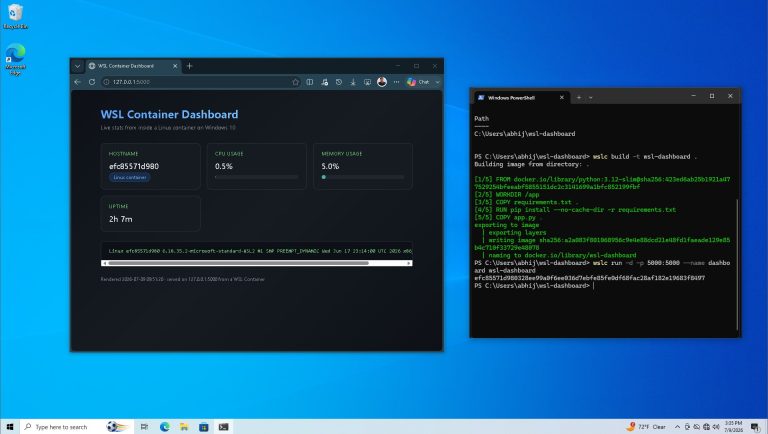
WSL Containers Now Runs on Windows 10 Too WSL Containers running on Windows 10 without Docker Desktop using wslc command in Windows Terminal
  • Windows

WSL Containers Now Runs on Windows 10 Too

Do Son July 10, 2026 0

Microsoft confirms WSL Containers works on Windows 10 (Build 19041+) without Docker Desktop. Here's how to deploy it in six steps.
CVE-2026-13753: HP Missing Authorization Vulnerability HP Deskjet missing authorization vulnerability CVE-2026-13753 exposing printer API security flaw
  • Vulnerability Report

CVE-2026-13753: HP Missing Authorization Vulnerability

Do Son July 10, 2026 0

CVE-2026-13753 exposes a missing authorization vulnerability in HP Deskjet 2800 printers. Unauthenticated attackers can extract sensitive Wi-Fi credentials.
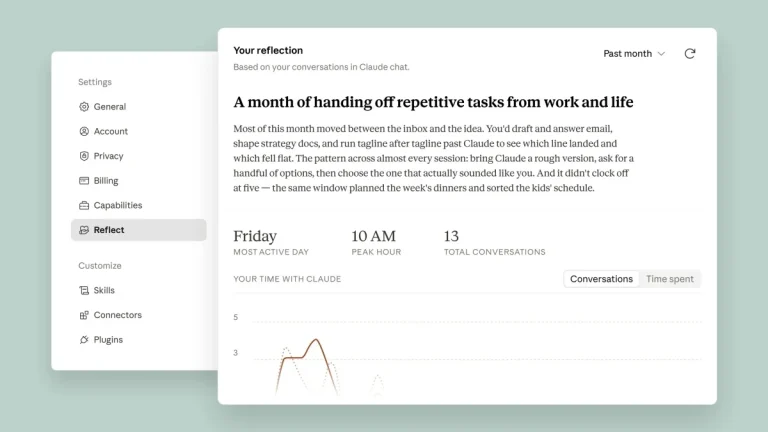
Claude Reflect Dashboard: Anthropic’s New AI Tool Claude Reflect dashboard interface visualizing AI usage statistics and productivity metrics.
  • Technology

Claude Reflect Dashboard: Anthropic’s New AI Tool

Do Son July 10, 2026 0

Discover the Claude Reflect dashboard. Anthropic's new digital health tool visualizes your AI usage, optimizes prompts, and promotes healthy collaboration.
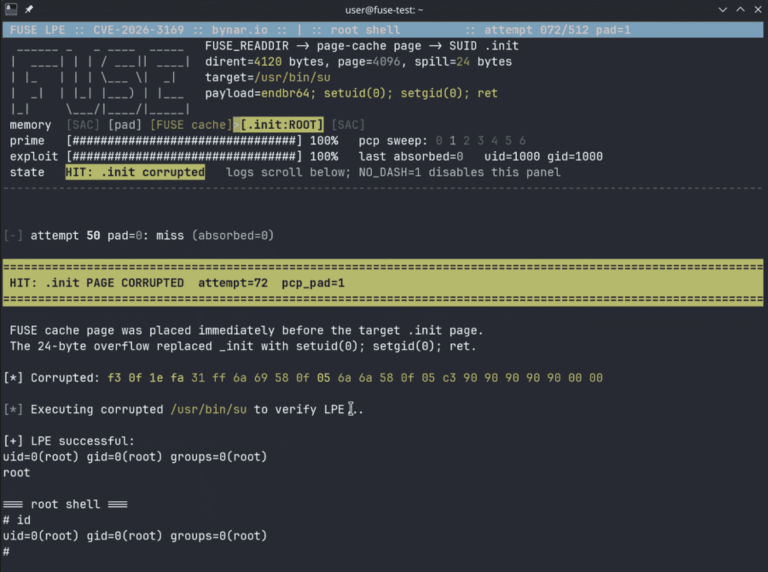
Public PoC Discloses CVE-2026-31694, a Linux Kernel FUSE Local Privilege Escalation Linux kernel FUSE local privilege escalation via CVE-2026-31694 page cache overflow
  • Vulnerability Report

Public PoC Discloses CVE-2026-31694, a Linux Kernel FUSE Local Privilege Escalation

Do Son July 10, 2026 0

Public PoC and full details are out for CVE-2026-31694, a Linux kernel FUSE page cache overflow that gives local privilege escalation to root. Patch now.
PamStealer macOS Malware Poses as Maccy to Steal Passwords PamStealer macOS malware delivering a Rust infostealer through a fake Maccy clipboard app
  • Malware

PamStealer macOS Malware Poses as Maccy to Steal Passwords

Do Son July 10, 2026 0

PamStealer macOS malware hides in a fake Maccy app and drops a Rust infostealer that checks your password via PAM before stealing it.
GNU Guix Vulnerabilities Expose guix substitute and guix pull GNU Guix vulnerabilities in guix substitute and guix pull enabling remote privilege escalation
  • Vulnerability Report

GNU Guix Vulnerabilities Expose guix substitute and guix pull

Do Son July 10, 2026 0

Four GNU Guix vulnerabilities in guix substitute and guix pull allow remote privilege escalation, file overwrite, and local file disclosure. Update now.
JADEPUFFER Marks the First AI-Driven Agentic Ransomware Attack JADEPUFFER agentic ransomware attack chain diagram from Langflow RCE to database extortion
  • Malware

JADEPUFFER Marks the First AI-Driven Agentic Ransomware Attack

Do Son July 10, 2026 0

Sysdig documented JADEPUFFER, the first agentic ransomware run end-to-end by an AI agent. It breached Langflow via CVE-2025-3248 and extorted a database.
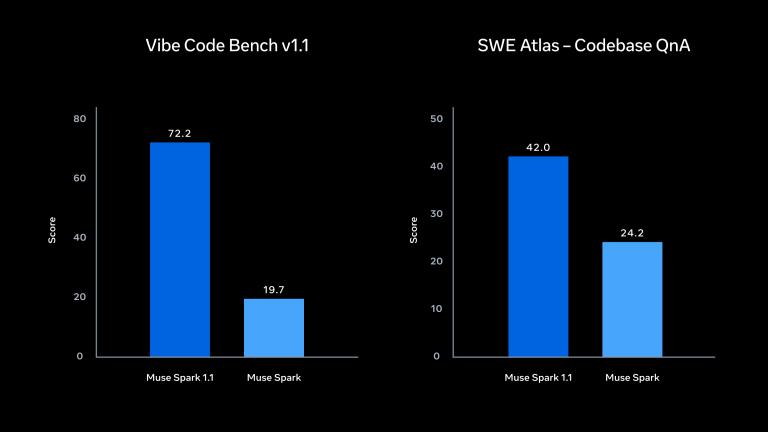
Meta Introduces Muse Spark 1.1 AI Model Meta Muse Spark 1.1 artificial intelligence model for agent tasks and programming.
  • Technology

Meta Introduces Muse Spark 1.1 AI Model

Do Son July 10, 2026 0

Meta introduces Muse Spark 1.1, a closed-source AI model built for complex agent tasks and programming. Discover its advanced capabilities and pricing.
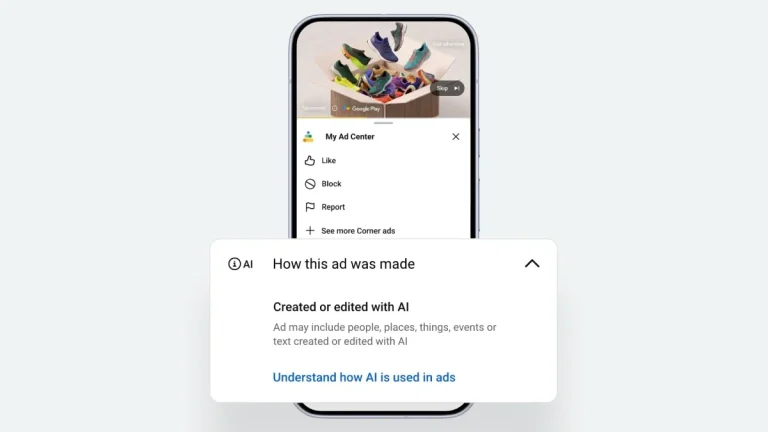
Google Ads AI Transparency Tools to Combat Fake Content Google Ads AI transparency tools displayed within the My Ad Center interface.
  • Technology

Google Ads AI Transparency Tools to Combat Fake Content

Do Son July 10, 2026 0

Google Ads AI transparency tools will soon label artificial content in My Ad Center. Discover how this update aims to protect consumer trust globally.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-58115CVSS 10.0
    A vulnerability has been identified in SIMATIC IoT2050 Advanced (6ES7647-0BA00-1YA2) (All versions < V4.3.4.1 running Industrial OS with...
    Admin intel📅 Updated: Nov 2, 2026
  • CVE-2026-77876CVSS 9.3
    Control Web Panel (CWP) before webpanel_version 1.16 contains an OS command injection vulnerability in the protected_directory user panel...
    📅 Updated: Nov 2, 2026
  • CVE-2026-79873CVSS 9.3
    Authentication bypass vulnerabilities in the PAPI protocol of AOS-10 could allow an unauthenticated adjacent attacker to circumvent existing...
    📅 Updated: Nov 2, 2026
  • CVE-2026-79874CVSS 9.3
    An authentication bypass in the API of AOS-10 allows an unauthenticated adjacent attacker to circumvent existing authentication controls....
    📅 Updated: Nov 2, 2026
  • CVE-2026-79872CVSS 9.4
    A buffer overflow vulnerability exists in the underlying operating system of AOS that could lead to unauthenticated remote...
    📅 Updated: Nov 2, 2026
  • CVE-2026-55981CVSS 9.6
    A firmware verification vulnerability in Creative Sound Blaster Katana could allow an attacker to modify a legitimate firmware...
    📅 Updated: Nov 2, 2026
  • CVE-2026-118235CVSS 9.8
    The SimpleForm – Form Maker to Chat Apps with Quiz, Poll and Multi Lead Notifications plugin for WordPress...
    📅 Updated: Nov 2, 2026
  • CVE-2026-116512CVSS 9.8
    The Project Manager – AI Powered Project Management, Task Management, Kanban Board & Time Tracker plugin for WordPress...
    📅 Updated: Nov 2, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.