Skip to content
November 2, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
Apple Removes Russian Apps VK and MAX from App Store Apple removes Russian apps VK and MAX from the App Store amid a Kremlin sanctions and push notification dispute
  • Technology

Apple Removes Russian Apps VK and MAX from App Store

Do Son June 29, 2026 0

Apple removes Russian apps VK and MAX from the App Store without explanation, prompting Kremlin demands and push notification cutoffs.

Cloud Gatekeeper Designation: AWS and Azure Face Strict DMA Regulation European Commission cloud gatekeeper designation review for AWS and Azure platforms
  • Technology

Cloud Gatekeeper Designation: AWS and Azure Face Strict DMA Regulation

Do Son June 29, 2026 0

The European Commission issues a preliminary cloud gatekeeper designation for AWS and Azure under the DMA, sparking fierce industry opposition.
Public PoC and Exploit Details Released for IPV6_FRAG_ESCAPE on RHEL 10 IPV6_FRAG_ESCAPE IPv6 container escape PoC root shell on RHEL 10 and CentOS Stream 10 kernel
  • Vulnerability Report

Public PoC and Exploit Details Released for IPV6_FRAG_ESCAPE on RHEL 10

Do Son June 29, 2026 0

Researcher Massimiliano Oldani disclosed IPV6_FRAG_ESCAPE, a public PoC for an unprivileged IPv6 container escape on RHEL 10 and CentOS. No CVE.
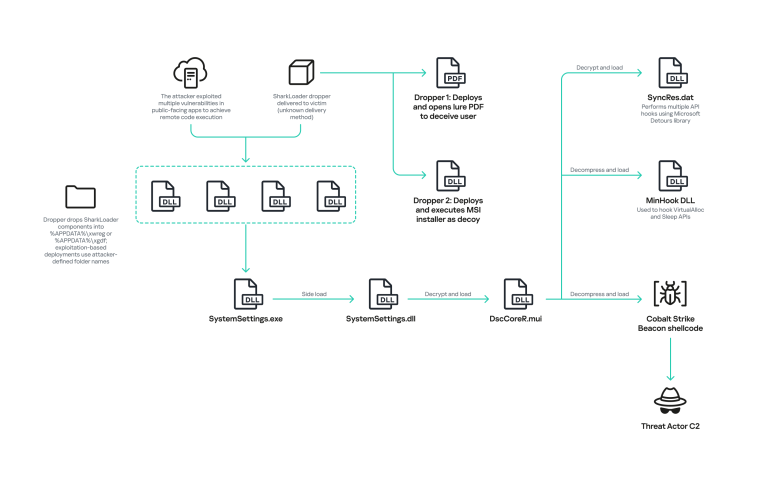
SharkLoader Malware Deploys Cobalt Strike in Global StrikeShark Campaign SharkLoader malware infection chain deploying Cobalt Strike Beacon in the StrikeShark campaign
  • Malware

SharkLoader Malware Deploys Cobalt Strike in Global StrikeShark Campaign

Do Son June 29, 2026 0

Kaspersky details SharkLoader malware, which deploys Cobalt Strike Beacon in the global StrikeShark campaign via DLL sideloading and exploited apps.
NTLM Reflection Bypass CVE-2026-24294 Gets Public PoC Exploit NTLM reflection CVE-2026-24294 SMB local privilege escalation Windows Server 2025 PoC exploit
  • Vulnerability

NTLM Reflection Bypass CVE-2026-24294 Gets Public PoC Exploit

Do Son June 29, 2026 0

Synacktiv publicly disclosed an NTLM reflection bypass, CVE-2026-24294, with PoC exploit code. It gives SYSTEM on Windows Server 2025. Patch now.
macOS Gaslight Malware Uses LLM Prompt Injection Diagram showing macOS Gaslight malware infection chain and Rust backdoor prompt injection
  • Malware

macOS Gaslight Malware Uses LLM Prompt Injection

Do Son June 29, 2026 0

The new macOS Gaslight malware, a North Korean Rust backdoor, targets analysts with LLM prompt injection and steals sensitive keychain data.

Thailand Healthcare Malware Exploits RAR Archives Diagram showing the Thailand healthcare malware infection chain via RAR archive phishing
  • Cybercriminals

Thailand Healthcare Malware Exploits RAR Archives

Do Son June 29, 2026 0

Threat actors are using RAR archive phishing to deploy Thailand healthcare malware. The campaign targets hospitals to steal credentials and sensitive data.

Edgecution Malware Turns a Microsoft Edge Extension Into a Backdoor C2Looper Rust backdoor diagram showing GitHub command-and-control and ClickFix ransomware infection chain
  • Malware

Edgecution Malware Turns a Microsoft Edge Extension Into a Backdoor

Do Son June 29, 2026 0

Edgecution malware abuses a malicious Edge extension and native messaging to backdoor hosts. Zscaler links it to a Payouts King access broker.
Google Gemini Compute Shortage: The Global AI Crisis Gemini AI branching threads Gemini 3.1 Flash-Lite Google Gemini compute shortage affecting Meta operations and AI token limits
  • Technology

Google Gemini Compute Shortage: The Global AI Crisis

Do Son June 29, 2026 0

Discover how the Google Gemini compute shortage forces Meta to accelerate internal AI models. Learn why Google now rents SpaceX GPUs to meet massive demand.

Google Wallet Package Tracking Turns Your Gmail Receipts Into Delivery Cards Google Wallet package tracking card showing Gmail delivery info on the home screen
  • Technology

Google Wallet Package Tracking Turns Your Gmail Receipts Into Delivery Cards

Do Son June 29, 2026 0

Google Wallet package tracking now reads Gmail receipts to show incoming deliveries on its home screen, rivaling Apple Wallet.

Cisco Unified CM RCE Flaw Exploited in the Wild as PoC Code Goes Public Cisco Unified CM RCE flaw CVE-2026-20230 exploited in the wild with public PoC exploit code
  • Vulnerability Report

Cisco Unified CM RCE Flaw Exploited in the Wild as PoC Code Goes Public

Do Son June 29, 2026 0

Attackers exploit a Cisco Unified CM RCE flaw (CVE-2026-20230) in the wild. Public PoC code now details the SSRF-to-root chain. Patch now.

Weekly CVE Report Logs 1,909 New Vulnerabilities and 6 Exploited Flaws Weekly CVE report June 2026 1909 new vulnerabilities CISA KEV CVE-2026-20230 exploited
  • Weekly Recap

Weekly CVE Report Logs 1,909 New Vulnerabilities and 6 Exploited Flaws

Do Son June 29, 2026 0

This weekly CVE report covers 1,909 new vulnerabilities from June 22-28, 2026. CISA flagged six as exploited, including CVE-2026-20230.
Dell Wyse Vulnerabilities Allow CVSS 9.8 Code Execution Diagram of Dell Wyse vulnerabilities showing remote code execution and CVE-2026-41120 exploit
  • Vulnerability Report

Dell Wyse Vulnerabilities Allow CVSS 9.8 Code Execution

Do Son June 29, 2026 0

Critical Dell Wyse vulnerabilities (CVE-2026-41120) allow unauthenticated remote code execution. Administrators must patch management suites immediately.
Gemini CLI Vulnerability Hits Maximum CVSS 10 Score Google Gemini CLI vulnerability execution flow and CVE-2026-12537 patch details
  • Vulnerability Report

Gemini CLI Vulnerability Hits Maximum CVSS 10 Score

Do Son June 29, 2026 0

A critical CVSS 10 Gemini CLI vulnerability (CVE-2026-12537) allows unprivileged attackers to execute code in GitHub Actions. Patch your workflows now.

CVSS 10 Hoppscotch Mass Assignment: Full Server Compromise Diagram of Hoppscotch mass assignment vulnerability CVE-2026-50160 causing full server compromise
  • Vulnerability Report

CVSS 10 Hoppscotch Mass Assignment: Full Server Compromise

Do Son June 29, 2026 0

A CVSS 10 Hoppscotch mass assignment flaw leads to full server compromise. Unauthenticated attackers can exploit CVE-2026-50160 to overwrite JWT secrets.
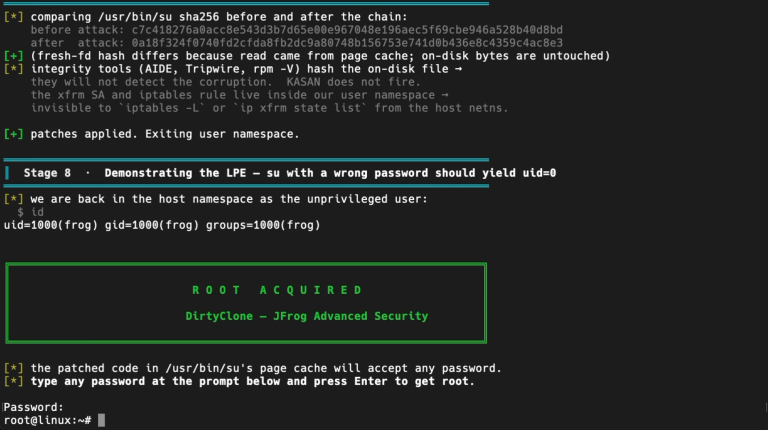
DirtyClone Linux Kernel Flaw Lets Local Users Get Root DirtyClone Linux kernel privilege escalation flaw CVE-2026-43503 page cache exploit
  • Vulnerability Report

DirtyClone Linux Kernel Flaw Lets Local Users Get Root

Do Son June 28, 2026 0

DirtyClone (CVE-2026-43503) is a Linux kernel privilege escalation flaw rated CVSS 8.8. It abuses the page cache to turn a local user into root.

GPT-5.6 Sol Model Launched Amid Strict Security Reviews GPT-5.6 Sol model capabilities and AI cybersecurity impact
  • Technology

GPT-5.6 Sol Model Launched Amid Strict Security Reviews

Do Son June 28, 2026 0

Discover the GPT-5.6 Sol model launch. OpenAI introduces Terra and Luna tiers while navigating strict US cybersecurity reviews and a restricted preview.

Claude Mythos 5 Returns: US Government Lifts AI Ban Claude Mythos 5 AI cybersecurity model unbanned by US government
  • Technology

Claude Mythos 5 Returns: US Government Lifts AI Ban

Do Son June 28, 2026 0

Anthropic's powerful Claude Mythos 5 cybersecurity AI model returns following a strict US government ban. Discover the impact on Silicon Valley.
libssh2 Vulnerability CVE-2026-58050 Gets Public PoC Exploit libssh2 vulnerability CVE-2026-58050 publickey subsystem heap buffer overflow PoC exploit
  • Vulnerability Report

libssh2 Vulnerability CVE-2026-58050 Gets Public PoC Exploit

Do Son June 28, 2026 0

Researchers publicly disclosed a libssh2 vulnerability, CVE-2026-58050, with PoC code. A malicious SSH server can corrupt a client's heap. Patch now.
CPython Tarfile Vulnerability Exposes Systems Diagram explaining the CPython tarfile vulnerability and CVE-2026-11940 bypass
  • Vulnerability Report

CPython Tarfile Vulnerability Exposes Systems

Do Son June 28, 2026 0

A new CPython tarfile vulnerability (CVE-2026-11940) allows directory escape attacks. Learn how this extraction filter bypass exposes systems.

US Seizes Domains to Stop Illegal World Cup Streaming Law enforcement officials announce domain seizures to stop illegal World Cup streaming.
  • Cybercriminals

US Seizes Domains to Stop Illegal World Cup Streaming

Do Son June 27, 2026 0

US authorities halted illegal World Cup streaming via nearly 400 domain seizures. Discover how Operation Offsides protects viewers from malware.
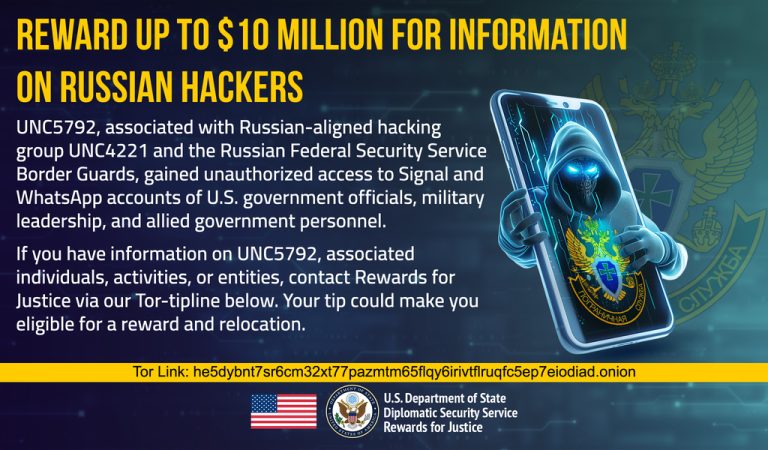
US Offers $10 Million Reward for Russian Hacker Group UNC5792 UNC5792 Rewards for Justice $10 million reward Russian Signal phishing group
  • Cybercriminals

US Offers $10 Million Reward for Russian Hacker Group UNC5792

Do Son June 27, 2026 0

The U.S. offers a $10 million reward for UNC5792, a Russian FSB-linked group behind Signal and WhatsApp phishing of officials.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-120322CVSS 9.4
    A vulnerability was identified in Termix-SSH Termix up to 2.9.2. This issue affects some unknown processing of the...
    📅 Updated: Nov 2, 2026
  • CVE-2026-120283CVSS 10.0
    A vulnerability was identified in Linksys E8450 1.2.00.360516. Affected is the function strcpy of the file /www/cgi-bin/portal.cgi. Such...
    📅 Updated: Nov 2, 2026
  • CVE-2026-120282CVSS 9.4
    A vulnerability was determined in WAVLINK WN536AX6-A V260507. This impacts the function host_black of the file /protocol.csp. This...
    📅 Updated: Nov 2, 2026
  • CVE-2026-120281CVSS 10.0
    A vulnerability was found in WAVLINK WN536AX6-A V260507. This affects the function strcpy of the file /protocol.csp of...
    📅 Updated: Nov 2, 2026
  • CVE-2026-120280CVSS 10.0
    A vulnerability has been found in WAVLINK WN536AX6-A V260507. The impacted element is the function wireguard_cli_group handler of...
    📅 Updated: Nov 2, 2026
  • CVE-2026-120279CVSS 10.0
    A flaw has been found in WAVLINK WN536AX6-A V260507. The affected element is an unknown function of the...
    📅 Updated: Nov 2, 2026
  • CVE-2026-120277CVSS 10.0
    A security vulnerability has been detected in WAVLINK WN536AX6-A V260507_2.0.0. This issue affects the function sub_41a1d8 of the...
    📅 Updated: Nov 1, 2026
  • CVE-2026-120276CVSS 10.0
    A weakness has been identified in WAVLINK WN536AX6-A V260507_2.0.0. This vulnerability affects the function sub_416760 of the file...
    📅 Updated: Nov 1, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.