Skip to content
November 2, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
CPython Tarfile Vulnerability Exposes Systems Diagram explaining the CPython tarfile vulnerability and CVE-2026-11940 bypass
  • Vulnerability Report

CPython Tarfile Vulnerability Exposes Systems

Do Son June 28, 2026 0

A new CPython tarfile vulnerability (CVE-2026-11940) allows directory escape attacks. Learn how this extraction filter bypass exposes systems.

US Seizes Domains to Stop Illegal World Cup Streaming Law enforcement officials announce domain seizures to stop illegal World Cup streaming.
  • Cybercriminals

US Seizes Domains to Stop Illegal World Cup Streaming

Do Son June 27, 2026 0

US authorities halted illegal World Cup streaming via nearly 400 domain seizures. Discover how Operation Offsides protects viewers from malware.
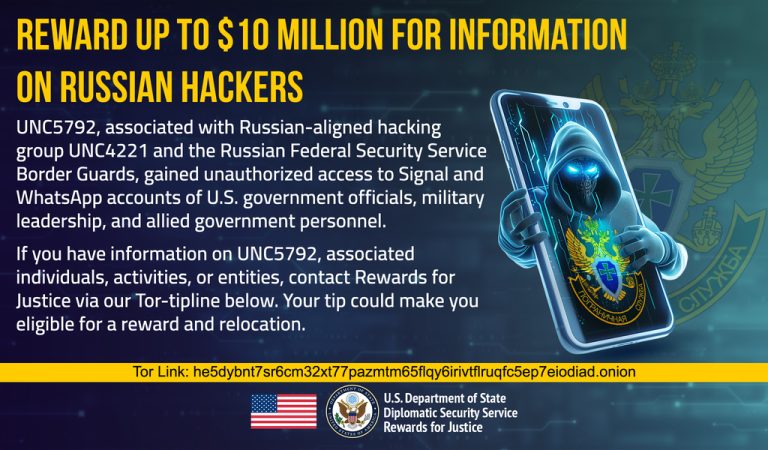
US Offers $10 Million Reward for Russian Hacker Group UNC5792 UNC5792 Rewards for Justice $10 million reward Russian Signal phishing group
  • Cybercriminals

US Offers $10 Million Reward for Russian Hacker Group UNC5792

Do Son June 27, 2026 0

The U.S. offers a $10 million reward for UNC5792, a Russian FSB-linked group behind Signal and WhatsApp phishing of officials.
Mistic Backdoor Linked to Ransomware Access Broker Mistic backdoor malware and ransomware access broker diagram
  • Malware

Mistic Backdoor Linked to Ransomware Access Broker

Do Son June 27, 2026 0

A new Mistic backdoor malware campaign linked to a ransomware access broker targets multiple sectors. Learn how this stealthy threat evades detection.
Langflow Cryptominer Malware Exploits CVE-2026-33017 Trojanized streaming site causing Packagist themes iOS spyware infections
  • Malware

Langflow Cryptominer Malware Exploits CVE-2026-33017

Do Son June 27, 2026 0

A new Langflow cryptominer malware campaign exploits CVE-2026-33017 to deploy malicious payloads. Learn how this threat spreads and how to stay protected.
Cisco SD-WAN Zero-Day Exploited in Attacks Diagram explaining the Cisco SD-WAN zero-day and CVE-2026-20245 exploitation
  • Cybercriminals

Cisco SD-WAN Zero-Day Exploited in Attacks

Do Son June 26, 2026 0

A threat actor exploited a Cisco SD-WAN zero-day (CVE-2026-20245) to gain root access. Learn how this attack happened and how to secure your networks.

Windows 10 Extended Security Updates Prolonged to 2027 Illustration of the Microsoft Windows 10 extended security updates timeline stretching to October 2027
  • Technology

Windows 10 Extended Security Updates Prolonged to 2027

Do Son June 26, 2026 0

Discover how Microsoft silently prolonged Windows 10 extended security updates for consumers to October 2027, mirroring Firefox's legacy support strategy.

WhatsApp Malware Campaign Spreads RMM Software Diagram showing the WhatsApp malware campaign and VBScript infection chain
  • Cybercriminals

WhatsApp Malware Campaign Spreads RMM Software

Do Son June 26, 2026 0

A new WhatsApp malware campaign uses a multi-stage VBScript infection chain to silently install RMM software on victim devices across multiple countries.

Fake Shop Campaigns Target Europe Fake shop campaigns selling counterfeit goods in Europe
  • Cybercriminals

Fake Shop Campaigns Target Europe

Do Son June 26, 2026 0

Researchers uncovered massive fake shop campaigns targeting Europe. Attackers sell counterfeit goods by impersonating major brands and exploiting World Cup.

FOSSBilling Template Injection Flaw Exploited in the Wild Nextcloud website hacked showing unauthorized Cloudbox phishing redirect and wp2shell vulnerability.
  • Vulnerability Report

FOSSBilling Template Injection Flaw Exploited in the Wild

Do Son June 26, 2026 0

A FOSSBilling template injection flaw (CVE-2026-28496, CVSS 9.4) is exploited in the wild. Patch to 0.8.0 now to stop server-side template injection.

OXLOADER Malware Loader Spreads CASTLESTEALER via Fake Node.js Ads TanStack Typosquatting npm Supply Chain Attack Axios Supply Chain Attack npm Poisoning eScan Supply Chain Attack Antivirus Compromise APT-36, NCERT WhatsApp Advisory FBI alert, Salesforce Salt Typhoon, APT group ConnectWise ScreenConnect hack Nation-state cyberattack FortiGate Leak - zkLend vulnerability - TRIPLESTRENGTH Threat Actor Group Dark Storm
  • Malware

OXLOADER Malware Loader Spreads CASTLESTEALER via Fake Node.js Ads

Do Son June 26, 2026 0

The OXLOADER malware loader spreads via malicious Google Ads, dropping the CASTLESTEALER infostealer with heavy obfuscation and anti-VM checks.
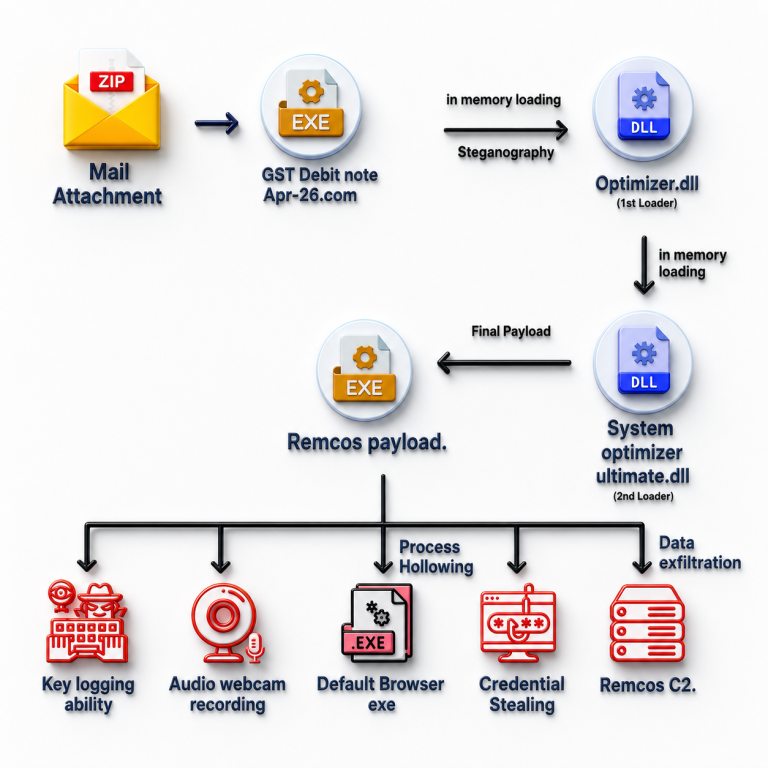
Remcos RAT Delivered by a Steganographic Loader in Phishing Emails Remcos RAT delivered by a steganographic loader hidden in a bitmap image
  • Malware

Remcos RAT Delivered by a Steganographic Loader in Phishing Emails

Do Son June 26, 2026 0

A steganographic loader hides Remcos RAT inside a bitmap and runs it in memory. K7 ties the fileless campaign to India via fake GST lures.

Python Patches python.org API Authentication Bypass Flaw python.org authentication bypass affecting Python release metadata and download API
  • Vulnerability Report

Python Patches python.org API Authentication Bypass Flaw

Do Son June 26, 2026 0

Python fixed a python.org authentication bypass in its release metadata API. The flaw, dormant since 2014, let attackers alter download URLs.

Curl v8.21.0 Release Fixes 18 Security Flaws Graphic illustrating the massive curl v8.21.0 release patching 18 security vulnerabilities globally
  • Vulnerability Report

Curl v8.21.0 Release Fixes 18 Security Flaws

Do Son June 26, 2026 0

Discover the massive curl v8.21.0 release featuring 18 security patches, many identified by AI models. Upgrade now for enhanced safety and HTTP/3 capabilities.

The Rumored Claude Fable 5 Return: UI Glitch or Reality? Claude Fable 5 return UI glitch interface on Anthropic platform
  • Technology

The Rumored Claude Fable 5 Return: UI Glitch or Reality?

Do Son June 26, 2026 0

Discover the truth behind the Claude Fable 5 return rumors. Learn how a recent UI glitch and AWS updates hint at an imminent launch for this powerful AI.

Apple Price Increase Hits Macs, iPads, and Vision Pro Apple price increase chart showing higher Mac iPad and Vision Pro prices driven by the AI memory shortage Vision Pro M5, Dual Knit Band
  • Technology

Apple Price Increase Hits Macs, iPads, and Vision Pro

Do Son June 26, 2026 0

The Apple price increase raises Mac, iPad, HomePod, Apple TV, and Vision Pro prices on the memory shortage. iPhone, Watch, and AirPods are spared.
CISA Adds Cisco Unified CM and PTC Windchill Flaws to KEV Catalog CISA KEV Catalog adding CVE-2026-20230 Cisco Unified CM and CVE-2026-12569 PTC Windchill vulnerabilities
  • Vulnerability Report

CISA Adds Cisco Unified CM and PTC Windchill Flaws to KEV Catalog

Do Son June 26, 2026 0

CISA added two flaws to its KEV Catalog: a Cisco Unified CM SSRF bug and a PTC Windchill RCE. Federal agencies must patch by June 28, 2026.

Public Exploits Released for Three Gogs RCE Flaws, CVSS Up to 10 Gogs RCE vulnerability with public proof-of-concept exploit code, CVSS up to 10
  • Vulnerability Report

Public Exploits Released for Three Gogs RCE Flaws, CVSS Up to 10

Do Son June 26, 2026 0

Public proof-of-concept code targets three Gogs RCE vulnerabilities scoring up to CVSS 10. Update self-hosted Gogs to version 0.14.3 right now.

Chrome Security Update Patches Three High-Severity Browser Flaws Chrome security update patching CVE-2026-13281 and other Chrome 149 vulnerabilities
  • Vulnerability Report

Chrome Security Update Patches Three High-Severity Browser Flaws

Do Son June 26, 2026 0

Google's Chrome security update patches three high-severity flaws in Mojo, Payments, and AdFilter. Update to 149.0.7827.200 now to stay protected.
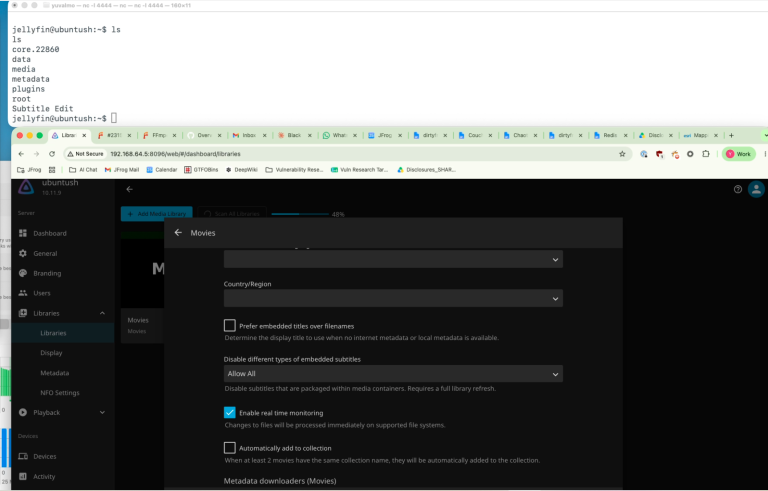
FFmpeg MagicYUV Vulnerability Exposes Media Applications Diagram explaining the FFmpeg MagicYUV vulnerability and CVE-2026-8461 exploit flow
  • Vulnerability Report

FFmpeg MagicYUV Vulnerability Exposes Media Applications

Do Son June 26, 2026 0

A critical FFmpeg MagicYUV vulnerability (CVE-2026-8461) allows attackers to achieve remote code execution via crafted media files. Patch systems quickly.
Langflow Security Vulnerabilities Expose AI Systems Diagram of Langflow security vulnerabilities CVE-2026-55255 CVE-2026-55447 CVE-2026-55450
  • Vulnerability Report

Langflow Security Vulnerabilities Expose AI Systems

Do Son June 26, 2026 0

Three critical Langflow security vulnerabilities (CVE-2026-55255, CVE-2026-55447, CVE-2026-55450) expose AI applications to RCE and DoS attacks. Patch now.

Critical Event-Driven Ansible Flaw Leaks Stored Credentials Event-Driven Ansible flaw causing credential disclosure of tokens and SSH keys
  • Vulnerability Report

Critical Event-Driven Ansible Flaw Leaks Stored Credentials

Do Son June 26, 2026 0

A missing authorization flaw in Event-Driven Ansible (CVE-2026-11807, CVSS 9.6) leaks credentials like OAuth tokens, vault passwords, and SSH keys.

❮ Prev Page
Next Page ❯

Search

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-20051CVSS 7.4
    A vulnerability with the Ethernet VPN (EVPN) Layer 2 ingress packet processing of Cisco Nexus 3600 Platform Switches...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2026-20118CVSS 6.8
    A vulnerability in the handling of an Egress Packet Network Interface (EPNI) Aligner interrupt in Cisco IOS XR...
    Watchtower Verified📅 Updated: Nov 1, 2026
  • CVE-2010-20125CVSS 8.7
    DedeCMS before 5.7 contains a file inclusion vulnerability in plus/carbuyaction.php that allows remote unauthenticated attackers to control the...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2015-20130CVSS 5.1
    Netsweeper before 4.0.11 and 4.1.0 before 4.1.5 contains a reflected cross-site scripting vulnerability in webadmin/reporter/view_server_log.php that allows remote...
    Watchtower Verified📅 Updated: Oct 30, 2026
  • CVE-2026-111357CVSS 7.0
    Ivanti Connect Secure 22.8R2.4 mishandles the manner in which the dsinvoked broker trusts DSCache configuration data, leading to...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118527CVSS 4.3
    Use of predictable filenames in Ivanti Connect Secure before versions 25.1.1.3 and 22.8R2.6 allows a remote authenticated attacker...
    CISA KEV📅 Added to KEV: Oct 30, 2026
  • CVE-2026-118539
    This module enables you to sell goods and services to customers through an included shopping cart and checkout...
    Admin intel📅 Updated: Oct 29, 2026
  • CVE-2022-31034CVSS 8.3
    Impact All versions of Argo CD starting with v0.11.0 are vulnerable to a variety of attacks when an...
    Watchtower Verified📅 Updated: Oct 29, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2025-11969CVSS 9.4
    The System REST APIs do not correctly enforce access control mechanisms, allowing users with lower privilege roles to...
    📅 Updated: Nov 2, 2026
  • CVE-2026-120345CVSS 10.0
    A vulnerability was found in WAVLINK WN551X3-A M51X3_V251020-WO-182e965. This impacts the function sub_41a430 of the file /bin/ioos of...
    📅 Updated: Nov 2, 2026
  • CVE-2026-120344CVSS 10.0
    A vulnerability has been found in WAVLINK WN551X3-A M51X3_V251020-WO-182e965. This affects the function system of the file /bin/ioos...
    📅 Updated: Nov 2, 2026
  • CVE-2026-120322CVSS 9.4
    A vulnerability was identified in Termix-SSH Termix up to 2.9.2. This issue affects some unknown processing of the...
    📅 Updated: Nov 2, 2026
  • CVE-2026-120283CVSS 10.0
    A vulnerability was identified in Linksys E8450 1.2.00.360516. Affected is the function strcpy of the file /www/cgi-bin/portal.cgi. Such...
    📅 Updated: Nov 2, 2026
  • CVE-2026-120282CVSS 9.4
    A vulnerability was determined in WAVLINK WN536AX6-A V260507. This impacts the function host_black of the file /protocol.csp. This...
    📅 Updated: Nov 2, 2026
  • CVE-2026-120281CVSS 10.0
    A vulnerability was found in WAVLINK WN536AX6-A V260507. This affects the function strcpy of the file /protocol.csp of...
    📅 Updated: Nov 2, 2026
  • CVE-2026-120280CVSS 10.0
    A vulnerability has been found in WAVLINK WN536AX6-A V260507. The impacted element is the function wireguard_cli_group handler of...
    📅 Updated: Nov 2, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.