Skip to content
October 22, 2026
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube

Daily CyberSecurity

Zero-hour alerts. Unmatched analysis.

Primary Menu
  • Home
  • CVE Data
    • CVE Watchtower
    • Top Exploited CVEs
    • CVE Stats by Vendor
    • Q2 2026 Report
    • CVE Alerts
    • CVE Alert Settings
    • Pricing
  • Cyber Criminals
  • Data Leak
  • Free Tools
    • CVSS 3.1 Calculator
    • Certificate Viewer
    • DNS Lookup
    • Encoder & Hash Generator
    • IP / Subnet Calculator
    • Whois Lookup
  • Linux
  • Malware
  • Vulnerability
  • Submit Press Release
  • Weekly Recap
Light/Dark Button
  • Home
  • News
  • Cyber Security
  • Samsung allegedly hit by hackers
  • Cyber Security

Samsung allegedly hit by hackers

Do Son March 5, 2022 2 minutes read
Samsung hackers

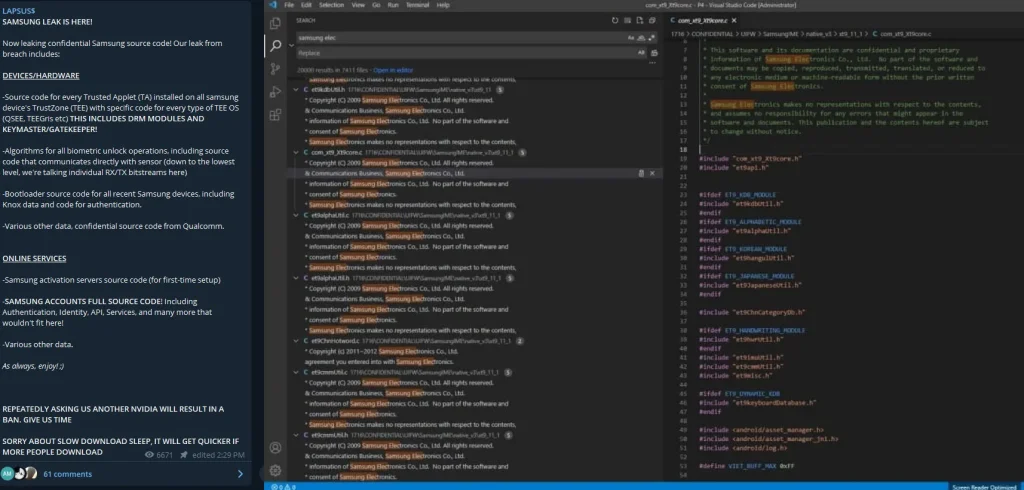
LAPSUS$ on Samsung hack, Source:@vxunderground

Add Daily CyberSecurity as a preferred source on Google
Previously, Nvidia was attacked by a hacker group, which resulted in the leakage of more than 1TB of data, including drivers, design drawings, and firmware. Some of the information that has been released so far includes the LHR algorithm, NVIDIA’s unreleased GPU, NVIDIA DLSS source code, NVIDIA employee login credentials, and two code signing certificates. The hacking group is now trying to sell the stolen information to third parties after a bad deal with Nvidia.

LAPSUS$ on Samsung hack, Source:@vxunderground
According to VideoCardz, the hacker group that previously attacked Nvidia claimed to have stolen data from Samsung’s servers and released some source code, including:
  • source code for every Trusted Applet (TA) installed in Samsung’s TrustZone environment used for sensitive operations (e.g. hardware cryptography, binary encryption, access control)
  • algorithms for all biometric unlock operations
  • bootloader source code for all recent Samsung devices
  • confidential source code from Qualcomm
  • source code for Samsung’s activation servers
  • full source code for technology used for authorizing and authenticating Samsung accounts, including APIs and services

The hacking group did not mention which servers were targeted at Samsung, which, if true, would have suffered a huge data breach, it may cause serious security incidents to itself and its related partners (such as Qualcomm), which would be very bad. The hacker group hasn’t mentioned the ransom issue or even communicated with Samsung.

Related coverage

  • ScreenConnect Vulnerabilities Exploited to Deploy Malware
  • North Korea’s Lazarus Group: A Persistent Threat to the Defense Sector
  • TA2726 & TA2727: Hackers Deploy Fake Updates to Spread Malware
  • Xeon Sender Abuses SaaS APIs for Massive SMS Attacks
  • Unit 42 Unmasks CL-STA-1087’s Years-Long Cyber Espionage Against Asian Militaries
  • Billbug Group Targets Southeast Asia in Sophisticated Espionage Campaign
Track all actively exploited CVEs →

Support Our Threat Intelligence

Find our threat intelligence and malware analysis helpful? Support our work today and unlock a 100% ad-free reading experience!

Buy Me a Coffee Logo Buy Me a Coffee
Select your plan
Free Pro Team

Hover over a plan to see its benefits.

Get Zero-Hour Vulnerability Alerts

Critical CVEs, CVSS scores, and PoC updates — straight to your inbox every week.

We respect your inbox. Unsubscribe anytime.

SHARE
Share on FacebookShare on XShare on LinkedInShare on TelegramShare on BlueskyShare on Mastodon
Written by
@DdoS · Security Researcher

Do Son

Do Son is the Founder and Editor of SecurityOnline.info. Working in cybersecurity since 2013, he reports on vulnerabilities, malware, and emerging threats, providing timely analysis to help organizations and individuals stay ahead of evolving risks.

Tags: Hackers samsung

Search

Translation

CVE ALERTS
📈

EPSS Spike Alerts
Catch risk spikes before they make headlines.

🎯

Custom EPSS/CVSS
Set score thresholds to effectively filter noise.

🛡️

Exploit Intel
Real-world exploit signals beyond the KEV catalog.

🐙

GitHub Issues
Auto-create alert tickets without duplication.

📬

Weekly Digest
Clean summaries, eliminating email spam.

🏷️

Watchlist Groups
Tag vulnerabilities by team (Infra/AppSec/SOC).

🔀

Smart Routing
Route chat channels based on severity levels.

🚨

RBP Tracker
Early warning detection and tracking system.

Subscribe – $7/mo or try free for 14 days →

🚨 Active Exploits in the Wild

  • CVE-2026-114625CVSS 9.9
    VeloCloud Orchestrator (VCO) on-prem has a security issue where this issue may allow a remote attacker to access...
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2020-13125CVSS 7.2
    An issue was discovered in the "Ultimate Addons for Elementor" plugin before 1.24.2 for WordPress, as exploited in...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2020-13126CVSS 9.9
    An issue was discovered in the Elementor Pro plugin before 2.9.4 for WordPress, as exploited in the wild...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2019-20180CVSS 8.0
    The TablePress plugin for WordPress is vulnerable to CSV Injection in versions up to and including 1.14 via...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2026-109619CVSS 9.2
    PHP has various global state that temporarily points into request memory. In some scenarios, global state may not...
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2026-109618CVSS 9.2
    PHP uses longjmp() for out-of-memory (OOM) errors to exit the current context and abort handling of the request....
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2014-125131CVSS 5.1
    DedeCMS 5.6 and 5.7 contains a reflected cross-site scripting vulnerability that allows unauthenticated attackers to inject script by...
    Watchtower Verified📅 Updated: Oct 22, 2026
  • CVE-2015-20124CVSS 8.7
    Aspose Importer & Exporter plugin for WordPress before 3.0 contains a path traversal vulnerability that allows unauthenticated attackers...
    Watchtower Verified📅 Updated: Oct 22, 2026
Powered by CVE Watchtower

Critical Vulnerabilities

  • CVE-2026-114625CVSS 9.9
    VeloCloud Orchestrator (VCO) on-prem has a security issue where this issue may allow a remote attacker to access...
    Admin intel📅 Updated: Oct 22, 2026
  • CVE-2026-63887CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: scsi: target: iscsi: Bound iscsi_encode_text_output() appends to rsp_buf...
    📅 Updated: Oct 22, 2026
  • CVE-2026-63886CVSS 9.8
    In the Linux kernel, the following vulnerability has been resolved: scsi: target: iscsi: Validate CHAP_R length before base64...
    📅 Updated: Oct 22, 2026
  • CVE-2026-76531CVSS 9.9
    As part of Cisco's ongoing commitment to proactive security and product quality, Cisco has conducted a comprehensive internal...
    📅 Updated: Oct 22, 2026
  • CVE-2026-76474CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality, engineering teams for Cisco Emergency Responder,...
    📅 Updated: Oct 22, 2026
  • CVE-2026-76475CVSS 9.3
    As part of Cisco's ongoing commitment to proactive security and product quality, engineering teams for Cisco Emergency Responder,...
    📅 Updated: Oct 22, 2026
  • CVE-2026-76473CVSS 9.8
    As part of Cisco's ongoing commitment to proactive security and product quality, engineering teams for Cisco Emergency Responder,...
    📅 Updated: Oct 22, 2026
  • CVE-2026-76302CVSS 9.9
    As part of Cisco's ongoing commitment to proactive security and product quality, Cisco has conducted a comprehensive internal...
    📅 Updated: Oct 22, 2026
Powered by CVE Watchtower

Daily CyberSecurity

  • About SecurityOnline.info
  • Advertise with us
  • Announcement
  • Contact
  • Contributor Register
  • Login
  • Disclaimer
  • DCMA
  • Privacy Policy
  • About SecurityOnline.info
  • Advertise on SecurityOnline.info
  • Contact Us

When you purchase through links on our site, we may earn an affiliate commission. Here’s how it works

  • CVE Watchtower
  • CVE Statistics by Vendor 2026
  • Q3 2026 Report
  • Top Exploited CVEs
  • Bluesky
  • Facebook
  • Linkedin
  • Mastodon
  • RSS
  • Twitter
  • Youtube
© 2017 - 2026 Daily CyberSecurity. All Rights Reserved.