 Do Son
ReliaQuest found the Gryxa toolkit, AI-built malware that steals crypto credentials and spies on how defenders try to remove it across 324 hosts.
AI Malware

A new npm package uses prompt injection and token flooding for AI malware scanner evasion. Discover how attackers disrupt AI-assisted malware review.

Netskope uncovers TroyDen’s Lure Factory, an AI-powered operation using 300+ trojanized GitHub repos and a 29,000-year sleep to steal credentials.
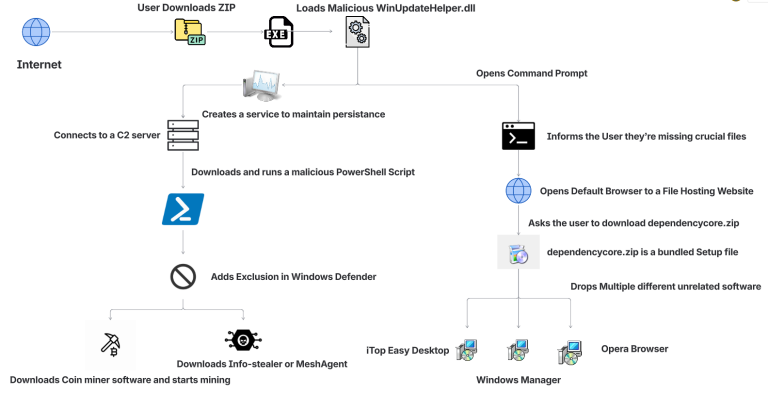
McAfee researchers found a massive malware campaign using LLMs to "vibe code" 1,700+ fake downloads. From Roblox mods to AI tools, your PC is the target.

BI.ZONE uncovers Forbidden Hyena using AI-generated code to deploy the new BlackReaperRAT and Milkyway ransomware in highly evasive cyberattacks.

Zscaler ThreatLabz uncovers Dust Specter, an Iran-linked cyber campaign hijacking Iraqi government infrastructure to deploy custom AI-assisted malware.
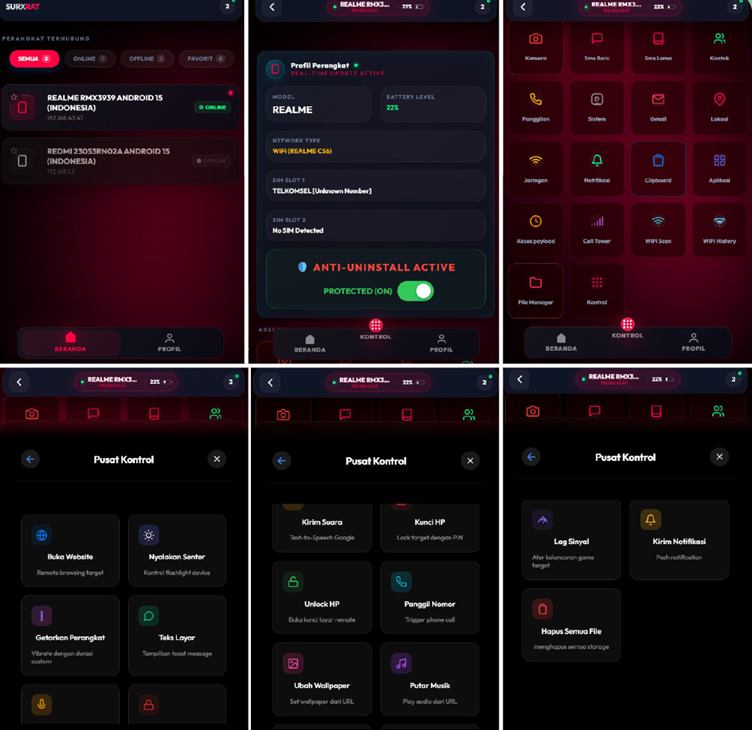
Cyble Research unmasks SURXRAT V5, a professionalized Android RAT experimenting with AI-assisted modules and hybrid monetization via Firebase infrastructure.
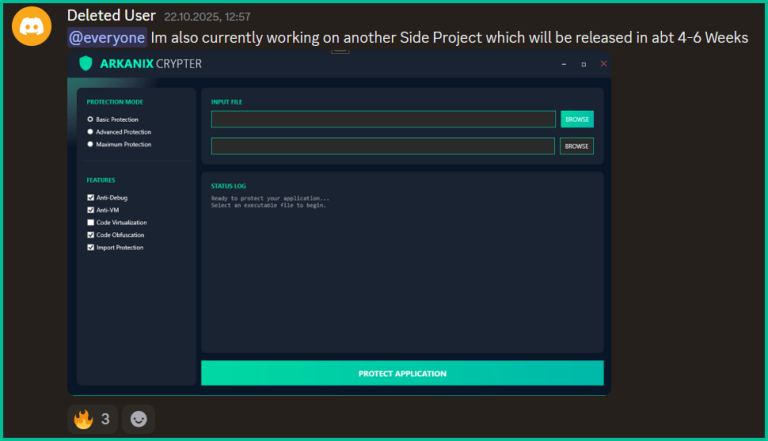
Kaspersky exposes Arkanix Stealer, a fast-moving MaaS operation leveraging Discord, tiered subscriptions, and AI-assisted development for quick data theft.
Proofpoint exposes TrustConnect, a new Malware-as-a-Service masquerading as an IT tool. The AI-assisted fake RMM software replaces dismantled threats.

"RedKitten" spies on Iranian protesters using AI-written malware. Attackers use fake death lists to deploy SloppyMIO surveillance tools.

New AI-generated malware campaign targets job seekers. Vietnamese actor "Huna" uses fake job offers to deliver PureRAT via Dropbox.

KONNI APT targets APAC developers with AI-generated malware disguised as crypto projects. The "polished" backdoor steals wallets & credentials.
CPR reveals VoidLink: the first advanced malware framework architected by AI. Using "Spec Driven Development," it reached functional status in under a week.

Aqua Security's Nautilus team discovered Koske, an advanced Linux cryptojacker likely crafted by AI, hiding in panda images and using rootkits for stealthy operations.

Attackers exploit fake AI video tools to deploy Noodlophile Stealer and XWorm, stealing credentials and data via Telegram bots.