 Do Son
The November 2026 bulletin resolves critical MediaTek vulnerabilities, including modem flaws CVE-2026-20499, CVE-2026-20545, and CVE-2026-20546.
Android security
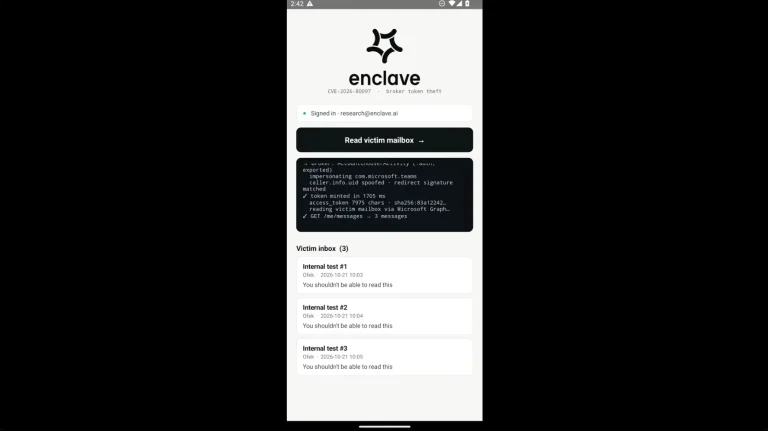
The Microsoft Authenticator AuthMask flaw allowed rogue Android apps to impersonate trusted software and hijack enterprise tokens and passkeys.
MediaTek security bulletin for October 2026 fixes 31 flaws, including critical MediaTek modem vulnerability CVE-2026-20519. Update now.
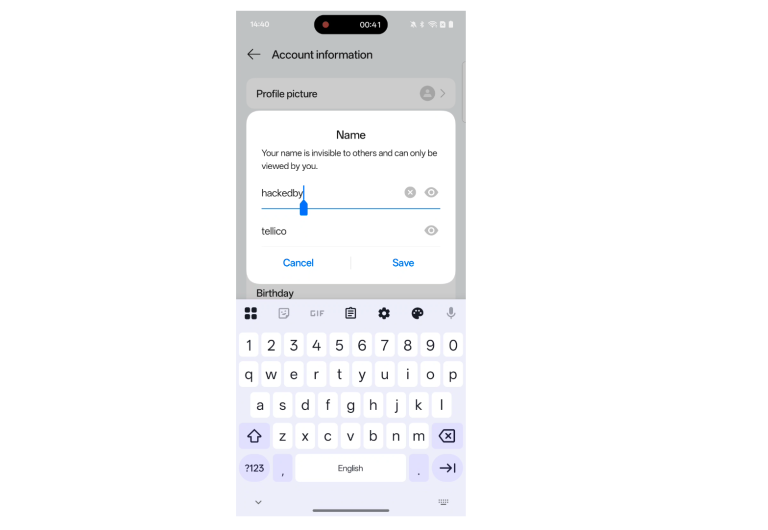
A disclosed OnePlus session takeover vulnerability threatens OnePlus 13R Android security, allowing malicious apps to steal tokens and modify user data.
Android 17 becomes the first major mobile OS to enable Encrypted Client Hello (ECH) by default, hiding visited website names from ISPs and network eavesdroppers.

A zero-click flaw in Xiaomi ShareMe (MiDrop) lets nearby attackers write files silently. Full details and PoC code are now public.

Google engineers propose restricting local ADB loopback connections on Android to close a security gap, a change that could break Shizuku and aShell.

Google patches a critical Android zero day flaw in the June 2026 security bulletin. Learn how to secure your device from active exploitation now.
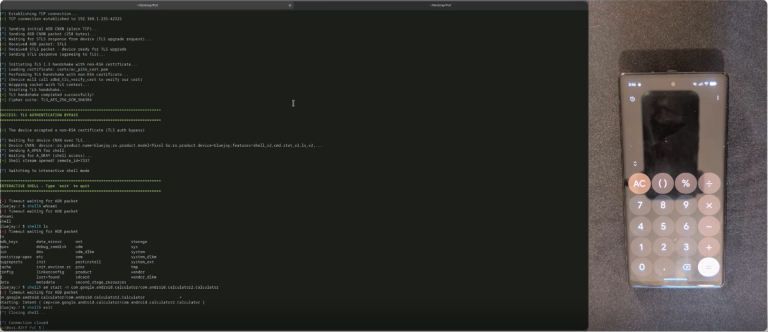
BARGHEST reveals CVE-2026-0073: a zero-click Android ADB bypass over Wi-Fi. Public PoC and exploit details are now live. Secure your mobile device today!

Qualcomm’s May 2026 bulletin reveals critical 9.8 CVSS flaws in Software Center & Bootloaders. Remote RCE and memory corruption affect millions of devices.

Microsoft warns of a 50M-user flaw in EngageSDK affecting crypto wallets. An intent redirection bug could leak private data. Update to v5.2.1 now!

McAfee unmasks Operation NoVoice: a sophisticated Android rootkit that survives factory resets to clone WhatsApp sessions and seize full device control.

Google’s April 2026 Android bulletin fixes a critical zero-interaction DoS in the Framework and high-severity StrongBox HSM flaws. Update your device now.
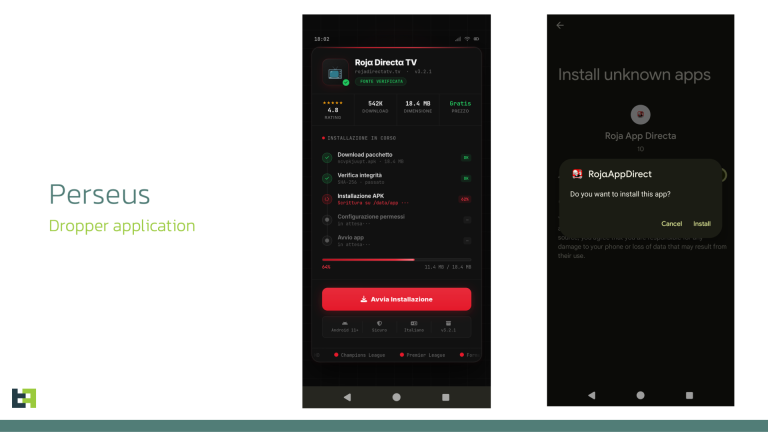
ThreatFabric uncovers "Perseus," an evolved Android malware targeting note-taking apps to steal recovery phrases and private data via accessibility services.

Ledger Donjon uncovers a critical MediaTek TEE flaw allowing attackers to extract PINs and crypto seed phrases in 45 seconds. Patch now.
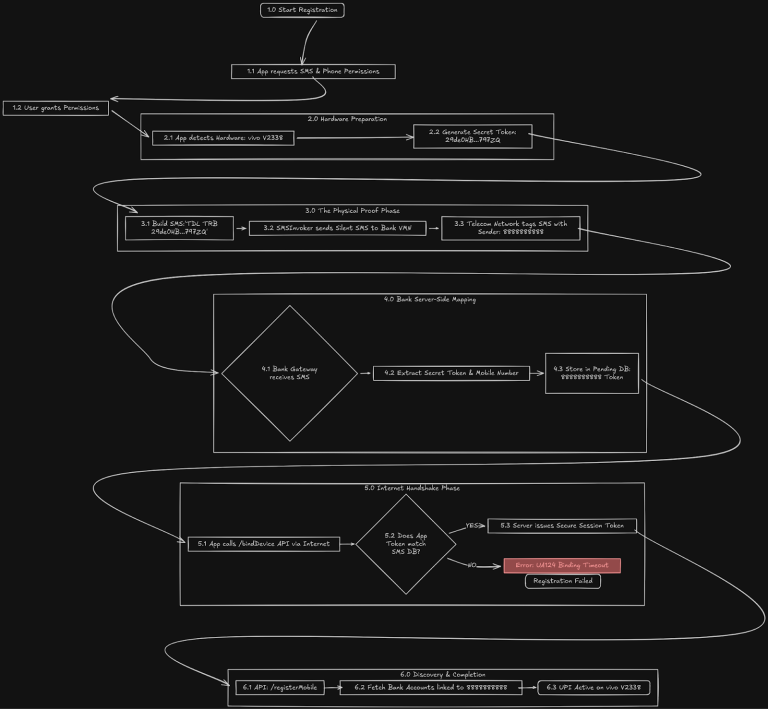
CloudSEK reveals how attackers use LSPosed and the "Digital Lutera" module to bypass Android UPI SIM-binding, gaslighting payment apps for remote fraud.
Google’s March 2026 Android update fixes 129 flaws, including CVE-2026-21385—a high-severity Qualcomm vulnerability currently being exploited in the wild.


Google disrupts IPIDEA proxy network. Fake VPNs and hijacked apps turned millions of devices into unwitting exit nodes. Play Protect is removing them.

New Android anti-theft updates use AI to detect "snatch-and-run" theft and instantly lock your screen. Identity Check adds biometric layers to stop thieves.
Public PoC exploit for Android CVE-2024-23700 allows critical privilege escalation without user interaction. WearOS & Custom ROMs are at risk.

WhisperPair flaw (CVE-2025-36911) exposes Google Fast Pair devices to hijacking and tracking. Update your headphone firmware now to block silent attacks.