 Do Son
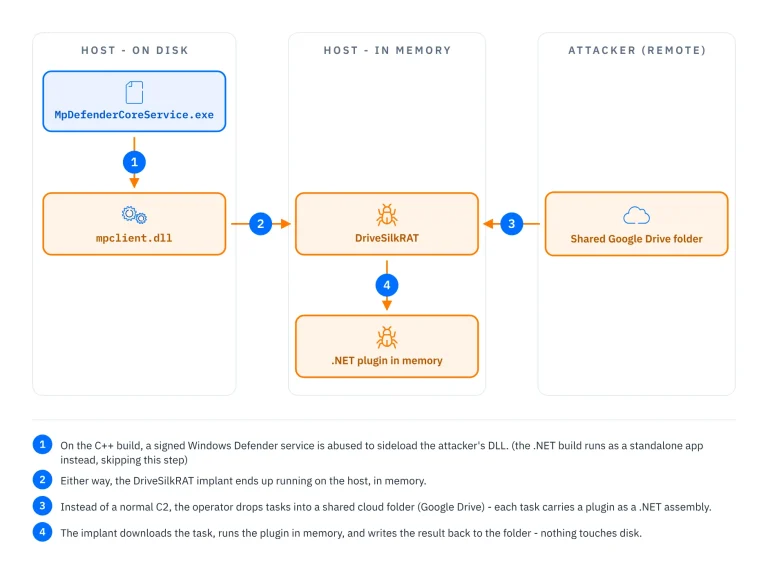
SilkParasite APT ran China-nexus cyberespionage across Central Asia, using 7 custom RATs, DLL sideloading, and AI-assisted malware.
Bitdefender

Cybercriminals are ramping up football fan scams and World Cup 2026 fraud. Protect yourself from fake merchandise, phishing, and lottery traps today.
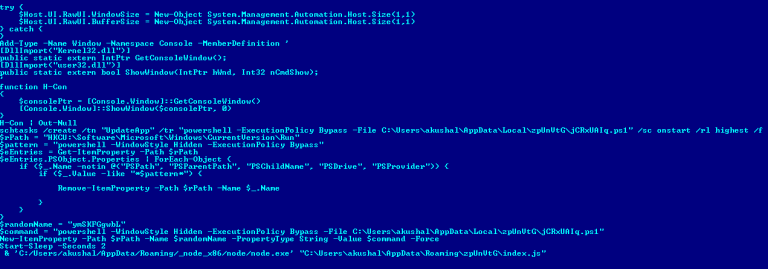
Bitdefender uncovers a malicious Windsurf IDE extension using the Solana blockchain as an unblockable C2 to steal developer credentials and source code.
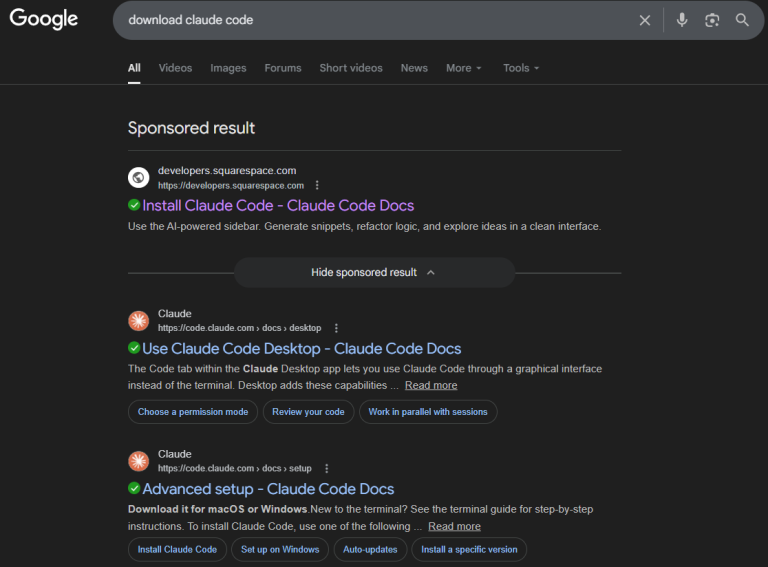
Bitdefender exposes a malvertising campaign targeting developers searching for Claude Code. Fake Google Ads deploy Windows stealers and macOS backdoors.

LummaStealer is back, evading takedowns with "ClickFix" tactics. Bitdefender reveals how fake CAPTCHAs trick users into running malware. Stay alert.

In a troubling convergence of trusted developer infrastructure and cybercrime, Bitdefender researchers have uncovered a sophisticated Android...

Qilin & North Korean hackers launch "Korean Leaks," a massive supply chain attack on South Korea's financial sector via a compromised MSP.

Cybercriminals are using fake Battlefield 6 cracks and trainers to deploy infostealers. Avoid "InsaneRamZes" & "RUNE" torrents to protect your data.

A new report reveals a Chinese APT group compromised a Philippine military company with a fileless malware framework called EggStreme, which uses DLL sideloading for stealth.

A new report reveals a global malvertising campaign on Facebook spreading an evolved version of Brokewell malware to steal crypto and bypass 2FA.

Bitdefender Labs uncovers "Curly COMrades," a Russian-aligned cyber-espionage group using a new backdoor, MucorAgent, to target government and energy sectors.
Bitdefender uncovers a large network of convincing mystery box scams on social media stealing credit card data via hidden subscriptions. Watch out!

Learn about the GravityZone Console Vulnerability, CVE-2025-2244, and its critical risks to system security.

Learn about CVE-2024-13871 & CVE-2024-13872 and critical vulnerabilities in Bitdefender BOX v1 that affect household security devices.

Learn about the urgent patch issued by Bitdefender for a critical vulnerability (CVE-2024-6980) in its GravityZone Update Server.

Bitdefender, a leading cybersecurity provider, has addressed a vulnerability (CVE-2024-4177) in its GravityZone Console On-Premise product

Successful exploitation of CVE-2023-6154 (CVSS 7.8) requires the attacker to have local access to the target machine.