 Do Son
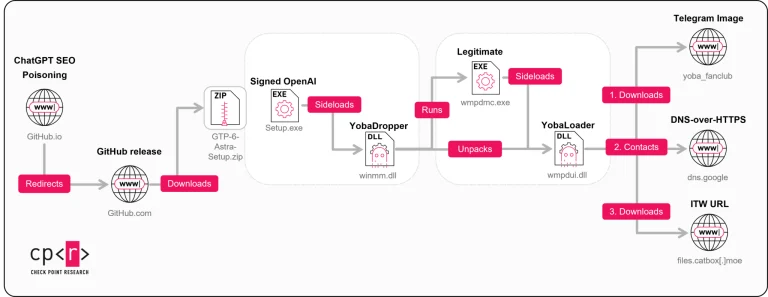
Check Point reveals the Yoba malware campaign. This GitHub Yoba malware campaign uses signed OpenAI and Anthropic binaries to sideload YobaLoader.
Check Point Research
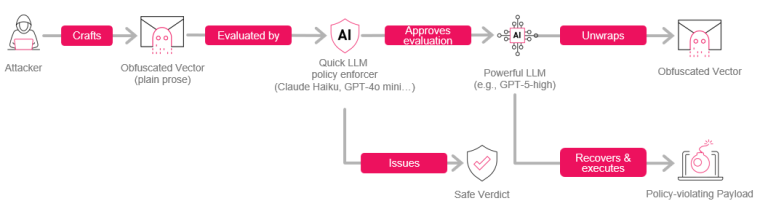
Researchers revealed the Puzzlemask AI attack, showing how this Puzzlemask AI attack vector bypasses quick LLM security filters using plain prose.
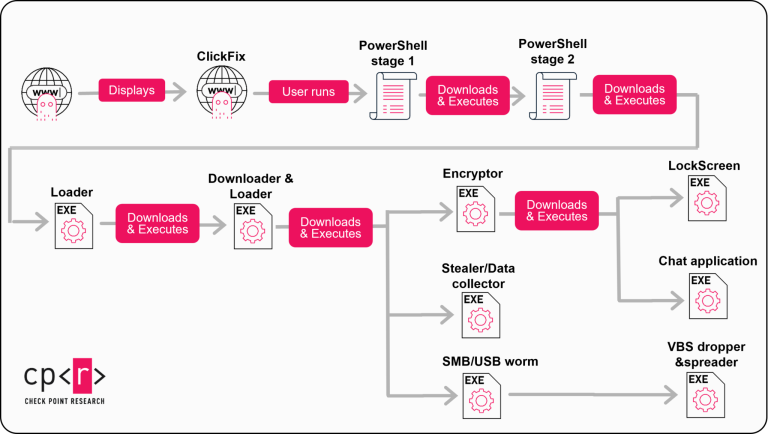
StopAndProtect malware turns hacked WordPress sites into a botnet for ransomware and data theft. Check Point exposed 5,000+ victims.
Discover how AI generated malware from DeepSeek turns hallucinated ideas into real browser native ransomware using the File System Access API.
Check Point exposed a crypto clipboard hijacker spread by fake Ghost Networks. The Rust clipper swaps wallet addresses to steal crypto. Stay alert.

16GB Rocket database leak exposes The Gentlemen ransomware cartel. Check Point Research unmasks their RaaS tactics, AI tools, and active exploits.
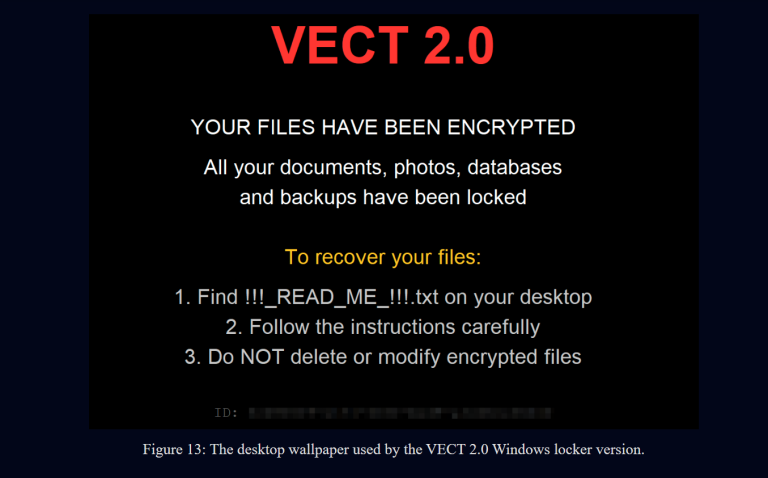
Check Point Research reveals VECT 2.0 ransomware is a broken wiper. A critical flaw makes file recovery impossible for files over 128KB. Read the analysis.

Check Point Research uncovers an Iran-linked password spraying campaign targeting M365 to support kinetic missile strikes and damage assessment in the ME.

Check Point Research uncovers a DNS tunneling flaw in ChatGPT allowing silent data theft. OpenAI deployed a fix on Feb 20, 2026. Is your AI chat truly private?

Check Point reveals "TrueChaos," an espionage campaign exploiting a TrueConf zero-day (CVE-2026-3502) to drop malware via fake updates. Patch to 8.5.3 now.
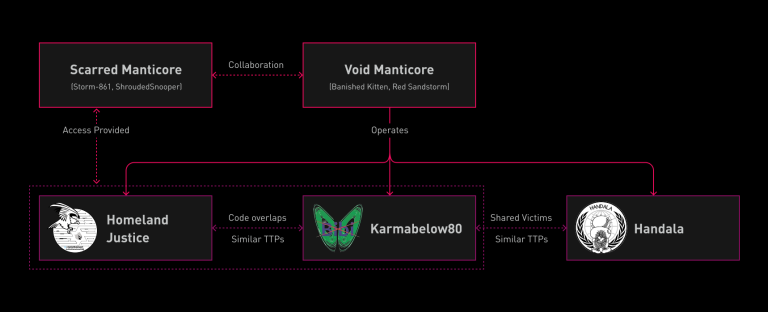
Check Point Research unmasks Handala Hack (Void Manticore), an Iranian MOIS threat actor using AI scripts and NetBird for destructive wiping attacks.
Blurring the Lines: How Iranian State Hackers are Weaponizing RaaS and the Cybercriminal Underground

Blurring the Lines: How Iranian State Hackers are Weaponizing RaaS and the Cybercriminal Underground
Check Point Research reveals Iranian state hackers (Void Manticore) are weaponizing RaaS and criminal malware like Rhadamanthys for plausible deniability.

A new Check Point Research report reveals how Iranian-nexus threat actors compromise IP cameras in the Middle East for real-time missile reconnaissance.

Check Point Research uncovers Silver Dragon, an APT41-linked group using the GearDoor backdoor and Google Drive for stealthy cyber espionage.

KONNI APT targets APAC developers with AI-generated malware disguised as crypto projects. The "polished" backdoor steals wallets & credentials.
CPR reveals VoidLink: the first advanced malware framework architected by AI. Using "Spec Driven Development," it reached functional status in under a week.

RondoDox botnet targets HPE OneView with 40k attacks in 4 hours. Critical RCE CVE-2025-37164 allows full system takeover. Patch immediately.

Check Point reveals Sicarii ransomware is a Russian false flag operation. Despite Israeli branding, the group relies on machine-translated Hebrew.

New "cloud-first" malware VoidLink targets Linux & containers with advanced stealth. Written in Zig, it mimics Cobalt Strike to evade EDR. Check your cloud.

New GoBruteforcer variant targets 50k+ servers by exploiting weak passwords from AI-generated code. Learn how this crypto-stealing botnet operates.

Check Point Research exposes the YouTube Ghost Network, using GachiLoader to spread Rhadamanthys infostealer through cracked software and game cheats.

Ink Dragon is weaponizing government servers in Europe using a relay-centric mesh. By hijacking IIS servers, they mask C2 traffic across global networks.