
 Do Son
ETH Zurich researchers unmasked "Fabricked" (CVE-2025-54510), a flaw in AMD Infinity Fabric that bypasses SEV-SNP memory isolation. Patch your firmware today!
Cloud Security
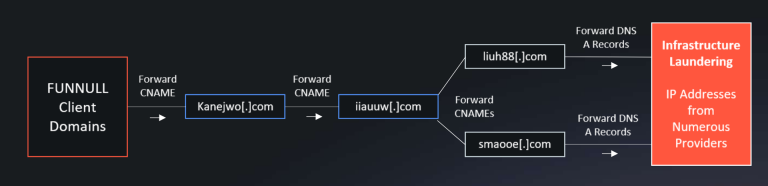
Triad Nexus has built a $300M fraud engine using "Infrastructure Laundering" on AWS and Google. See how they use geo-fencing and CNAME chains to evade the law.

A critical 9.1 CVSS flaw in OAuth2 Proxy allows unauthenticated users to bypass security via User-Agent spoofing. Secure your upstream apps—patch v7.15.2 today.
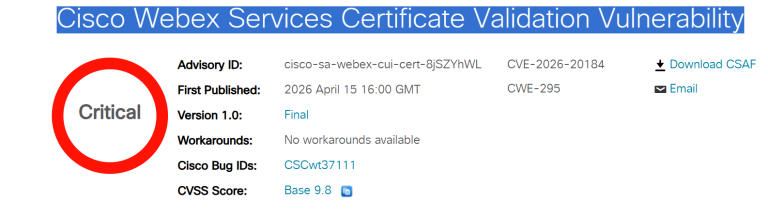
Cisco Webex CVE-2026-20184 allows unauthenticated user impersonation via SSO flaw. Fix requires a manual certificate update in Control Hub. Act now!

MinIO faces a critical 8.8 CVSS vulnerability allowing unauthenticated object writes by bypassing signature checks. Secure your AI/ML data—upgrade now!
Proofpoint warns that 10% of M365 account takeovers use malicious mailbox rules to steal data and hide alerts. Secure your cloud identity—check your rules!
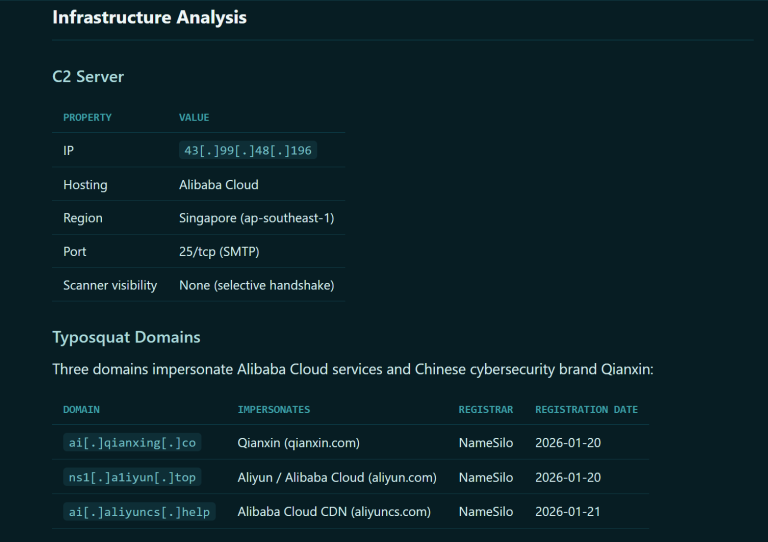
APT41's new zero-detection ELF backdoor uses SMTP (Port 25) to hijack Linux cloud workloads invisibly. Secure your credentials—audit your SMTP traffic today.

OpenStack Keystone vulnerability allows disabled LDAP users to authenticate. Logic flaw in attribute mapping affects releases up to 2026.1. Patch now!

Juju's critical CVSS 10 flaw (CVE-2026-5412) allows low-level users to steal master cloud credentials. Secure your AWS/Azure/GCP environments—upgrade now!

A critical CVSS 10 flaw in Axios (CVE-2026-40175) allows attackers to bypass AWS IMDSv2 and achieve RCE via header injection. Upgrade to v1.15.0 now!
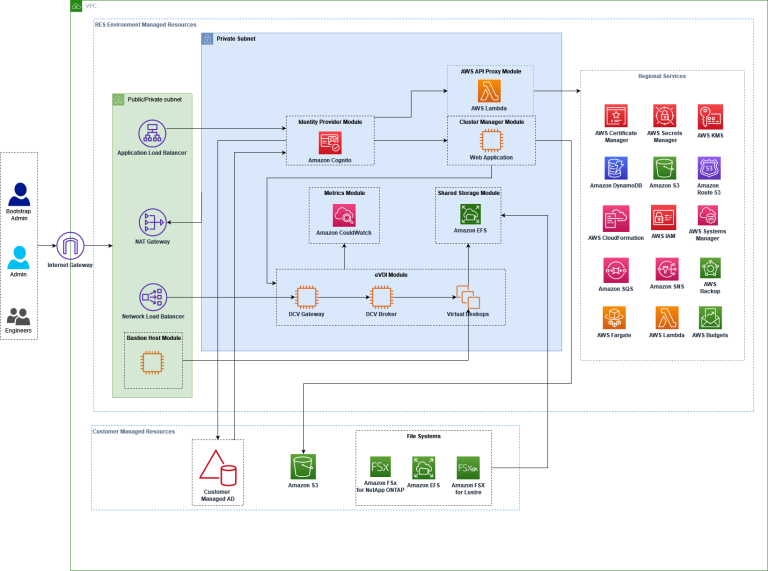
AWS patches critical RES flaws (CVE-2026-5707/8/9) allowing root access and instance profile hijacking. Protect your cloud lab—update to v2026.03 now.

OpenStack Keystone CVE-2026-33551 allows low-privilege users to bypass role restrictions and seize full S3 bucket control. Patch your cloud environment now!

AWS patches a high-severity (8.7) Firecracker flaw allowing root guests to trigger memory corruption via the virtio-pci transport. Update your microVMs now.

Cisco Talos uncovers UAT-10608, an automated campaign using "NEXUS Listener" to harvest Next.js credentials via React2Shell. Patch your cloud tokens now!

GPUBreach: A new GPU Rowhammer attack from UofT that bypasses IOMMU and ECC to achieve full system root on NVIDIA systems. GitHub code arrives April 13.
Juju hits a perfect 10.0 CVSS score (CVE-2026-4370). A TLS flaw on port 17666 lets attackers hijack clusters. Update to 3.6.20 or 4.0.5 now!

Google Drive's AI now detects 14x more ransomware. Learn how to use the new "infallible temporal anchor" for one-click file restoration in March 2026.

The European Commission confirms a cyber-attack on its Europa.eu cloud platform. Data was stolen, but core administrative systems remain untouched.
GoHarbor's Harbor faces a critical 9.4 CVSS flaw (CVE-2026-4404). Default admin passwords allow total registry compromise and image poisoning. Update now.
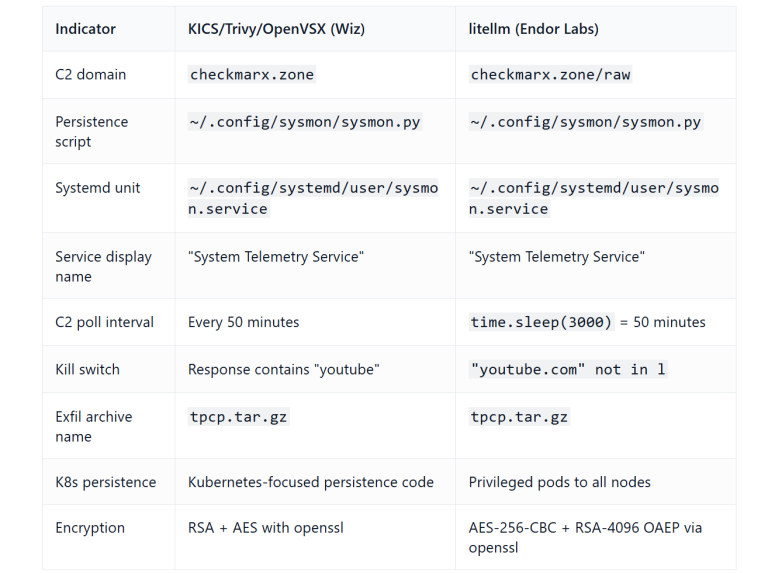
95M-download LiteLLM library hijacked on PyPI. TeamPCP's backdoor steals cloud tokens and hijacks Kubernetes clusters. Check for version 1.82.8 now.

A critical 9.8 CVSS vulnerability (CVE-2026-21994) in Oracle's Edge Cloud Infrastructure Toolkit allows unauthenticated remote attackers a total takeover.

Seqrite Labs exposes Operation CamelClone, a global cyber espionage campaign using the HOPPINGANT loader and public cloud services to evade detection.