 Do Son
Elastic Security Labs uncovered a CyberStrikeAI AWS intrusion and CyberStrikeAI AWS CloudTrail intrusion that pulled 56 EC2 scripts in 141 milliseconds.
Cloud Security
TSMC data breach confirmed: a TSMC employee data leak traced to a cloud provider. A seller claims 46,000 records and asks 3 BTC.
The October Railway security incident exposed up to 100,000 workspaces in a targeted AI keys breach. Learn how the attack happened and what to do.
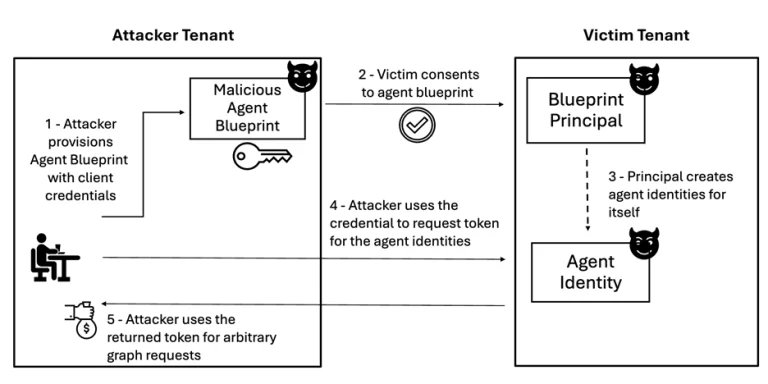
Proofpoint researchers detailed the BluePhishing attack Entra Agent ID technique, showing how malicious AI agent blueprints enable OAuth consent abuse.
A recent NVIDIA Brev security incident exposed virtual machine SSH keys, prompting emergency key rotations and security audits for AI developers.
SUSE fixed Rancher security vulnerabilities, including Rancher credential leak CVE-2026-88811, an SSRF flaw, and an unauthorized shell bypass. Update now.
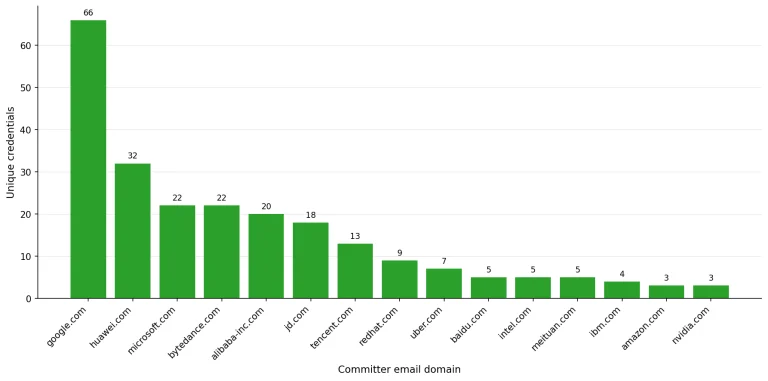
A security scan revealed over 26,000 Gitee exposed credentials across 7.25 million public repositories, affecting major cloud and AI platforms.
Hackers reduced the GMO Internet ransom demand from $50M to $1M and leaked victim files after the Japanese conglomerate ignored multiple bug warnings.
Wiz Research uncovered the Gheist campaign, a Gheist GitHub campaign planting 13,500 rogue branches across 850+ accounts to steal private repo secrets.
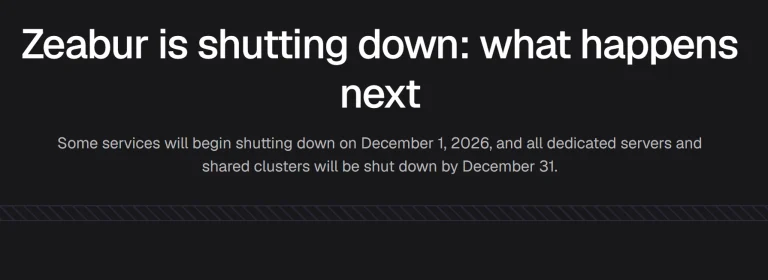
The Zeabur platform shutdown is set for December 2026 after an attacker read 3.21 million environment variables and 321,800 accounts.
Railway security incident: an attacker obtained some decrypted environment variables and builds were paused. Rotate API keys and secrets now.
PwnEscape (CVE-2026-99999) is a critical Linux kernel VM escape that let a guest run code as root on the host in lab tests. Update your kernel now.
AWS fixes Loom for AWS admin takeover CVE-2026-103956 and a SageMaker Unified Studio code execution bug, CVE-2026-104019. Patch now.
Microsoft ties a JADEPUFFER Azure attack to Storm-3168, the agentic ransomware actor that tried to delete 100+ storage accounts in seven minutes.
The Vite development server vulnerability CVE-2026-39364 is exploited in mass scanning for credential harvesting. F5 Labs logged 32,000 events. Patch now.
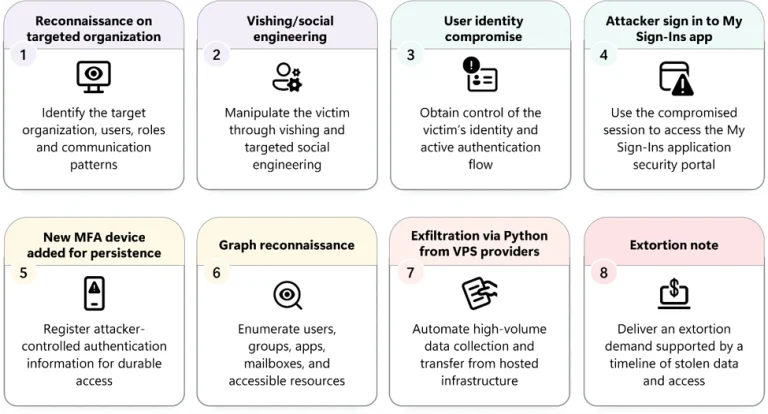
Microsoft warned of passkey social engineering attacks hitting tenants. Learn how passkey social engineering targets enterprise cloud identities.
Datadog uncovered an AWS password spraying campaign targeting cloud environments. Protect your accounts against this AWS password spraying activity now.
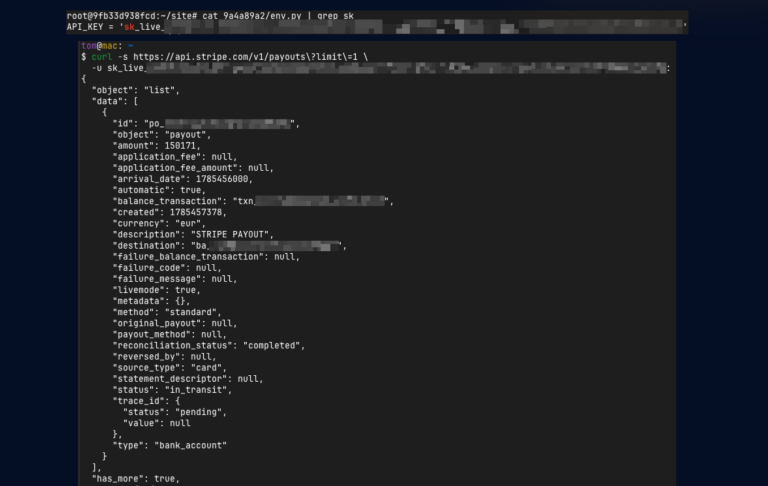
A scan found 28,000 exposed Git repositories leak credentials, API keys, and sensitive files. Learn how to secure your public web servers today.
CVE-2026-50112 is a critical Apache CloudStack flaw enabling cross-tenant remote code execution as root on KVM hosts. Upgrade to 4.20.3.1 or 4.22.1.1.
Truffle Security found leaked corporate AWS keys holding full control. See how leaked corporate AWS keys admin rights expose enterprise cloud accounts.
Sakura Internet disclosed a breach of its customer management system affecting 1.36 million accounts, though passwords were hashed and salted and no ransom was demanded.

UNC6671 vishing extortion group rebrands across five names, using AiTM credential phishing to hit financial services and enterprise cloud accounts.