 Do Son
Tenable exposes "LeakyLooker"—9 cross-tenant flaws in Google Looker Studio that let hackers manipulate and exfiltrate GCP data. Google has patched them.
Cloud Security
Google has finalized its $32B acquisition of Wiz, the largest in its history. Discover how this "code-to-cloud" platform secures AI in a multi-cloud world.
Datadog Security Research uncovers a sophisticated AiTM phishing campaign using real-time proxies to steal AWS Console credentials and bypass MFA in minutes.

Researchers discovered three major flaws in Amazon’s AWS-LC cryptographic library, allowing hackers to bypass digital signature validation. Update now.
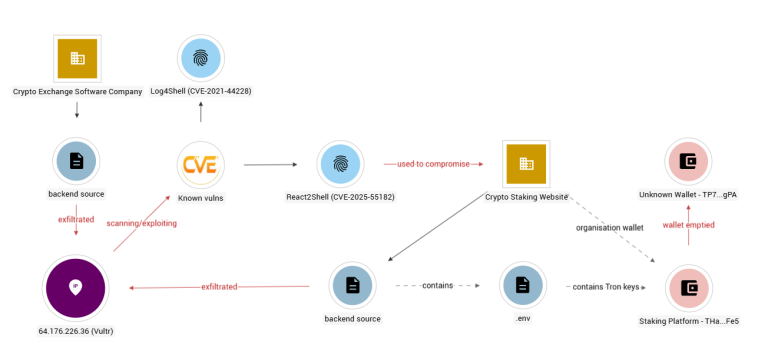
Ctrl-Alt-Intel exposes a suspected DPRK campaign using an 'Amazon Kill Chain' and React2Shell to systematically breach crypto exchanges and steal code.

A Mexican dev team faces bankruptcy after a leaked Gemini API key racked up an $82,314 bill in 48 hours. Is Google Cloud's billing model to blame?
Nokia discovers a critical 9.1 RCE flaw (CVE-2026-28370) in OpenStack Vitrage's RCA service. Patch immediately to prevent total host server takeovers.

OpenSSF warns of "hackerbot-claw," an autonomous AI bot exploiting GitHub Actions to hijack repositories. Secure your CI/CD pipeline before it’s too late.

RustFS patches a critical 9.1 CVSS XSS flaw (CVE-2026-27822). Attackers can steal S3 credentials via a malicious file preview. Update to 1.0.0-alpha.83 now!

ServiceNow patches a critical 9.2 CVSS RCE vulnerability (CVE-2026-0542) in its AI sandbox. Unauthenticated users could execute code remotely. Patch now!
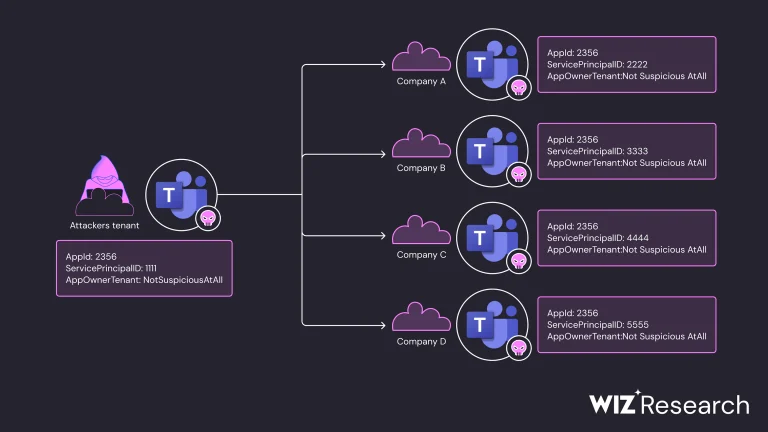
Wiz Research exposes a stealthy threat using malicious OAuth apps and Cyrillic homoglyphs to bypass Microsoft Entra ID security. Protect your cloud tenant.

Malicious Outlook add-in "AgreeTo" steals 4,000+ credentials. Attackers hijacked the abandoned tool in the official store. Uninstall immediately.
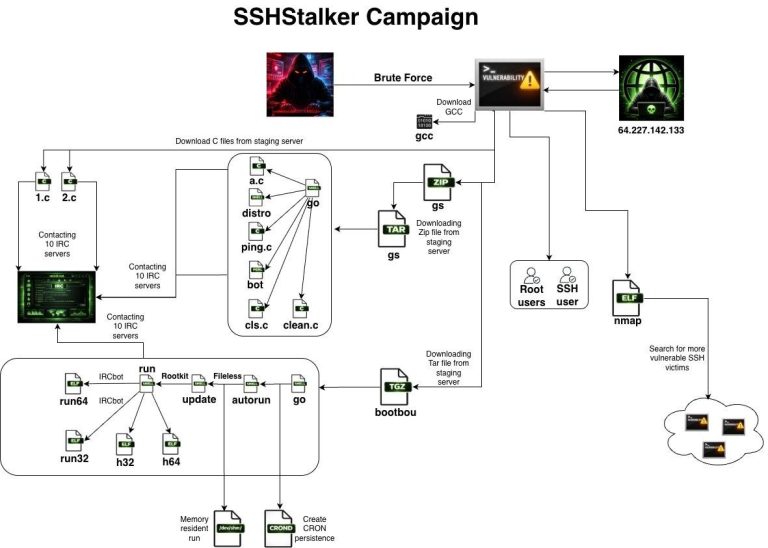
New SSHStalker botnet uses vintage IRC tactics & automated SSH brute-forcing to compromise Linux servers. Flare research reveals a "zombie army" in the making.

Cisco Talos reveals VoidLink, a modular Linux malware framework by UAT-9921. Features "compile-on-demand" tools to target IoT & cloud infrastructure.

Critical Keylime flaw CVE-2026-1709 (CVSS 9.4) disables mTLS in v7.12.0-7.13.0. Unauthorized clients can access the registrar. Update or firewall now.

Zscaler reveals Marco Stealer, a new malware harvesting crypto & cloud files. It uses AES-256 encryption & kills analysis tools. Learn how to detect it.

Sophisticated phishing abuses Vercel Blob & PDFs to bypass filters. Stolen credentials are exfiltrated via Telegram bots. Learn how to spot this attack.
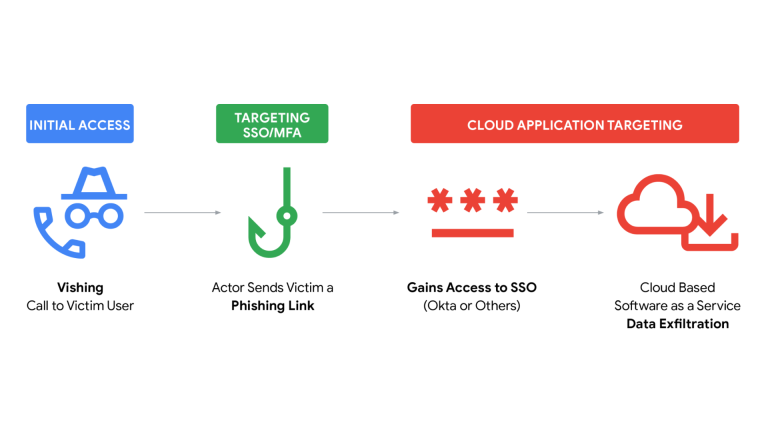
Mandiant warns of vishing rings like ShinyHunters impersonating IT support to bypass MFA and steal corporate cloud data. Verify your callers.

New "Exfil Out&Look" attack uses OWA add-ins to steal emails without leaving logs. Microsoft has no immediate fix for this blind spot.
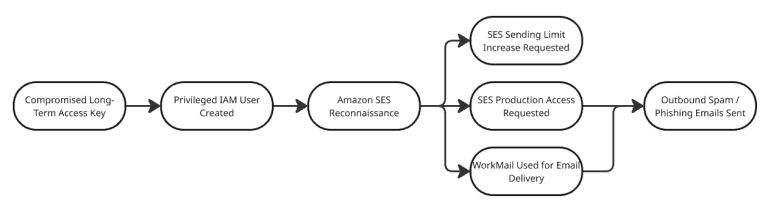
Attackers are bypassing AWS SES sandbox limits by pivoting to WorkMail. Rapid7 reveals how this abuse creates a blind spot for defenders.

Wiz reveals "CodeBreach": A regex typo in AWS CodeBuild could have let hackers hijack the AWS Console via the JS SDK. Issue is now patched.

OpenStack patches CVE-2026-22797 (Privilege Escalation). Flaw in OAuth2 middleware allows header forgery for admin access. Update keystonemiddleware now.