 Do Son
OVH patched CVE-2026-53359, a critical KVM flaw, across tens of thousands of hosts in under 10 days without warning most clients first.
Cloud Security

Proofpoint details OAuth client ID spoofing, a stealthy account enumeration technique probing Microsoft Entra ID without a successful sign-in event.

Researcher @Cereblab confirms the Grok Build repository upload bypasses privacy mode; SpaceXAI's /privacy only covers code snippet sharing.

A critical Mistral policy bypass flaw allows arbitrary code execution. Learn how to patch your workflow service to prevent security credentials theft.
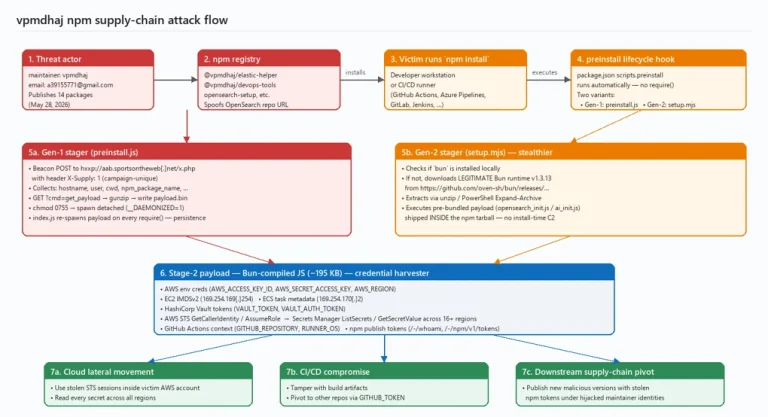
A critical npm supply chain attack exploits lookalike packages to distribute credential harvesting malware. Learn how to protect your cloud assets.
Discover how nation-state hackers leverage the ROADtools cloud attack toolkit to compromise Entra ID environments and bypass MFA controls.
Explore the critical Kata Containers container escape vulnerability (CVE-2026-47243). Technical details and PoC exploit code are now fully public.

A critical Fission router vulnerability (CVE-2026-46614) allows unauthenticated function invocation in Kubernetes. Learn how to patch it now.

Fix the critical Dell Container Storage Modules vulnerability (CVE-2026-40710). Learn how hardcoded credentials expose systems and update now.

A recent report shows persistent P2Pinfect botnet activity inside Google Kubernetes Engine via exposed Redis instances. Learn how to secure your network.
Google Threat Intelligence exposes UNC6671 ("BlackFile"), an aggressive group using vishing and AiTM proxies to bypass MFA in Microsoft 365 and Okta.

Despite a global takedown, Tycoon 2FA is back. It now abuses Microsoft's device code flow to bypass MFA entirely. Disabling this flow is critical.

Urgent: Apache CloudStack patches critical flaws (CVE-2026-25199, CVE-2026-25077) enabling VM hijacking and KVM host RCE. Secure your cloud environment now.

Scammers are leveraging Amazon SES and leaked IAM keys to bypass security filters. Learn how to protect your organization from this high-trust phishing surge.

Apache Polaris 1.4.1 fixes critical flaws allowing attackers to bypass S3/GCS boundaries and seize cloud credentials. Patch your Iceberg catalog now!
Jakob Wolffhechel reveals "Shittrix," 89 critical flaws in Citrix XenServer & XCP-ng. CVSS 9.9 bugs allow full host takeover. Assume compromise today.
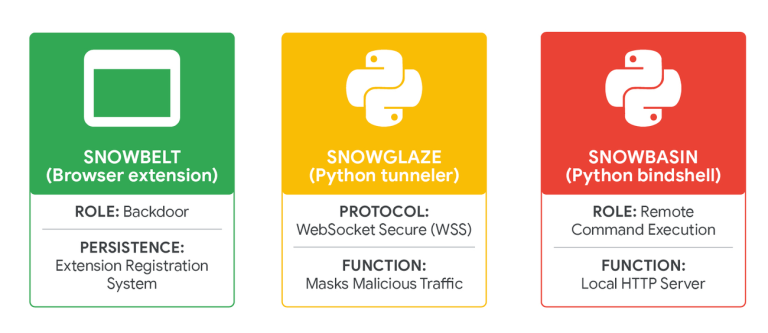
UNC6692 uses MS Teams impersonation to deploy the SNOW suite. Learn how "living off the cloud" bypasses reputation filters to hijack Active Directory.

Dr. Tube’s AI-assisted Bissa scanner exploited 900+ companies using React2Shell (CVE-2025-55182) to steal 30,000 .env files. See the AI-led attack workflow.
CVE-2026-33626: A critical SSRF in LMDeploy exploited in under 13 hours. Learn how attackers hijack AI nodes and how to secure your inference cloud now.
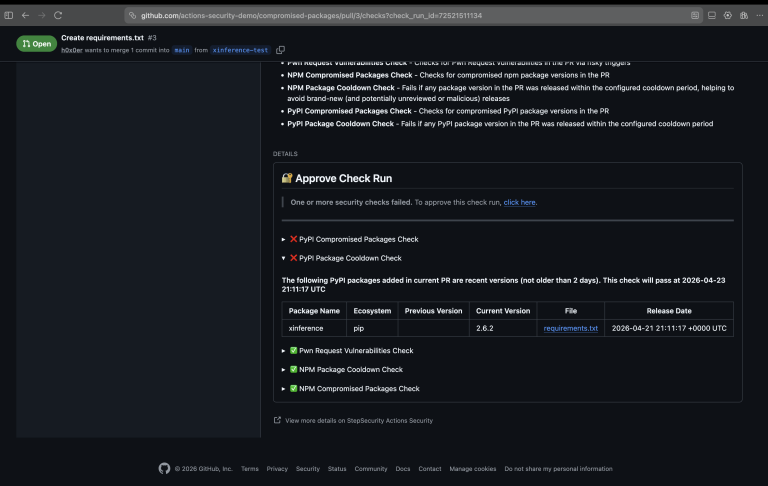
Critical supply chain attack hits Xinference (v2.6.0-2.6.2). TeamPCP’s malware siphons cloud credentials and MLOps secrets. Audit your MLOps pipeline today.

Two critical CVSS 10.0 RCE flaws in Spinnaker's Clouddriver and Echo services allow full JVM and shell access. Patch your multi-cloud pipelines immediately.

Atlassian’s new AI policy arrives Aug 17, 2026. Learn which tiers face mandatory data collection and how to protect your Jira and Confluence content.