 Do Son
A Red Canary report reveals attackers are exploiting an Apache ActiveMQ flaw to breach Linux systems, then patching the vulnerability to hide their presence.
Cloud Security

Proofpoint reveals an AiTM phishing campaign using fake OAuth apps and the Tycoon platform to bypass MFA, hijack Microsoft 365 accounts, and steal credentials.

Wiz Research uncovers Soco404, an evolving cryptojacking operation exploiting cloud misconfigurations and PostgreSQL to stealthily mine cryptocurrency across Linux and Windows.

A critical unauthenticated SSRF vulnerability (CVE-2025-54122, CVSS 10.0) in Manager.io's accounting software allows bypassing network isolation and exfiltrating sensitive data from cloud environments.

Unit 42 uncovers HazyBeacon, a novel backdoor using AWS Lambda URLs for stealthy C2. It's deployed via DLL sideloading, targeting Southeast Asian govts for trade documents.

SCATTERED SPIDER targets U.S. airlines with ransomware, vishing, and VMware exploits—CrowdStrike warns of a rising threat across cloud identities.

A flaw (CVE-2025-4679) in Synology ABM leaked a static client_secret, allowing unauthenticated attackers read-only access to all Microsoft 365 tenants with ABM installed.

Trellix uncovers "OneClik," a sophisticated APT campaign abusing Microsoft ClickOnce and AWS cloud services to deploy Go-language backdoors, targeting energy, oil, and gas sectors.

Mandiant Red Team breached Aviatrix Controller via auth bypass & RCE flaws CVE-2025-2171/2172—reached root, gained AWS keys. Full chain, no guesswork.
Trend Micro reveals misconfigured Kubernetes containers in AWS EKS can expose sensitive AWS credentials via unencrypted HTTP API, leading to privilege escalation risks.

Trend Micro uncovers a new attack method using misconfigured Docker Remote APIs and the Tor network to stealthily deploy cryptominers and establish persistent access.

Apache CloudStack LTS updates patch five security flaws, including two critical vulnerabilities in Kubernetes and admin access, risking full system compromise.

A high-severity flaw (CVE-2024-43706) in Kibana's Synthetic Monitoring allows unauthorized access. Upgrade to 8.12.1 or apply mitigations immediately.

High-severity flaws in Salesforce OmniStudio's FlexCard and Data Mapper expose encrypted customer data. Learn how to protect your organization.

Cisco issues advisories for high-severity flaws (CVSS 8.8, 8.7) in IMC and NDFC, risking privilege escalation and device impersonation. Patch immediately!
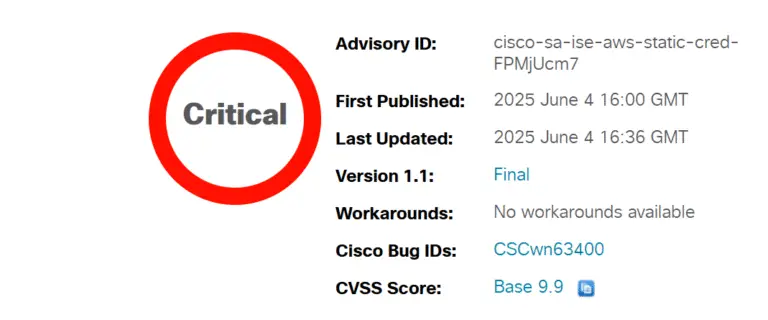
CVSS 9.9 flaw in Cisco ISE cloud deployments with public PoC exploit enables remote attacks on AWS, Azure, and OCI. Patch now.

Wiz uncovers JINX-0132, a cryptojacking campaign exploiting misconfigured Nomad, Consul, Docker, and Gitea in DevOps environments to mine Monero.

Learn about new vulnerabilities in VMware Cloud Foundation that could lead to unauthorized access, info disclosure, and unapproved actions.

Bitnami Pgpool flaw (CVE-2025-22248) exposes PostgreSQL to unauthenticated access. Update to Pgpool 4.6.0-1 or Helm chart 16.0.0 to fix.

Microsoft patched critical Azure & Power Apps security flaws before exploitation. No user action needed. Stay informed on cloud security.

Commvault updates its March advisory after detecting nation-state threat activity in Azure; no data breach confirmed, advanced defenses deployed.

Tenable Research discovered "ConfusedComposer," a GCP Composer vulnerability enabling privilege escalation. Learn how attackers could exploit Cloud Build permissions.