 Do Son
Unit 42 exposes the new Gremlin stealer. It uses memory-resident techniques to hijack active browser session tokens and completely bypass MFA.
Cyber Security
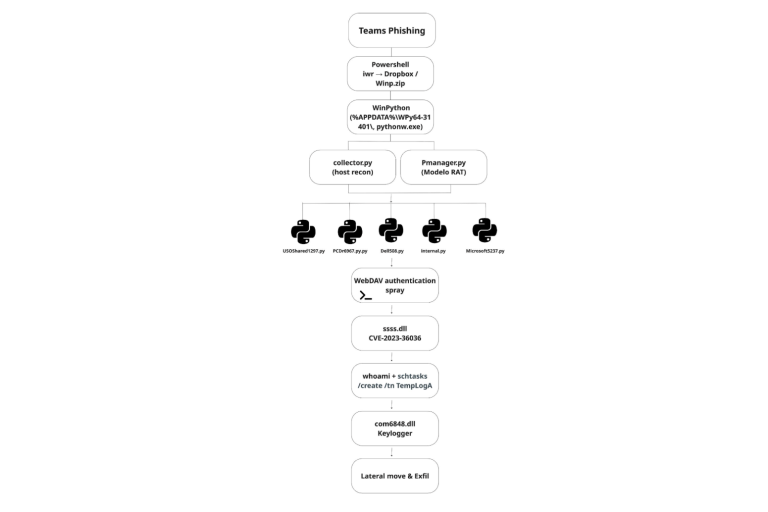
Rapid7 Labs exposes how attackers are abusing Microsoft Teams external access and Dumpit memory scrapers to breach corporate networks. Protect your team!
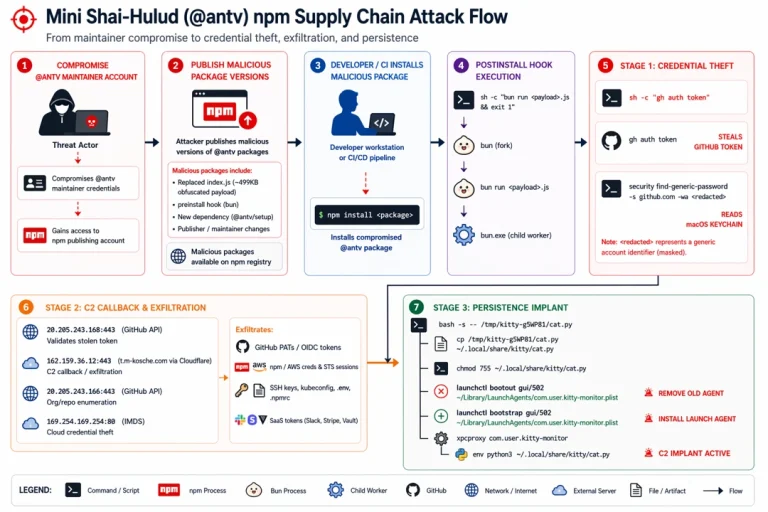
Microsoft warns of an aggressive Mini Shai-Hulud worm attack targeting the @antv npm ecosystem and stealing secrets from cloud-connected CI/CD pipelines.
Coder patches a critical 9.1 CVSS signature bypass (CVE-2026-46354) in Azure identities that allows unauthenticated workspace token theft. Patch now!
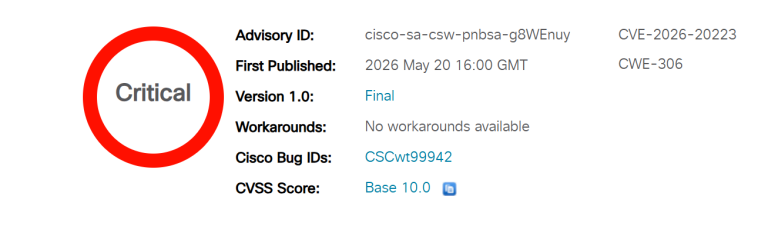
Cisco drops an urgent advisory for CVE-2026-20223 (CVSS 10.0) in Secure Workload. Unauthenticated remote attackers can steal full Site Admin privileges.
Unpatched CVSS 10 flaw (CVE-2026-45829) in ChromaDB allows unauthenticated remote code execution via Hugging Face models. Isolate your servers now!
Google has dropped an urgent Chrome desktop update fixing 16 vulnerabilities, including two critical sandbox subversion flaws in WebRTC and the UI.

Urgent: Drupal releases patches for highly critical SQLi flaw CVE-2026-9082. Unauthenticated attackers can exploit PostgreSQL backends for full remote RCE.

Apache OFBiz releases version 24.09.06 to patch severe RCE flaws, token forgery, and a critical password-reset authentication bypass. Upgrade now!

Technical details and a functional PoC exploit have been released for CVE-2026-41702, a VMware Fusion TOCTOU flaw granting instant root on macOS.

Point Wild exposes a sophisticated PyInstaller loader using in-memory AMSI patching and SHA-512 decryption to drop XWorm V7.4. Patch now!

Grafana Labs confirms a targeted cyberattack and source code theft after a missed token from the Mini Shai-Hulud npm worm left a repository exposed.
ZKTeco patches a critical 9.1 CVSS flaw (CVE-2026-8598) in CCTV cameras leaking admin credentials without authentication. Upgrade your firmware now!
Budibase patches a critical 9.9 CVSS SCIM authorization bypass (CVE-2026-46425). Basic users can delete admins and hijack accounts. Update now!
NVIDIA patches a critical 9.8 CVSS authentication bypass (CVE-2026-24207) in Triton Inference Server. Update to r26.03 to secure AI workloads!

FreePBX fixes critical 9.1 CVSS flaw (CVE-2026-46376) where hardcoded credentials grant unauthenticated portal access. Update your modules now!
Arcane fixes a critical 9.9 CVSS vulnerability (CVE-2026-45625) that allows basic users to steal GitOps credentials in plaintext. Update to 1.19.0!

Despite a global takedown, Tycoon 2FA is back. It now abuses Microsoft's device code flow to bypass MFA entirely. Disabling this flow is critical.

The Mini Shai-Hulud npm worm has hijacked the atool account, poisoning AntV & timeago.js to scrape GitHub runner memory. Execute a full reset now!

AI "vibe coding" and the EvilTokens PhaaS platform are supercharging device code phishing to bypass Microsoft 365 MFA. Secure your network today!

Urgent: Malicious Nx Console v18.95.0 briefly hit the VS Code Marketplace, targeting 2M+ installs with a macOS backdoor and token stealer. Audit now!

CVE-2026-46442 in Flowise allows authenticated users to escape the NodeVM sandbox and execute system commands. Secure your AI infrastructure now!