 Do Son
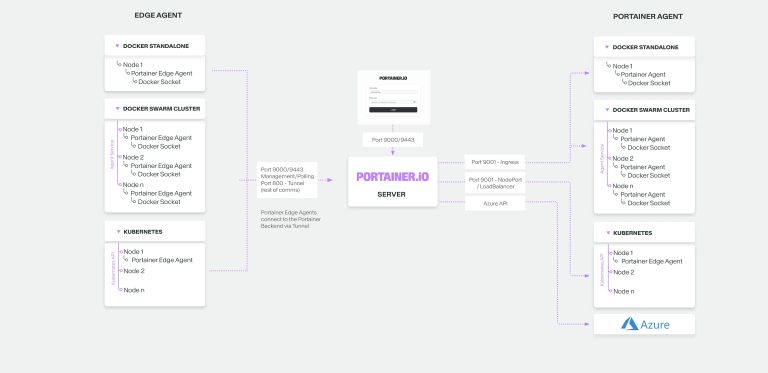
Portainer fixes two critical 9.4 CVSS flaws (CVE-2026-44848/49) allowing instant container escape to host root. Patch your environments now!
Cyber Security
Marten .NET library suffers a critical 9.8 CVSS SQL injection flaw (CVE-2026-45288). Learn how to block the exploit and patch your databases now!

Cato CTRL intercepts "TencShell," a new stealth malware derived from open-source Rshell. Attackers use third-party access to breach networks!

McAfee Labs exposes a massive CountLoader campaign using EtherHiding and AMSI bypass to drop stealthy cryptocurrency clippers. Secure your assets!

16GB Rocket database leak exposes The Gentlemen ransomware cartel. Check Point Research unmasks their RaaS tactics, AI tools, and active exploits.

Critical CVE-2026-35194 flaw in Apache Flink allows RCE via SQL injection on TaskManagers. Upgrade your clusters immediately to secure your data!
Two critical flaws in Strapi CMS (CVE-2026-27886 & CVE-2026-22599) allow unauthenticated admin takeover and SQL injection. Update your nodes now!
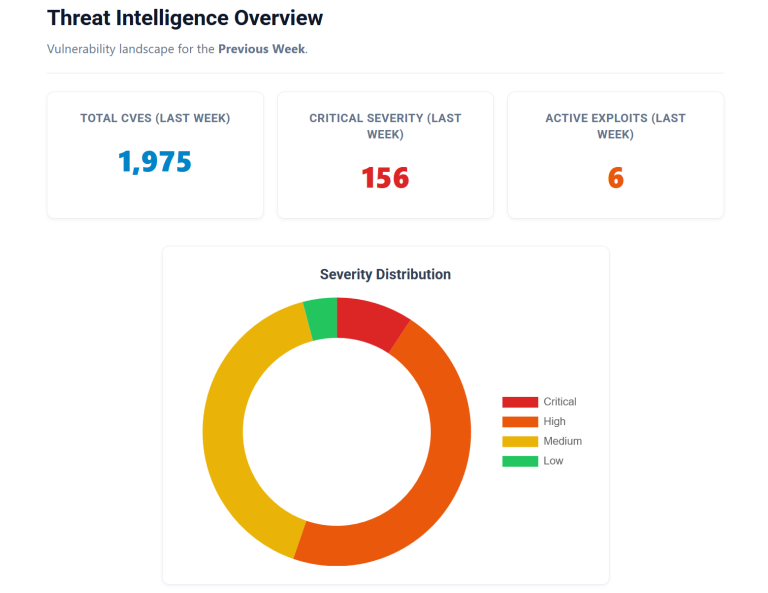
Cisco SD-WAN (CVE-2026-20182) and Exchange Server (CVE-2026-42897) are actively exploited in the wild! Discover the top threats you must patch now.

The GhostLock whitepaper exposes a critical blind spot in ransomware defense. Low-privilege users can freeze SMB shares with zero data encryption.
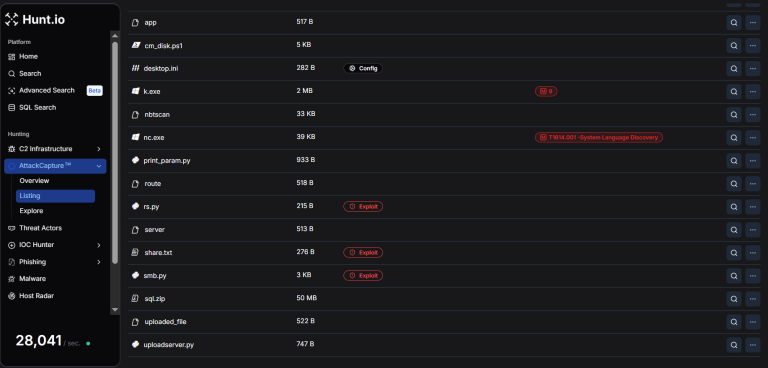
Quest KACE SMA CVE-2025-32975 (CVSS 10) exploited in the wild. Attackers bypass auth to seize admin control. Patch to version 14.1.101 or 14.0.341 now!

Paper Werewolf APT targets industrial sectors with PaperGrabber stealer and EchoGather RAT. Learn to detect their AI-assisted loaders and custom tools.
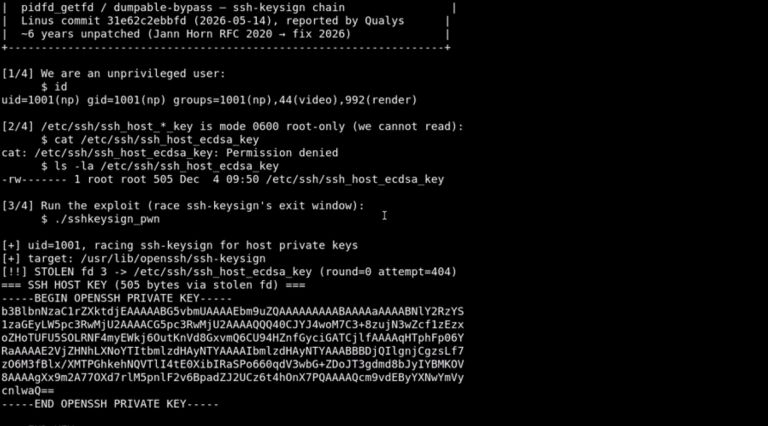
Technical details and PoC exploits disclosed for Linux Kernel ptrace flaw. Unprivileged users can steal root file descriptors. Patch to May 14 release!

cPanel & WHM fix 5 critical vulnerabilities (CVE-2026-29205). Fixes for arbitrary file read, SQLi, and privilege escalation are now live. Update now!

ELECOM routers hit by critical 9.8 CVSS flaws (CVE-2026-42062). Unauthenticated attackers can execute OS commands and bypass auth. Update firmware now!

CVE-2026-8178 in Amazon Redshift JDBC Driver allows RCE via unsafe class loading. Protect your data warehouse and update to version 2.2.2 now!

pgAdmin 4 v9.15 fixes a 9.4 CVSS auth bypass and multiple RCE flaws. Attackers can execute OS commands via SQL tools. Upgrade your pgAdmin server now!
Exploited in the Wild: Critical OWA Spoofing Flaw (CVE-2026-42897) Hits On-Premises Exchange Servers
Exploited in the Wild: Critical OWA Spoofing Flaw (CVE-2026-42897) Hits On-Premises Exchange Servers
CVE-2026-42897 exploited in the wild. A 8.1 CVSS OWA flaw allows RCE via malicious emails. Verify your Exchange Emergency Mitigation (EM) status now!

Google Chrome patches 79 vulnerabilities, including 14 "Critical" RCE threats. Update to version 148.0.7778.167 now to protect your data and browser.

NGINX 1.30.1 fixes a 9.2 CVSS RCE flaw (CVE-2026-42945) and five other critical vulnerabilities. Protect your web infrastructure and update immediately!

Palo Alto Networks patches CVE-2026-0263 and CVE-2026-0265. Fixes for IKEv2 RCE and CAS bypass are now available. Update your PAN-OS firewalls immediately!

CYFIRMA warns of Operation SilentCanvas: A weaponized JPEG delivers trojanized ScreenConnect, bypassing AMSI and UAC for full-system surveillance. Stay alert!

200,000+ sites hit by CVE-2026-8181. A 9.8 CVSS Burst Statistics flaw allows RCE via auth bypass. 5,000+ attacks blocked. Update to 3.4.2 immediately!