
 Do Son
GitLab patches high-severity XSS (8.7 CVSS) and unauthenticated DoS flaws in versions 18.11.3, 18.10.6, and 18.9.7. Secure your DevOps pipeline now!
Cyber Security

Ivanti issues an urgent patch for CVE-2026-8043, a critical 9.6 CVSS flaw in Xtraction allowing attackers to read files and write malicious HTML. Update now!

Urgent: A memory corruption flaw in MongoDB time-series collections (CVE-2026-8053) enables server takeover. Patch to versions 8.3.2, 8.0.23, or 7.0.34 now.

Urgent: Public PoC for OPNsense CVE-2026-44194 and CVE-2026-45158. Critical flaws allow root command execution via DHCP and User sync. Update to 26.1.8 now!

Public PoC for NGINX CVE-2026-42945. An 18-year-old RCE flaw in the rewrite module enables server takeover. Update to NGINX 1.31.0 or 1.30.1 immediately.

Public PoC for Fragnesia. This universal Linux LPE exploit allows unprivileged users to seize root via the page cache. Patch your kernel immediately!

Gen Digital exposes a JDownloader site breach (May 6-7, 2026). Attackers used WDAC policies to kill antivirus and r77 rootkits for total system invisibility.

GemStuffer exploits RubyGems as an illicit data transport to scrape UK council portals. Discover how this supply chain attack bypasses standard defenses.

Urgent: Public PoC for Apache CVE-2026-23918. A critical double-free in mod_http2 enables unauthenticated DoS and RCE. Update to Apache 2.4.67 immediately.

Microsoft’s May 2026 update fixes 137 vulnerabilities, including 30 Critical RCE and EoP flaws. Prioritize patches for Netlogon, Office, and M365 Copilot now.
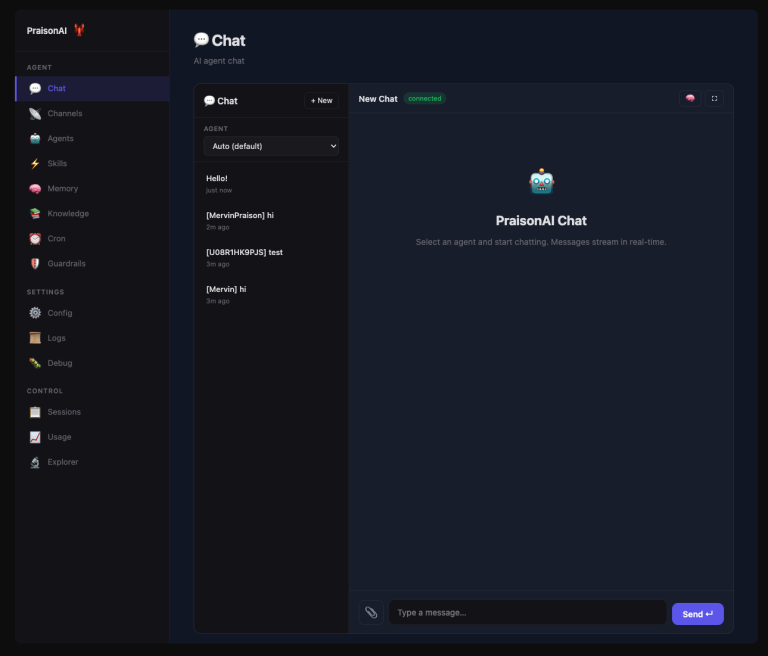
Sysdig warns: PraisonAI (CVE-2026-44338) exploited in under 4 hours. Attackers bypassed auth to hijack agents and drain API quotas. Update to 4.6.34 now!

Urgent: Fortinet warns of 9.1 severity flaws in FortiSandbox (CVE-2026-26083) and FortiAuthenticator (CVE-2026-44277). Patch now to prevent unauthorized RCE.
Urgent: Casdoor IAM platform hit by critical file write flaw (CVE-2026-44213). Attackers can bypass sandboxes to overwrite databases and gain host access.
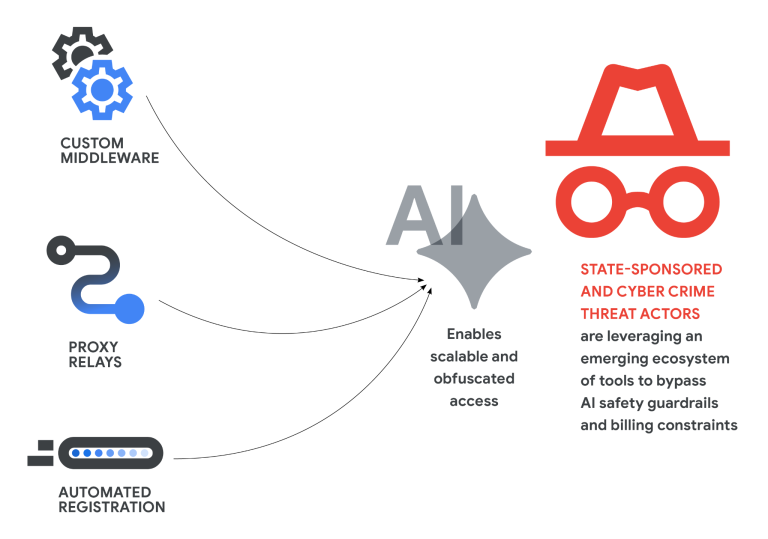
Google GTIG confirms the first AI-built zero-day exploit used in the wild. Discover how AI is industrializing cyber warfare and how Big Sleep is fighting back.
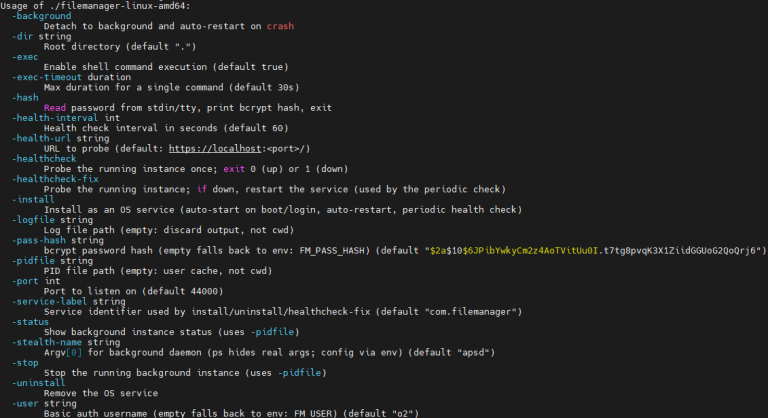
Urgent: cPanel & WHM hit by global 9.8 CVSS auth bypass. Over 2,000 IPs are actively hijacking servers for data theft and ransomware. Patch immediately!

SAP’s May 2026 Patch Day fixes two 9.6 severity flaws in S/4HANA and Commerce Cloud. Prevent SQL injection and RCE by updating your SAP landscape today.
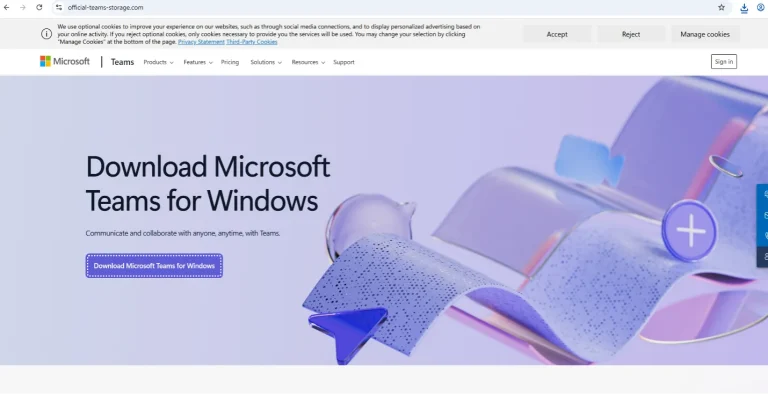
BlueVoyant unmasks "Lorem Ipsum": a well-funded campaign using SEO poisoning and signed MS Teams installers to deploy stealthy backdoors via image files.

Apache Tomcat RCE alert: CVE-2026-34486 exploit code and details are now public. A "fail-open" flaw enables RCE via Tribes clustering. Update immediately.
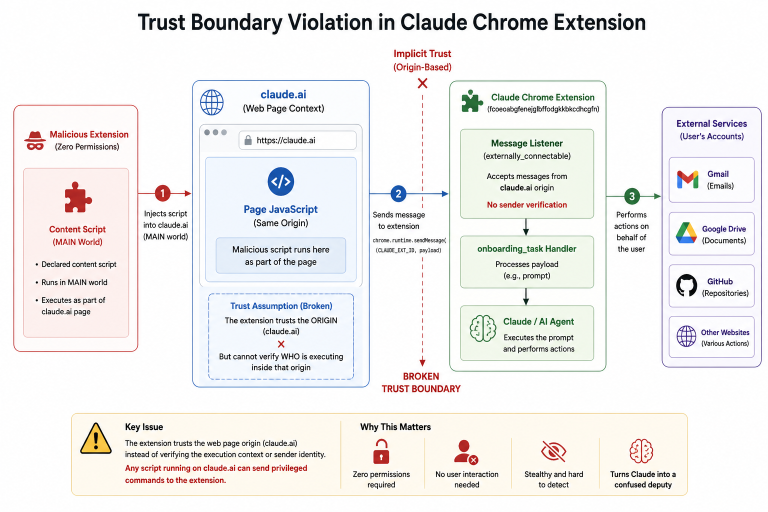
LayerX uncovers a critical flaw in Anthropic’s Claude extension. Learn how attackers can hijack AI agents to steal data and bypass security policies.

Apache Syncope CVE-2025-57738 allows root RCE via unsandboxed Groovy. Technical details and PoC are now public. Upgrade to v3.0.14 or 4.0.2 immediately.
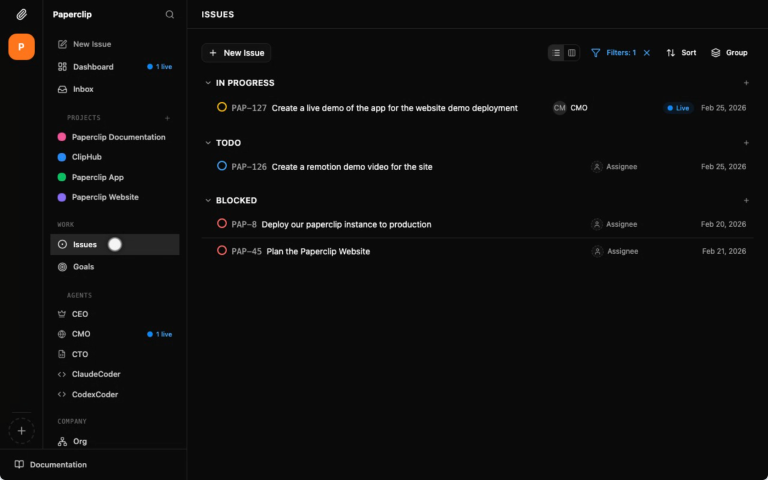
Paperclip’s 9.8 CVSS flaw and cross-tenant leaks expose AI agents to total takeover. Learn how a simple command could compromise your entire business.
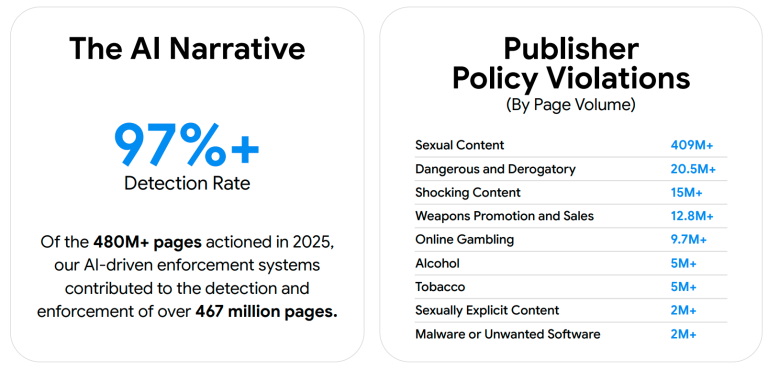
Google’s 2025 Ads Safety Report reveals how Gemini AI intercepted 99% of bad ads and reduced false account suspensions by 80%. Read the full scale of the defense.