
 Do Son
Texas AG Ken Paxton sues TP-Link, alleging the Wi-Fi giant's routers act as Trojan horses for CCP surveillance. State bans TP-Link gear for employees.
Cyber Security

Critical VS Code Live Server flaw CVE-2025-65717 (CVSS 9.1) lets attackers steal source code and credentials via malicious links. Protect your workspace now.

Point Wild reveals a new Remcos RAT variant abandoning local storage for real-time webcam streaming, memory evasion, and aggressive anti-forensics.

Splunk Enterprise Windows flaws (CVSS 7.7) CVE-2026-20143 & CVE-2026-20140 allow system takeover via DLL and Python search path hijacking. Patch immediately.
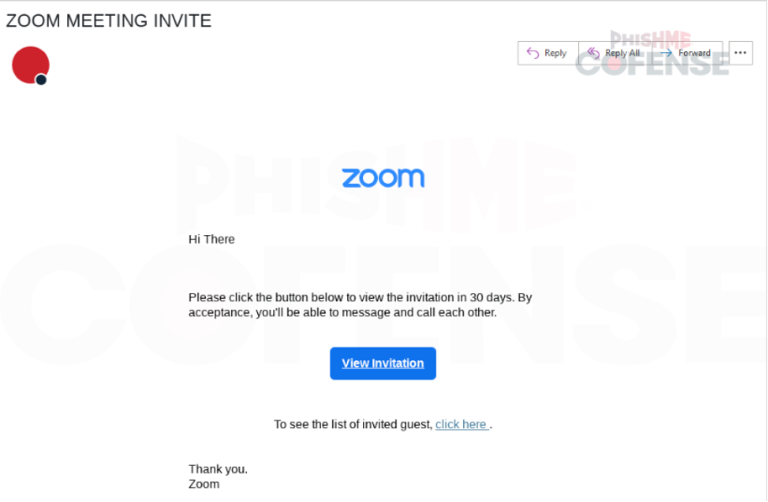
Cybercriminals are using fake DocuSign emails and the JWrapper framework to stealthily deploy SimpleHelp remote access tools. Learn how to spot the threat.

Critical Pterodactyl API flaw (CVE-2026-26016) allows cross-node authorization bypass. Attackers can destroy game servers. Update to version 1.12.1 now.

Google releases an urgent Chrome update to patch high-severity flaws in PDFium (CVE-2026-2648) and the V8 engine (CVE-2026-2649). Update to 145 now.
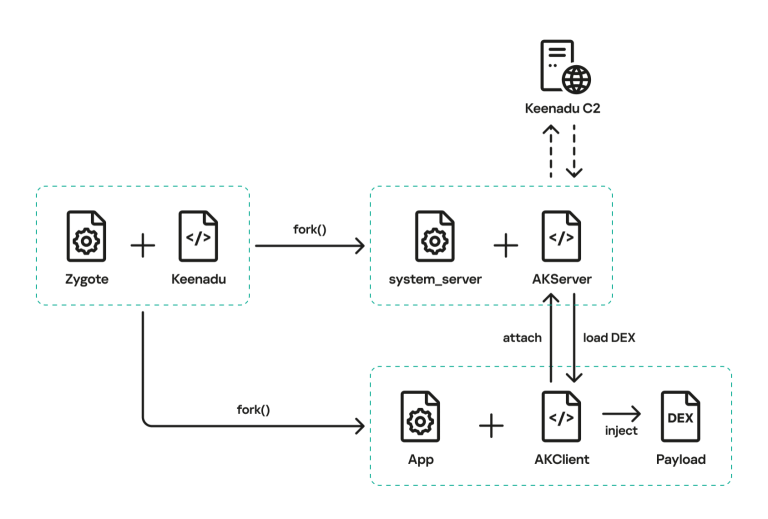
Kaspersky uncovers Keenadu, a firmware-level Android backdoor infecting the Zygote process. This pre-installed malware gives attackers full control.
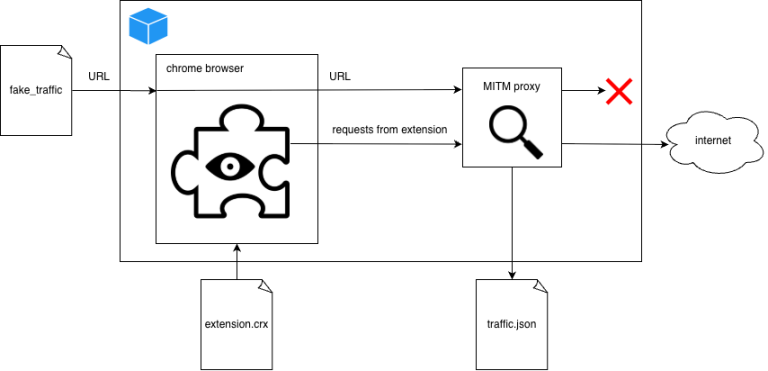
Q Continuum finds 287 Chrome extensions spying on 37M users. "Super PiP" & others exfiltrate history via Google Analytics. Check your browser now.
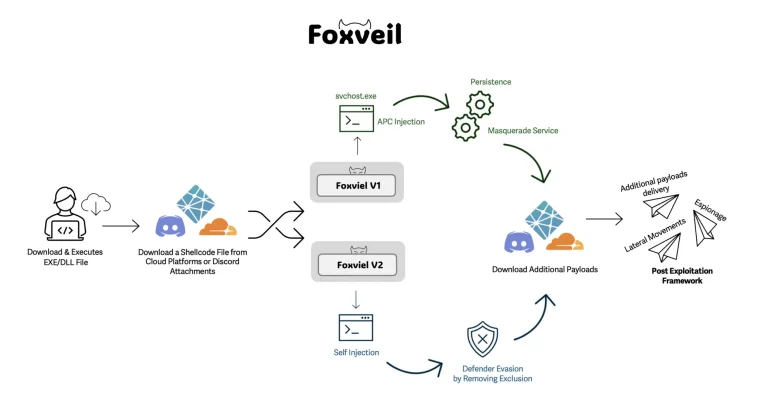
Cato CTRL discovers Foxveil, a new malware loader abusing Cloudflare, Netlify & Discord to bypass defenses. Active since Aug 2025. Learn the signs.
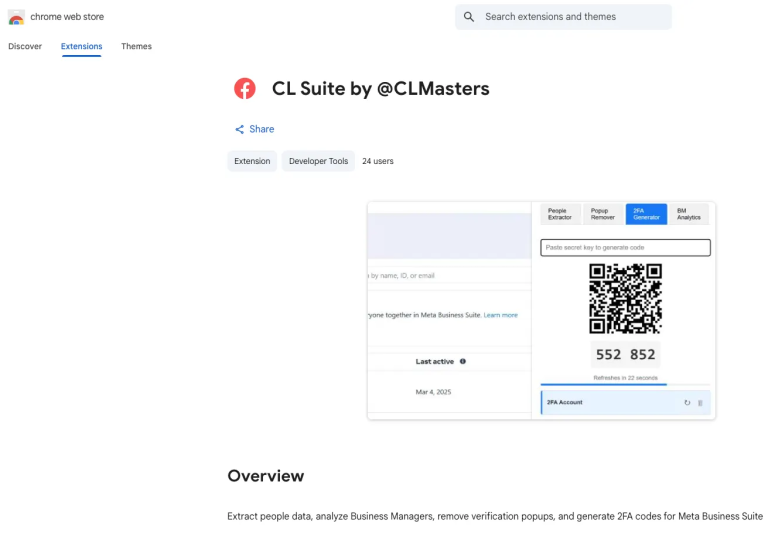
"CL Suite" Chrome extension steals Meta Business 2FA seeds & data. Attackers bypass security even after uninstall. Reset 2FA immediately.
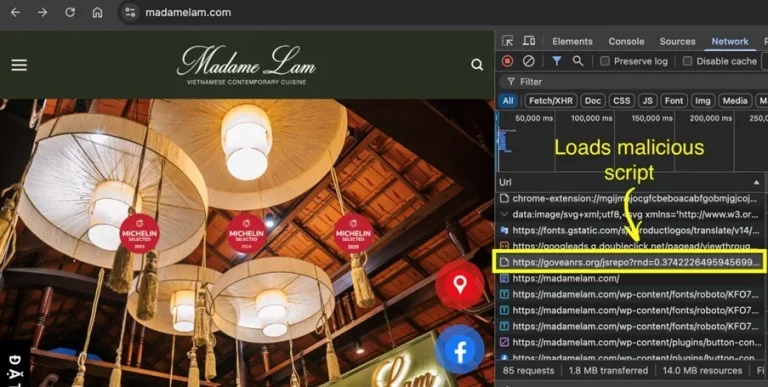
LevelBlue warns of StealC malware using "ClickFix" fake CAPTCHAs. Users are tricked into running fileless malware via PowerShell. Stay alert.

New Telegram phishing campaign abuses the "This is me" feature for account takeover. CYFIRMA reveals a global framework evading detection. Stay alert.

Ivanti patches critical EPM flaw CVE-2026-1603 allowing remote unauthenticated attackers to steal credentials. Update to 2024 SU5 immediately.

Warning: 7zip [.] com has been hijacked to spread residential proxy malware. Learn how to identify this 7-Zip impersonator and protect your system.

APT28 (Fancy Bear) weaponized CVE-2026-21509 in 24 hours to target NATO. New "BeardShell" and "NotDoor" malware steals emails. Patch Office now.

Microsoft warns of "CrashFix": malicious extensions crash browsers to trick users into running a "fix" that installs a RAT. Beware fake ad blockers.

Microsoft warns: Infostealers now target macOS & use WhatsApp worms. "Eternidade" & "Crystal PDF" steal credentials via cross-platform attacks.

Amaranth-Dragon (APT-41 nexus) weaponized WinRAR flaw CVE-2025-8088 in just 10 days. Southeast Asian govts targeted with malicious RAR archives.

TP-Link discloses command injection flaws in Archer BE230 routers (CVE-2026-0630). Authenticated attackers can gain root access. Update firmware now.
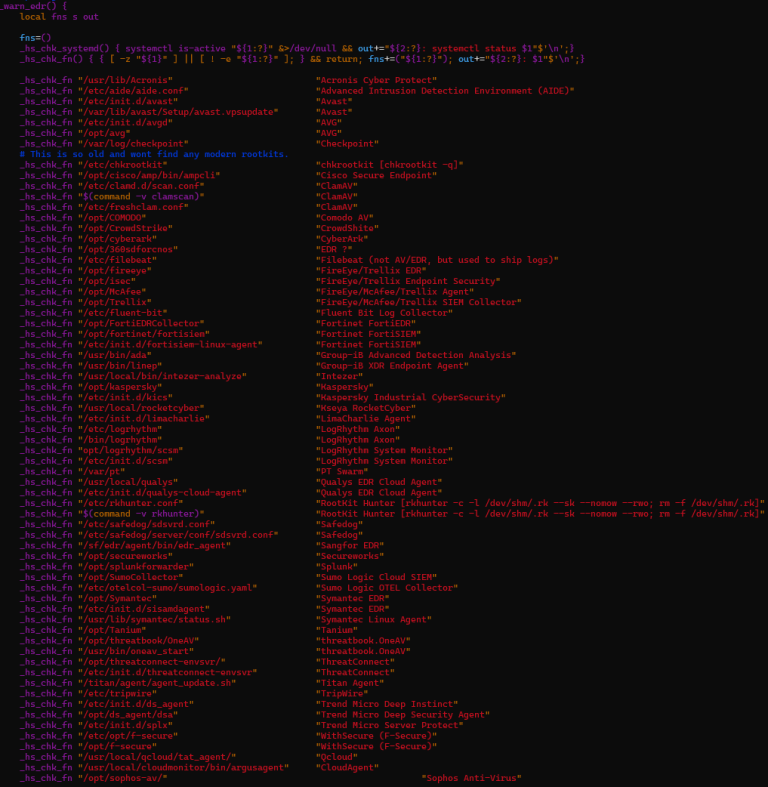
Cyble uncovers "ShadowHS," a fileless Linux malware weaponizing hackshell. It uses GSocket tunneling to evade firewalls and kill rival bots.
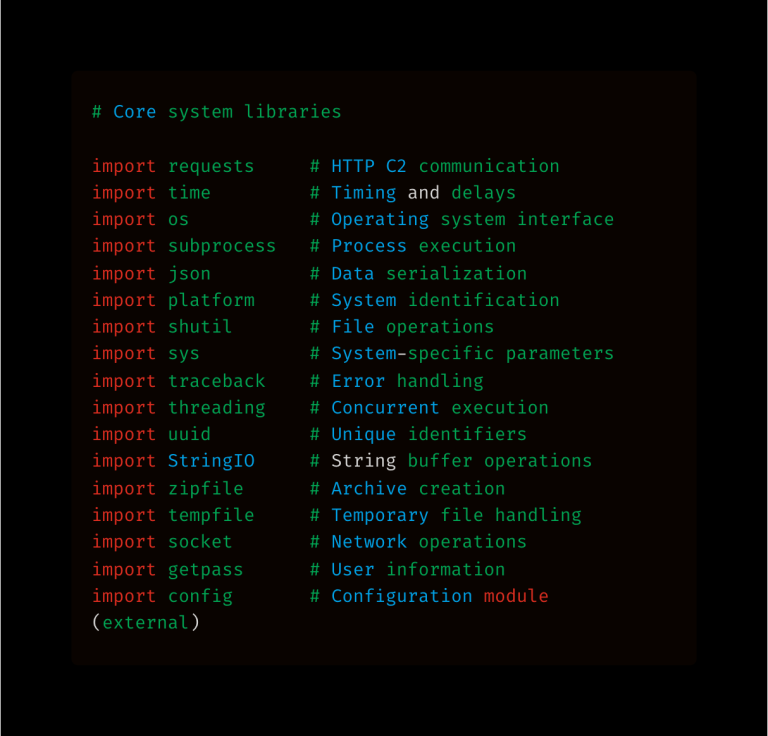
K7 Labs uncovers a stealthy Python-based RAT disguised as an ELF binary. Features adaptive beaconing and anti-forensics to stay hidden. Read the analysis.