 Do Son
FortiGuard Labs exposes a massive Silver Fox APT campaign targeting Taiwan. Hackers use tax-themed phishing and BYOVD attacks to deploy Winos 4.0 malware.
Cyber Security

Malwarebytes exposes a deceptive campaign using fake Windows 11 Facebook ads to trick users into downloading stealthy info-stealing malware.

GitLab reveals how North Korean fake IT workers use 'Contagious Interview' scams to bypass hiring, steal data, and hijack executive digital identities.

Critical prototype pollution flaw (CVE-2026-27212) in the Swiper npm package allows RCE, DoS, and auth bypass. Update to version 12.1.2 immediately.

Researchers extract LUKS decryption keys in plaintext from Moxa UC-1222A devices via a novel TPM bus sniffing attack (CVE-2026-0714). Secure your hardware.
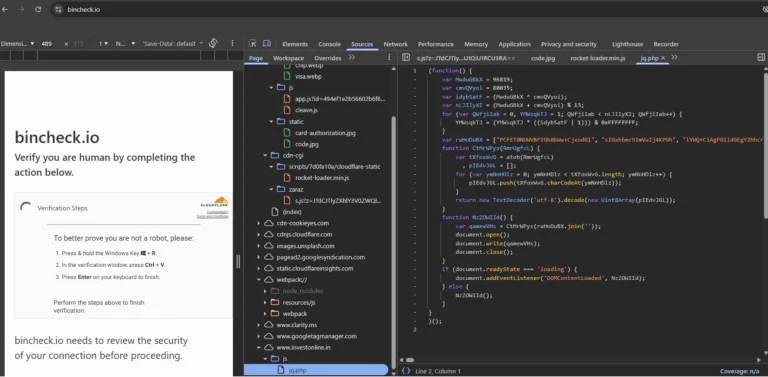
Elastic Security Labs uncovers a ClickFix campaign turning human helpfulness into a weapon. Fake verifications deploy the fileless MIMICRAT via PowerShell.

IceWarp urges immediate patching for critical flaws allowing unauthorized server access, XSS, and arbitrary file reading. Update your instances today.

Critical Undertow HTTP server flaw CVE-2025-12543 (CVSS 9.6) impacts HPE Telco Service Activator, allowing cache poisoning and session hijacking. Patch now.

Unit 42 warns of active attacks on critical BeyondTrust flaw CVE-2026-1731. Hackers bypass auth for RCE and data theft. Patch self-hosted instances now.

Critical path traversal flaws (CVE-2026-26065, CVE-2026-26064) in the Calibre e-book manager allow RCE via malicious PDB and ODT files. Update to 9.3.0.
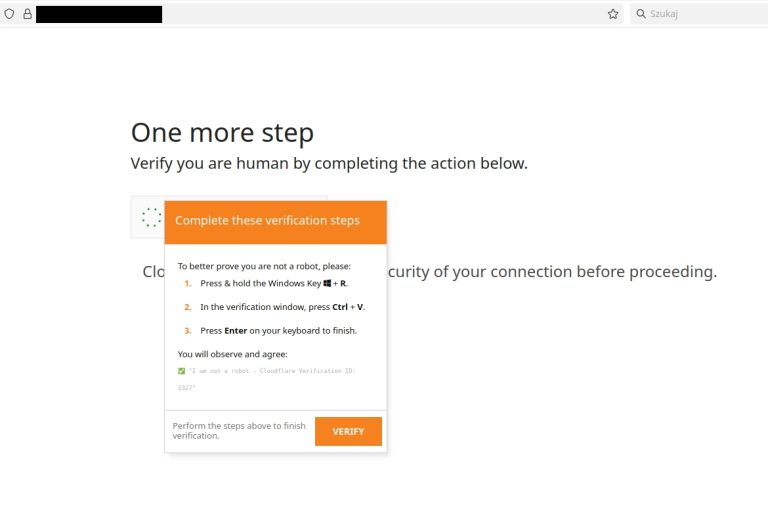
CERT Polska reveals how a fake "ClickFix" CAPTCHA campaign tricked users into deploying evasive Latrodectus and Supper malware. Protect your network now.
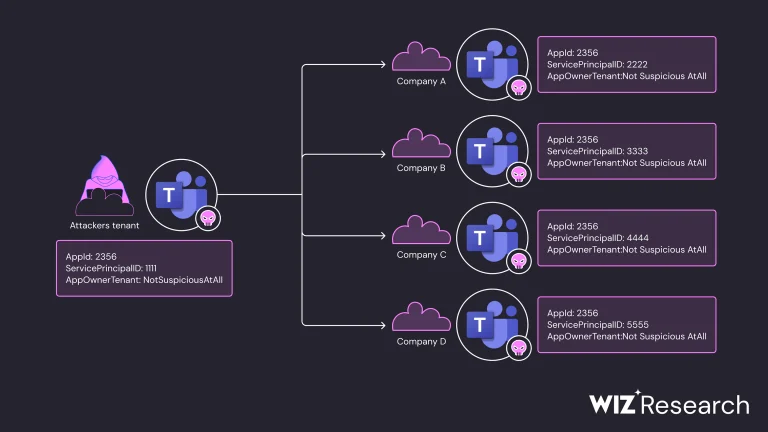
Wiz Research exposes a stealthy threat using malicious OAuth apps and Cyrillic homoglyphs to bypass Microsoft Entra ID security. Protect your cloud tenant.
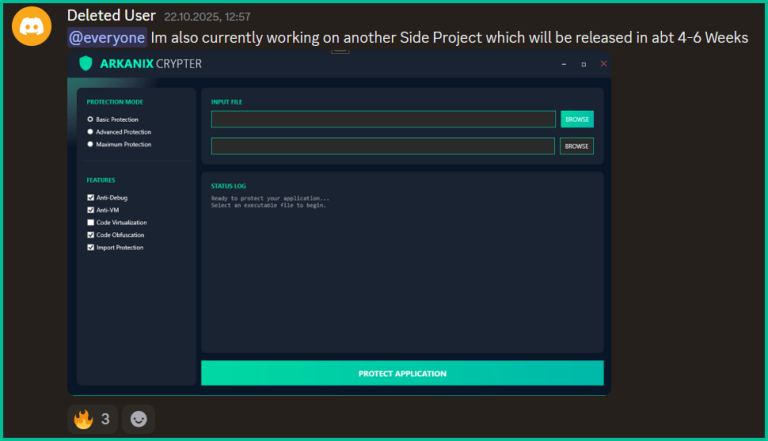
Kaspersky exposes Arkanix Stealer, a fast-moving MaaS operation leveraging Discord, tiered subscriptions, and AI-assisted development for quick data theft.
The FBI warns of a massive surge in ATM jackpotting attacks. Cybercriminals are using Ploutus malware to bypass the XFS layer and drain cash reserves.
Insikt Group exposes GrayCharlie compromising WordPress sites & US law firms. Attackers use "ClickFix" fake CAPTCHAs to deploy the NetSupport RAT.

A critical PDF Object Injection flaw (CVE-2026-25755) in jsPDF allows attackers to bypass AcroJS sandboxes. Update to version 4.2.0 immediately.
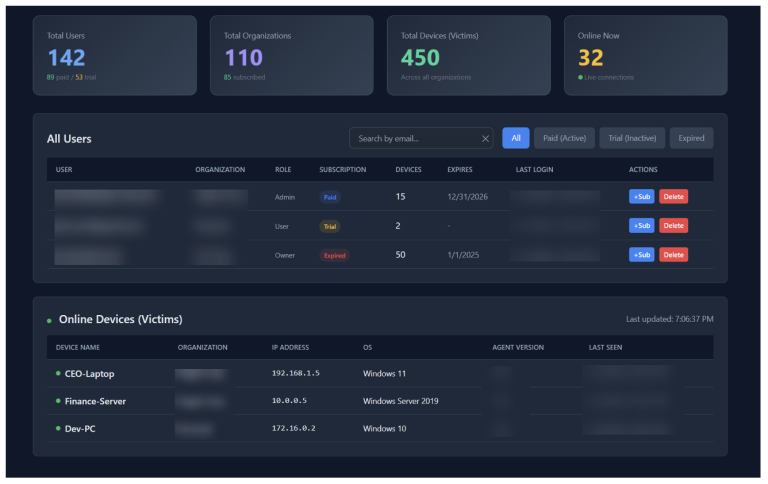
Proofpoint exposes TrustConnect, a new Malware-as-a-Service masquerading as an IT tool. The AI-assisted fake RMM software replaces dismantled threats.

A critical Windows Error Reporting flaw (CVE-2026-20817) allows local privilege escalation to SYSTEM. With the PoC publicly disclosed, update immediately.
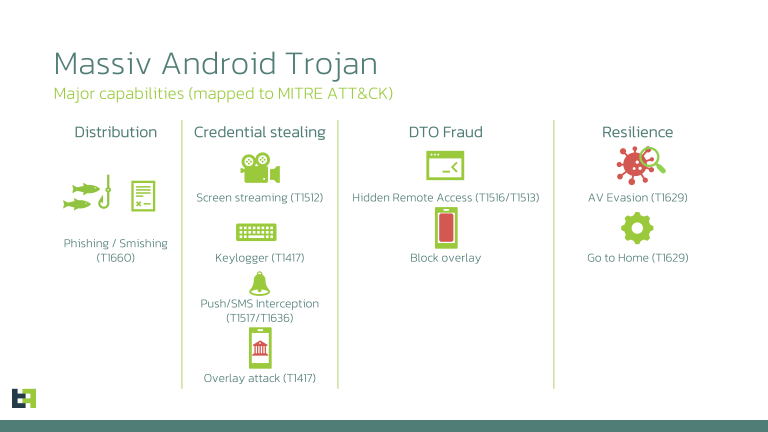
ThreatFabric exposes Massiv, a new Android banking Trojan hiding in fake IPTV apps. The malware uses accessibility permissions for full device takeover.

Ukrainian hacker Oleksandr Didenko receives a 60-month sentence for orchestrating a massive laptop farm scheme aiding North Korean IT operatives.

Apache Tomcat rolls out urgent updates for versions 9, 10, and 11 to fix legacy HTTP/0.9 protocol confusion and SNI certificate bypass flaws. Patch now.
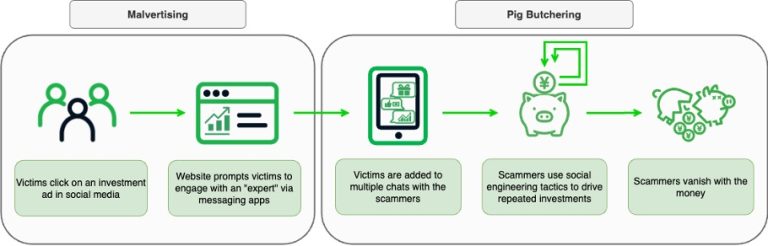
Infoblox Threat Intel exposes a highly scalable hybrid scam merging automated malvertising with "pig butchering" to drain global crypto investors' funds.