
 Do Son
HPE warns: Details of Aruba VIA root flaw (CVE-2025-37186) are public. Linux users exposed to LPE. No patch yet—apply the workaround now.
Cyber Security

Iran's nationwide internet blackout saw a brief 0.01% traffic surge from Tehran universities on Jan 9, 2026, signaling a new "whitelist" control strategy.

CVE-2026-21440: A critical 9.2 flaw in AdonisJS file uploads allows attackers to overwrite system files and gain RCE. Update to v10.1.2 immediately!

RustFS patches a critical 9.8 CVSS flaw (CVE-2025-68926) where a hardcoded gRPC token allows unauthenticated attackers to wipe storage data.

Apache StreamPipes patches CVE-2025-47411, a logic flaw allowing users to manipulate JWT tokens and hijack admin accounts. Update to v0.98.0 now!

OpenAI patches a new class of prompt injection in ChatGPT Atlas. See how the Agent mode is being hardened against hidden hijacks on the open web.

Jamf uncovers a new MacSync Stealer variant that was notarized by Apple, allowing it to bypass Gatekeeper and infect Macs without terminal commands.

n8n warns of a CVSS 10.0 RCE (CVE-2025-68613) in its expression system. Attackers can seize total server control. Upgrade to v1.122.0 immediately.

Gen Digital uncovers AuraStealer, a new infostealer using TikTok "Scam-Yourself" tactics to trick users into infecting their own Windows PCs.

CISA adds a CVSS 10 Cisco zero-day and SonicWall exploit chains to its KEV catalog, warning of active exploitation by Chinese APTs and supply chain attacks.

Researchers have uncovered a Russian-linked disinformation campaign targeting Moldova’s upcoming elections, attempting to undermine its pro-EU trajectory.
A massive 600GB data leak from China's Great Firewall exposes its internal workings, source code, and proof of its export to other countries.

The DOJ has charged Thalha Jubair, a UK national, for his role in the notorious Scattered Spider group's $115M cybercrime and extortion campaign.
Group-IB reports on MuddyWater, an Iranian APT, shifting tactics from RMM tools to custom malware and spearphishing, using new backdoors like Phoenix.

SolarWinds alerts on a Salesforce data breach impacting numerous companies. The breach exploited compromised OAuth tokens via the Salesloft Drift integration, exposing sensitive customer data.

A 26-year-old UK hacker, tied to the Yemen Cyber Army, has been sentenced to 20 months in prison for breaching thousands of websites and stealing data.

Russia has begun systematically blocking Cloudflare, throttling internet connections to 16KB after the initial download, impacting vast numbers of websites and other major hosting providers.

CISA adds 5 new exploited vulnerabilities to KEV, including flaws in ASUS routers, Craft CMS, and ConnectWise. Urgent patching required!

Meta's Q1 2025 report details the takedown of covert influence campaigns from China, Iran, and Romania, utilizing AI and fake accounts to manipulate public discourse.
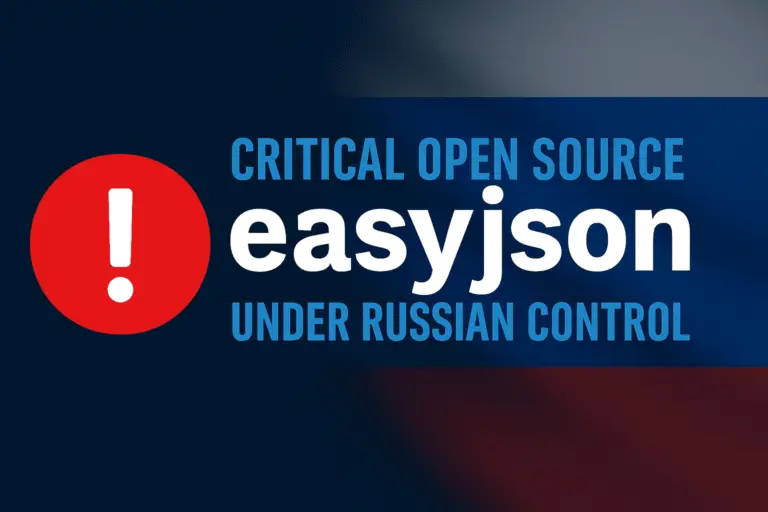
Research reveals the widely used open source library 'easyjson' is controlled by developers linked to Russia's VK Group, raising security concerns.

The UK's NCSC warns of a pervasive ransomware threat targeting all organizations. Learn key recommendations to enhance your cyber security and resilience.

NETSCOUT advisory reveals critical vulnerabilities in nGeniusONE, including hardcoded credentials & XSS. Update to version 6.4.0 b2350 or later immediately.