
 Do Son
DomainTools exposes North Korea’s "mature portfolio model": a compartmentalized cyber strategy designed for mission specialization and attribution resistance.
Cyber Security
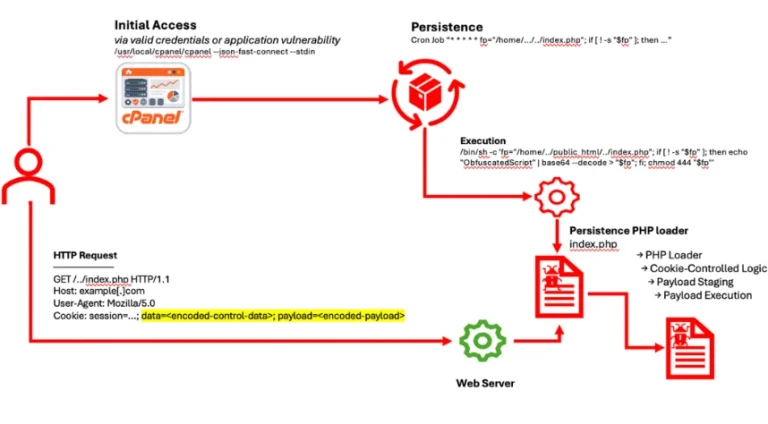
Microsoft Defender unmasks a stealthy PHP web shell hiding C2 logic in HTTP cookies. Learn how "cookie-gating" bypasses logs to maintain persistent RCE.
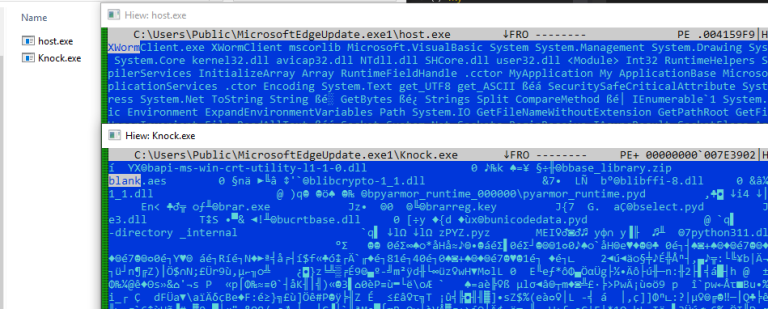
Splunk unmasks BlankGrabber: a modular Python info stealer using Discord and GitHub to swipe credentials and Discord tokens. Learn how to stay protected.
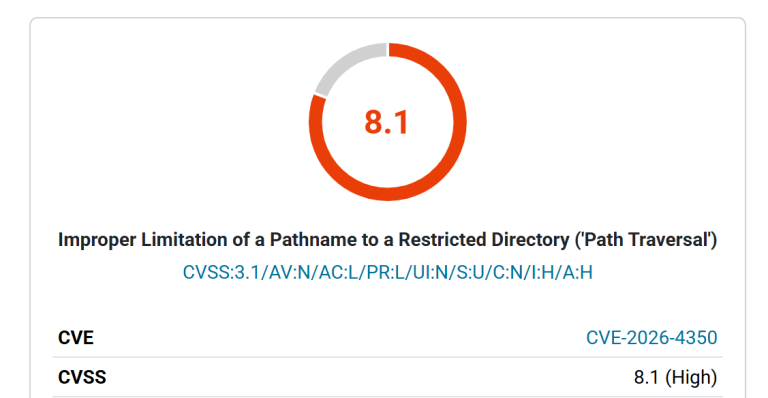
A critical 8.1 CVSS flaw in Perfmatters (200k+ installs) allows unauthenticated attackers to delete wp-config.php and hijack sites. Update to 2.6.0 now!

NCSC warns high-risk individuals of Russian and Chinese state actors hijacking WhatsApp and Signal. Protect your chats with these essential 2026 defense tips.

A critical flaw in IDrive for Windows (CVE-2026-1995) allows low-privilege users to seize SYSTEM control via weak folder permissions. Audit your PC today.
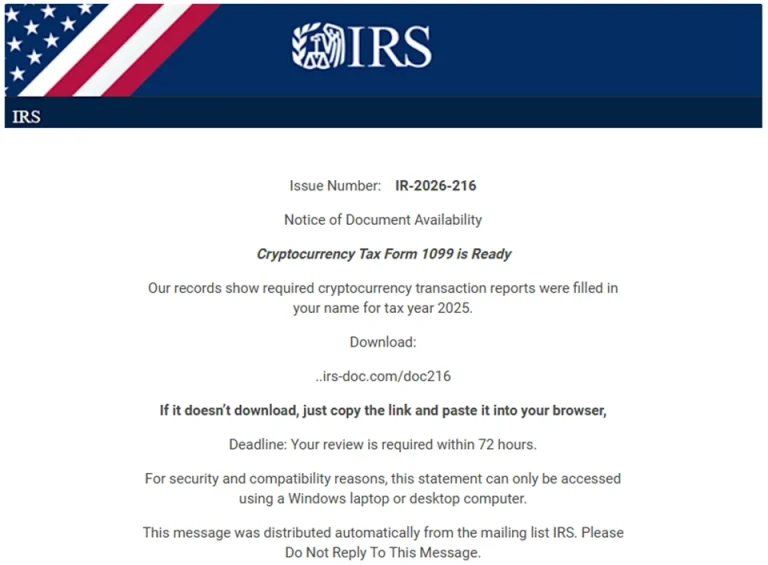
Microsoft warns of a surge in tax-themed phishing using PhaaS and ScreenConnect RATs to bypass MFA and hijack systems. Protect your W-2 data this season.
Russian national Aleksei Volkov was sentenced to 81 months in prison and ordered to pay $9.1M for his role as an access broker in major U.S. ransomware attacks.

Checkmarx warns of a supply chain breach on the OpenVSX registry and KICS GitHub Action. Malicious plugins were active briefly on March 23. Update now.
After a developer hit an $82k debt in 48 hours, Google AI Studio has added spending limits. Learn how to set your fiscal guardrails and protect your account.
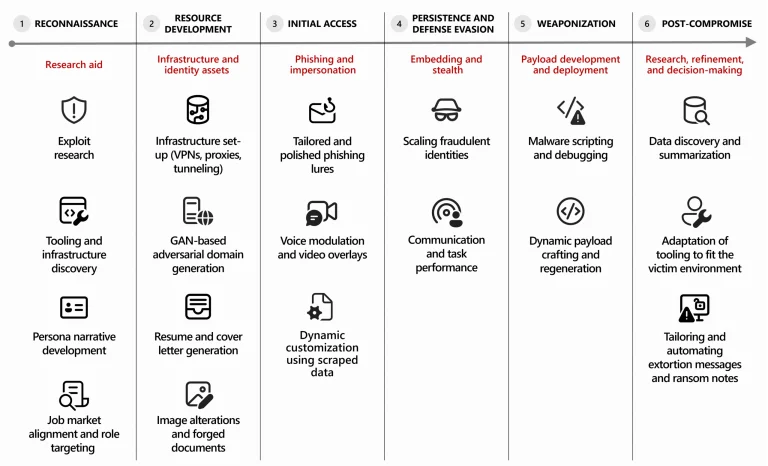
Microsoft Threat Intelligence reveals how cybercriminals and North Korean APTs are weaponizing generative AI to scale attacks and poison AI assistants.
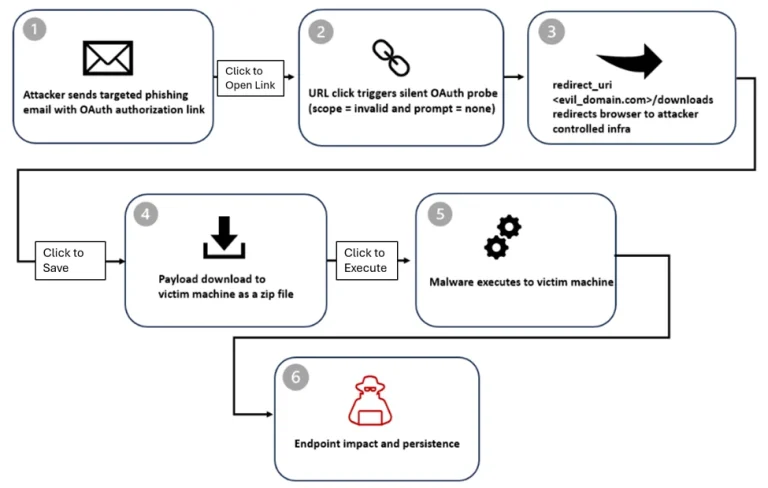
Microsoft Defender reveals a new phishing campaign abusing OAuth redirect URIs to bypass security and deliver stealthy malware to your system.


Windows kernel vulnerability CVE-2026-21241 (afd.sys) exposed! A new PoC exploit shows how local attackers can win a race condition to gain SYSTEM privileges.
ASUSTOR patches a critical 9.2 severity flaw (CVE-2026-3179) and a MitM vulnerability in ADM's FTP Backup. Update to version 5.1.2.REO1 now to secure your data.
Genians report reveals MuddyWater APT's shift to Rust-based malware and RMM tool abuse for long-term espionage across government and critical infrastructure.

Zyxel issues urgent patches for a critical 9.8 severity flaw (CVE-2025-13942) in UPnP functions that allows remote attackers to execute OS commands. Patch now!

SolarWinds patches four critical 9.1 CVSS RCE vulnerabilities in Serv-U. Attackers can create admin users and execute code as root. Update to 15.5.4 now!

Researcher @goyaramen exposes "ARXON," an AI-automated pipeline using LLMs to manage simultaneous global attacks on Fortinet devices. The future of scale is here.

Google releases Chrome v145.0.7632.116 to patch high-severity flaws in Media, DevTools, and the Tint graphics engine. Update now to prevent memory leaks.

Group-IB exposes Operation Olalampo: MuddyWater's new MENA campaign using AI-assisted Rust malware (CHAR) and Telegram bots for stealthy C2 communication.

CISA warns of critical flaws in EOL USR-W610 IoT servers. CVE-2026-25715 allows full admin control via blank passwords. No patches planned; isolate now.