 Do Son
TL;DR On September 22, 2026, cPanel published security advisories addressing three security flaws across its hosting platform....
cybersecurity
TL;DR Security researchers published a technical breakdown of a critical Fluent Bit vulnerability tracked as CVE-2026-61674 on...
TL;DR GitHub released security updates addressing several GitHub Enterprise Server vulnerabilities. These critical flaws could permit remote...
TL;DR On September 23, 2026, developers launched a GitLab critical patch release fixing 11 security flaws. The...
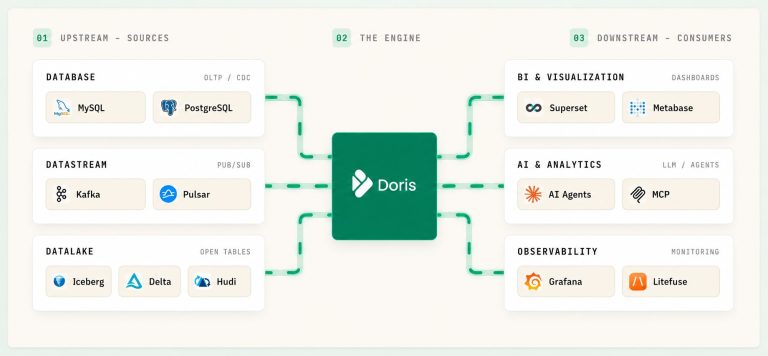
TL;DR The Apache Software Foundation addressed two security flaws in its real-time analytics database. These Apache Doris...
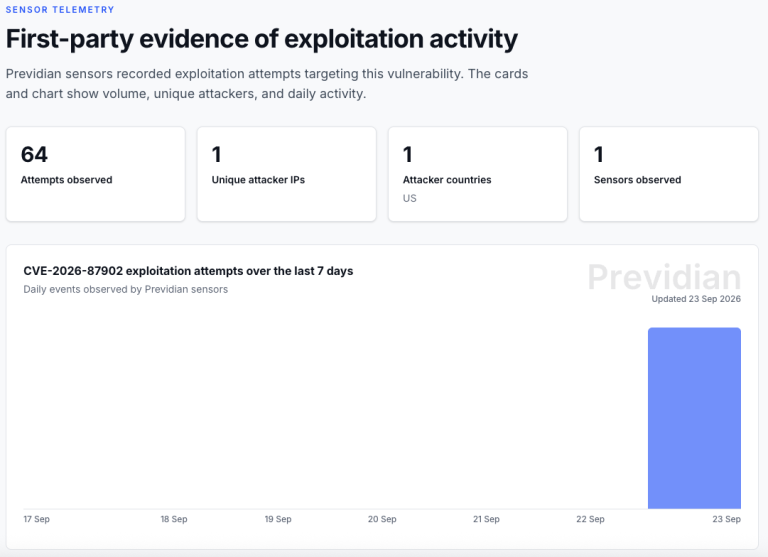
TL;DR On September 22, 2026, WordPress addressed a critical security flaw tracked as CVE-2026-87902. Security researchers confirmed...
TL;DR Zoho Corporation patched six critical ManageEngine security vulnerabilities across its network monitoring portfolio. These severe flaws...
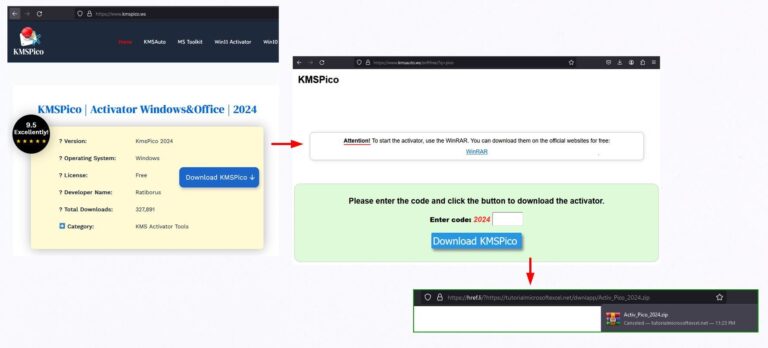
At a Glance Attribute Details Malware Family Vidar information stealer Threat Actor Unknown financially motivated cybercriminals Target...

TL;DR On September 21, 2026, security researcher Rafie Muhammad published technical analysis of a high-severity flaw in...
At a Glance Attribute Details Malware Family sckit Go binary Threat Actor Unknown Target Victims AI developers...
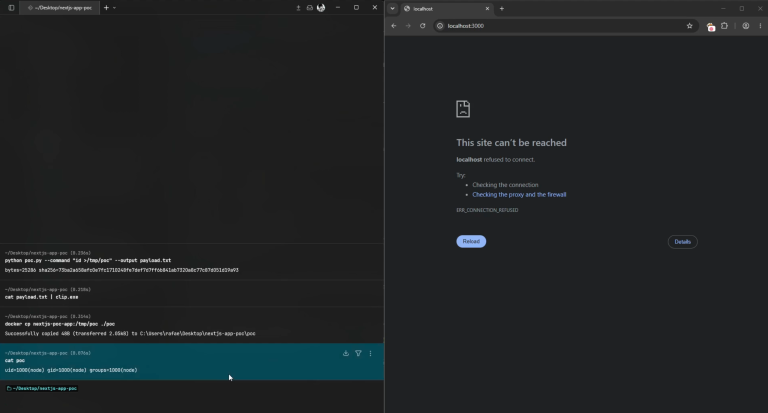
TL;DR On September 22, 2026, Vercel published an emergency fix for a critical Next.js RCE vulnerability. Tracked...
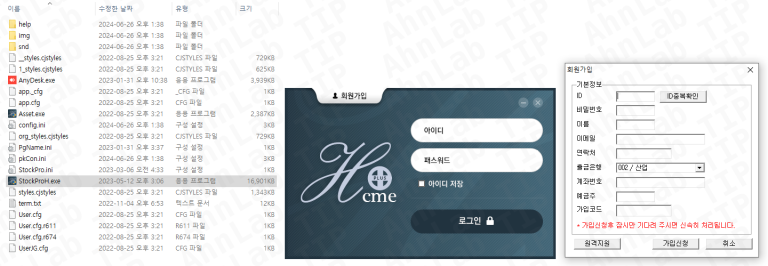
At a Glance Malware Family: KRSID ransomware, Quasar RAT (historical). Threat Actor: Suspected investment fraud groups (Telegram:...
TL;DR On September 23, 2026, IBM published a security bulletin addressing 47 vulnerabilities in Financial Transaction Manager....
TL;DR IBM disclosed 22 security flaws affecting DataStage on Cloud Pak for Data. The most severe IBM...
TL;DR Google recently rolled out Chrome 154 to the stable channel for Windows, Mac, and Linux users....
TL;DR On September 22, 2026, SolarWinds released software updates to resolve critical security flaws. These SolarWinds Observability...
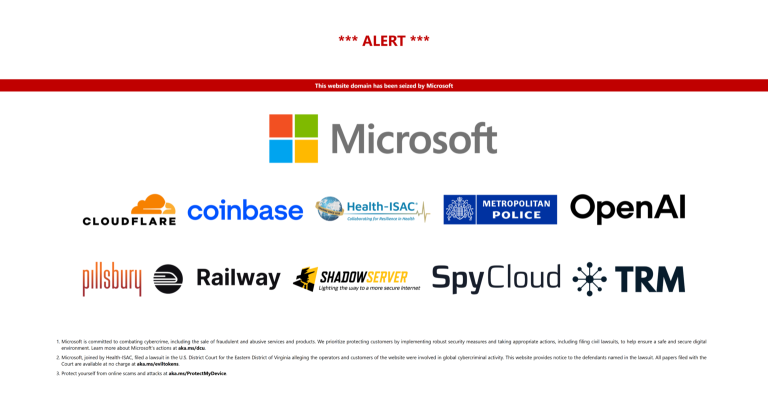
At a Glance Attribute Details Actor or Group Storm-2992 and associated cybercrime subscribers Activity Type Phishing-as-a-Service, device...
TL;DR On September 22, 2026, F5 disclosed a critical flaw in its Access Policy Manager software. This...
TL;DR Zoho Corporation patched a critical ManageEngine ADSelfService Plus vulnerability affecting the GINA client. This flaw allows...
TL;DR Security teams observed active attacks against an unpatched flaw in enterprise gateways. This critical Check Point...
TL;DR WordPress recently released version 7.1.2 to address a critical path traversal flaw. This WordPress RCE vulnerability...
TL;DR Check Point warned of an actively exploited Check Point Management vulnerability. Attackers use CVE-2026-93616 to run...