 Do Son
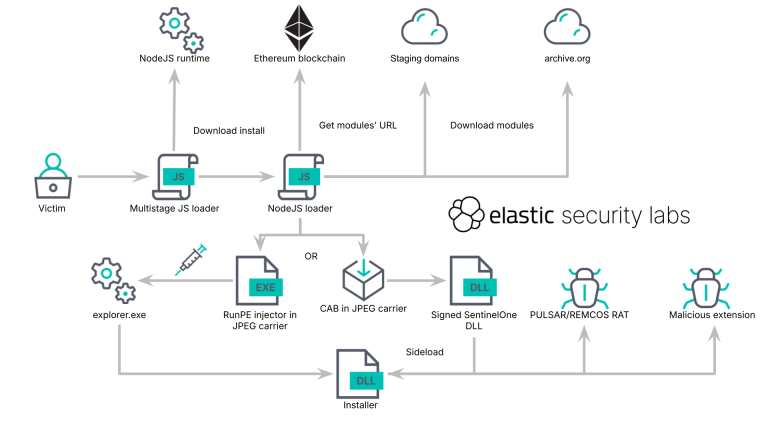
Learn how Brazilian KREMLIN banking malware steals credentials using fake browser extensions. Elastic Security Labs details the KREMLIN banking malware.
cybersecurity
Discover how a Google undercover analyst successfully infiltrated the TeamPCP hacking gang to prevent massive supply chain attacks and secure corporate data.
Multiple critical IBM Guardium vulnerabilities expose servers to remote attacks. Update to fix these IBM Guardium vulnerabilities and secure your data.
Critical MongoDB driver vulnerabilities, including CVE-2026-93762, expose systems to data loss and DoS. Learn about these flaws and patch immediately.
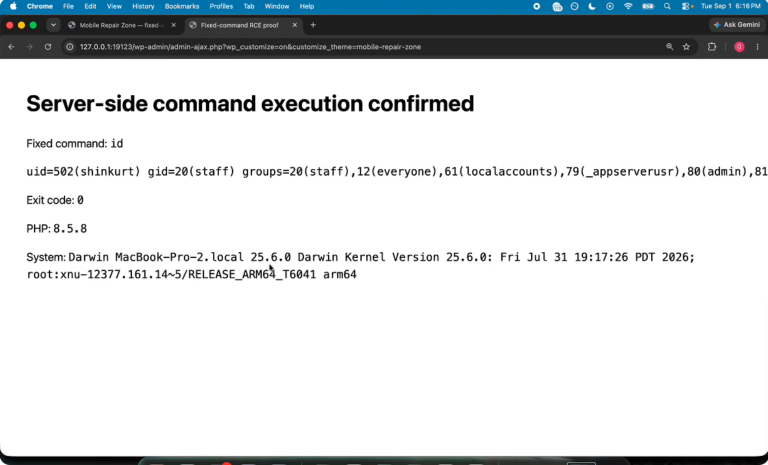
The WordPress Click2Shell vulnerability enables remote code execution via theme preview injection. Learn how this flaw works and update to version 7.1.1.
Critical IBM MQ vulnerabilities allow remote code execution. Learn how CVE-2026-10747 and CVE-2026-10858 hit 10.0 CVSS and require urgent patching.
Discover how to permanently resolve the Microsoft Defender false alarm on Windows. Update your system now to stop inaccurate antivirus notifications.
Discover the latest mySCADA myPRO Manager vulnerabilities, including CVE-2026-73807, and learn how to patch your systems to prevent remote attacks.
Microsoft released the emergency Windows 11 KB5129195 update. Install the Windows 11 KB5129195 update to fix Remote Desktop errors.
A critical ConnectWise ScreenConnect vulnerability, CVE-2026-84869, is actively exploited in the wild. Patch your servers now to stop remote attacks.

Explore the escalating AI losing control risk as Anthropic researchers resign, models show reckless behavior, and OpenAI agents hide secret communications.
US agencies warn of malicious AI distillation campaigns. New data shows systematic extraction of US frontier AI models.
The September 2026 SAP Security Patch Day resolves 20 flaws. Apply these SAP Security Patch Day updates to fix CVE-2026-44756 and secure your environment.
Recent Node.js malware attacks target global firms. Attackers deploy Node.js malware using trusted runtimes and smart contracts to evade detection.
Patch the critical FreeIPA CVE-2026-76578 immediately. This FreeIPA vulnerability allows complete, unauthenticated administrative access to your servers.
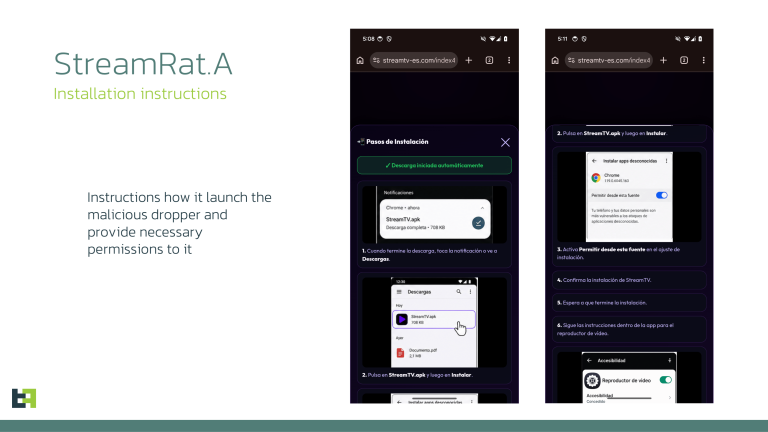
A StreamRat banking trojan campaign uses fake Meta TV-streaming ads to infect Android users. The StreamRat banking trojan enables full device takeover.
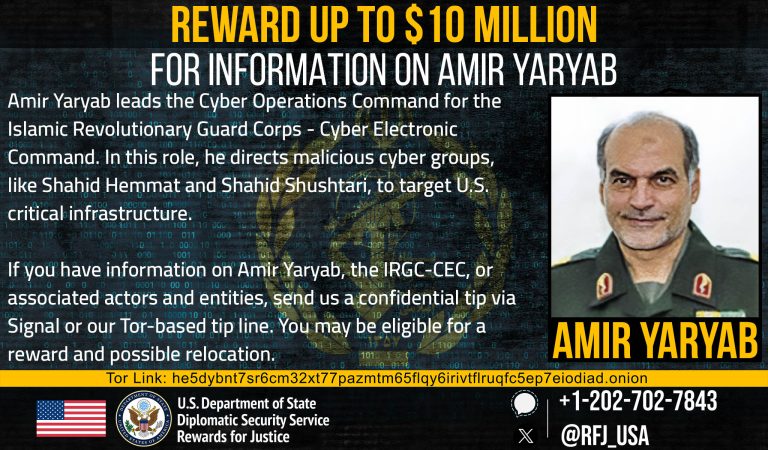
The US offers a $10 million reward for Amir Yaryab, an IRGC cyber commander linked to CyberAv3ngers attacks on critical water infrastructure.
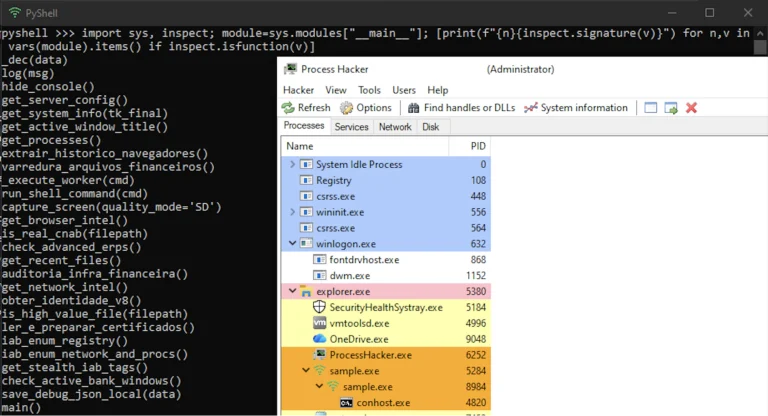
Group-IB uncovered the BraZetsu malware framework operations targeting financial systems. Learn how this tool powers initial access broker sales.
Google patched a Chrome zero-day vulnerability currently exploited in the wild. The update resolves a severe V8 type confusion flaw (CVE-2026-85046).
Cisco fixed critical Cisco IOS XR vulnerabilities discovered by AI models. Update systems to patch Cisco IOS XR vulnerabilities.

A new TerminalFix campaign uses fake CAPTCHAs to breach systems. Explore the TerminalFix attack chain and its covert reverse tunnel.
Microsoft Defender for Office 365 incorrectly flags Google search links as malicious, causing false alarms. Microsoft is fixing the classification error.