 Do Son
Threat actors abuse Node.js in malvertising campaigns to steal data and deliver malware via fake crypto installers and stealthy PowerShell scripts.
cybersecurity

Malvertising campaign targets Onfido users via deceptive Google ads, using Evilginx to steal credentials.

New attack campaign uses Microsoft Teams phishing and a novel TypeLib COM hijacking technique for persistence, targeting finance sector.

APT29, a Russia-linked group, targets European diplomats with phishing emails disguised as wine tasting invitations, deploying GRAPELOADER malware

CISA issues urgent alert on actively exploited SonicWall SMA100 vulnerability (CVE-2021-20035). Federal agencies must mitigate by May 7, 2025

Unprotected APIs exposed sensitive data of over 33,000 employees. CloudSEK's BeVigil discovered the security flaw

CrazyHunter ransomware group targets Taiwan's critical infrastructure with sophisticated attacks, using BYOVD techniques and open-source tools.

The CVE Foundation launches to ensure the future of the CVE Program after U.S. government funding ends for MITRE's operation.
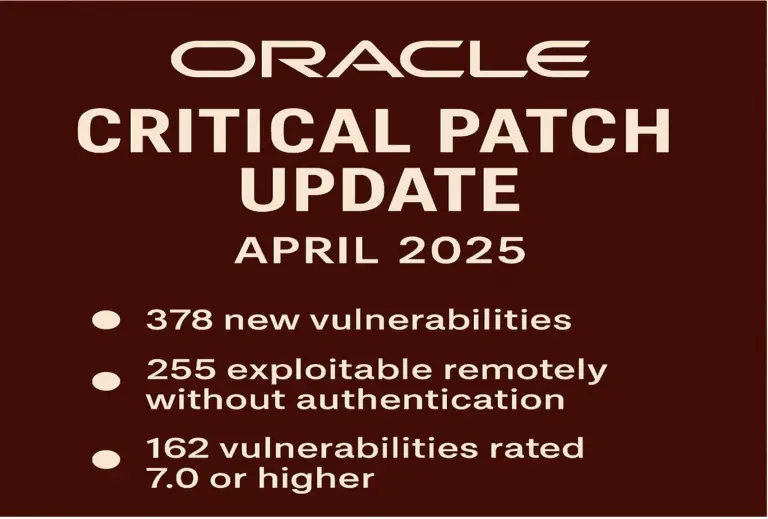
Oracle's April 2025 CPU delivers 378 security patches across its product suite. Learn about critical vulnerabilities and the urgent call to update.

A curated list of the top cybersecurity tools for 2025, covering reconnaissance, wireless hacking, password cracking, forensics, and more.

Google Chrome 135 fixes critical CVE-2025-3619 and high CVE-2025-3620 flaws. Users urged to update now to avoid potential code execution threats.

Discover Waiting Thread Hijacking, a novel process injection technique that bypasses EDR systems. Learn how it stealthily executes code in remote processes.

Discover how Windows 11 vulnerabilities CVE-2025-24076 and CVE-2025-24994 allow unprivileged users to gain system privileges via DLL hijacking.
A new campaign by Chinese threat actor UNC5174 uses the VShell RAT. Sysdig TRT reports on the group's shift to open-source tools and evasion tactics.

Kandji's research uncovers PasivRobber, a sophisticated macOS malware suite targeting user data. Learn about its deceptive tactics and capabilities.

A malicious npm package, disguised as an Advcash integration, contains a reverse shell that triggers after successful payments, granting attackers server access.

CloudSEK's report reveals how fake PDF converters use social engineering to spread malware. Learn how these malicious sites deceive users and steal data

NVISO's report details BRICKSTORM, a China-linked backdoor targeting European industries, using sophisticated techniques to evade detection

Learn about ResolverRAT, a new remote access trojan using advanced evasion to avoid detection. This malware employs sophisticated techniques.

PyPI resolved a security issue on April 14, 2025, where users retained team privileges after organization removal. The swift 2-hour fix prevented potential escalation.

A Forescout report reveals critical vulnerabilities in solar power systems that could be exploited to destabilize power grids and compromise user data.

A China-nexus APT group exploited Ivanti Connect Secure VPN vulnerabilities to infiltrate organizations globally, deploying the SPAWNCHIMERA malware toolkit