
 Do Son
Invariant Labs reveals a critical vulnerability in the Model Context Protocol (MCP) enabling Tool Poisoning Attacks. Learn how this threat can lead to data exfiltration and AI hijacking
cybersecurity

Google introduces Unified Security, powered by Gemini AI, to streamline enterprise cybersecurity. Discover new AI security agents, enhanced threat detection, and data protection tools for comprehensive security management.
CISA has added critical vulnerabilities affecting Windows CLFS (CVE-2025-29824) and Gladinet CentreStack (CVE-2025-30406) to its Known Exploited Vulnerabilities Catalog. Learn about the threats and the urgent need to apply patches.Sources and related content

Microsoft reports active exploitation of a Windows CLFS zero-day (CVE-2025-29824) to escalate privileges and deploy ransomware. Learn about the attacks, the threat actors involved, and how to mitigate the risk.
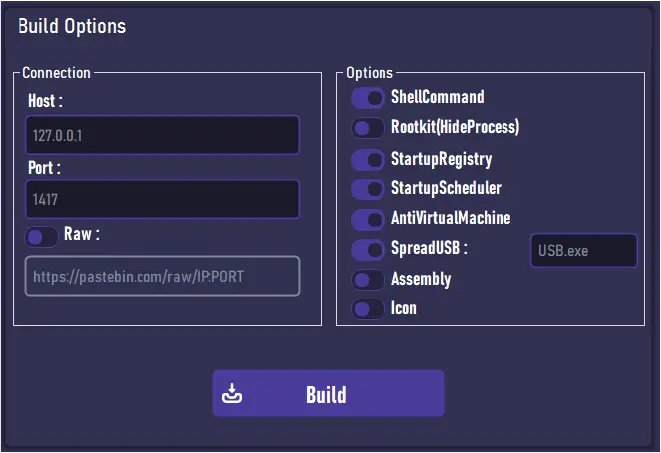
CYFIRMA researchers discovered Neptune RAT, an advanced Remote Access Trojan targeting Windows. Learn about its destructive features, evasion techniques, and distribution methods.

Attackers are using "Rogue RDP" techniques, abusing RemoteApp and resource redirection to steal files and conduct espionage

Microsoft's April 2025 Patch Tuesday addresses 134 vulnerabilities, including a zero-day under active exploitation. This update covers critical RCE flaws in Windows, Office, and more

Vidar Stealer malware is distributed by masquerading as BGInfo.exe, exploiting expired signatures and file discrepancies to evade detection

The Grandoreiro banking trojan is being spread through phishing campaigns. Learn about the attack methods and how to stay safe.

A security flaw in Apache's mod_auth_openidc module can expose protected web content to unauthenticated users. Patch or mitigate to secure your server

Siemens security advisories detail a critical authentication vulnerability (CVE-2024-54092) in Industrial Edge Devices, allowing for potential impersonation

Learn about the recent cybersecurity incident at the U.S. Department of the Treasury and the steps taken to address the breach.

Unlocking the power of large language models (LLMs) in offensive cybersecurity. Learn how researchers achieved a record-breaking 95% performance on InterCode-CTF benchmark using simple agent designs.

Introducing reNgine: The ultimate web app reconnaissance suite. Enhance your security assessment with advanced tools and uncover vulnerabilities like never before.

Learn about the cybersecurity incident at Artivion, a renowned manufacturer of cardiovascular surgical devices, and how they are responding to the breach.

Learn about the cybersecurity incident that led to the closure of DMM Bitcoin, a Japanese cryptocurrency exchange. Find out more about the unauthorized transfer of millions of dollars worth of Bitcoins.

Discover the alarming cybersecurity concerns at drinking water systems in the US. Find out how vulnerabilities could be exploited and what measures need to be taken for protection.

Discover how China's Regulation on the Management of Network Product Security Vulnerabilities shapes its cybersecurity landscape.

Understand the cybersecurity concerns surrounding macOS Sequoia. Find out how changes to the network architecture have impacted security vendors and users.

Discover the growing threat of cybercriminals exploiting Extended Validation code signing certificates to deceive users and bypass security measures.

Get insights into the ECB's cybersecurity stress test of European banks. Learn how financial institutions fared in terms of their preparedness for cyber incidents.

Discover the latest cybersecurity trends affecting SMBs. Find out about the surge in malware infections and the favored tactics used by cybercriminals.