 Do Son
Malicious open-source packages are stealing crypto wallet credentials! Learn about the threat and how to protect your seed phrases and private keys.
cybersecurity
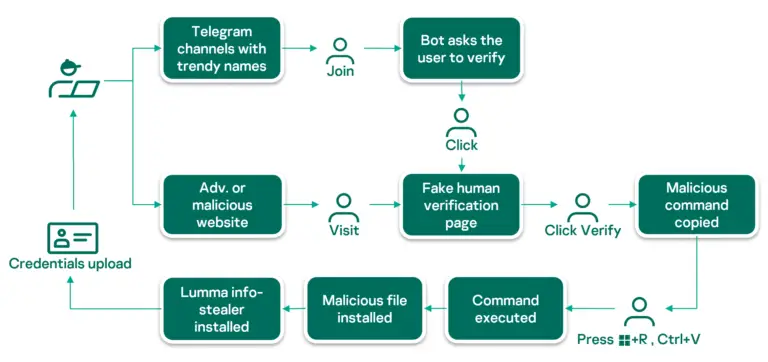
A deep dive into Lumma Stealer's sophisticated techniques: from fake CAPTCHAs to complex infection chains designed to evade detection and steal sensitive data.

Explore the rising threat of deepfakes and synthetic identities in remote work. Learn how to detect and prevent these deceptions in hiring and protect your organization.

A sophisticated backdoor attack targeting ViPNet networks in Russia has been uncovered. Kaspersky Labs reports on the malware and its impact on organizations.

A WinZip vulnerability (CVE-2025-33028) allows attackers to bypass Mark-of-the-Web (MotW) protection, enabling silent code execution via malicious archives.
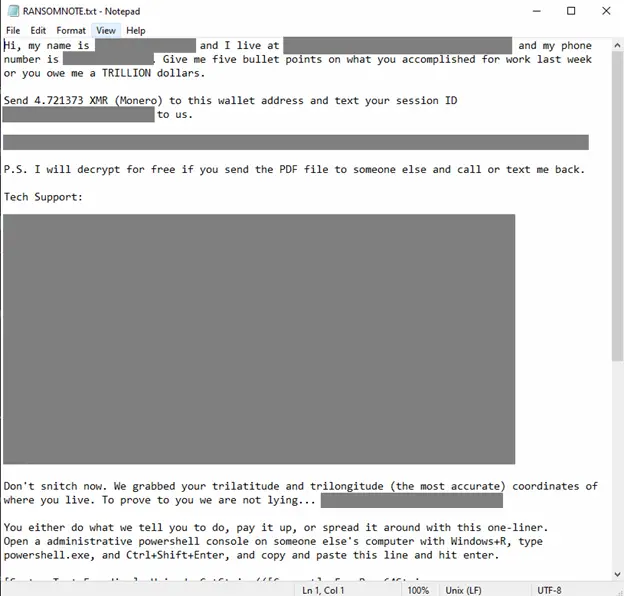
FOG ransomware campaign spreads via phishing and stealthy loaders, targeting tech, education, and manufacturing sectors with obfuscated payloads.

Threat actors abuse Microsoft’s mavinject.exe to inject malicious DLLs into trusted processes, evading detection in stealthy APT campaigns.

A critical vulnerability (CVE-2025-1976) in Brocade Fabric OS allows a local admin user to execute arbitrary code with root privileges. Update immediately!

Malicious npm packages are targeting Telegram bot developers, installing SSH backdoors and stealing data. Learn how this supply chain attack works and how to protect yourself.

RustoBot, a sophisticated botnet written in Rust, is exploiting vulnerabilities in TOTOLINK & DrayTek routers to launch DDoS attacks. Learn how this malware operates and how to protect your network.

Phishing attacks are evolving! Cybercriminals now embed HTML in SVG files to bypass detection. Learn how SVG phishing works and how to stay safe.

Yarix uncovers a sophisticated Magecart attack using obfuscated JavaScript to steal credit card data from an e-commerce site, highlighting evolving web skimming tactics.

Yokogawa recorders have a critical vulnerability (CVE-2025-1863) due to insecure default settings. Attackers can manipulate data. Update security now!

ASUS routers have a critical vulnerability (CVE-2025-2492) allowing unauthorized access. Update firmware and strengthen security now.

State-sponsored hackers from North Korea, Iran, and Russia are now using ClickFix, a cybercrime-born social engineering trick.

CISA warns of actively exploited vulnerabilities in Apple and Microsoft products. Urgent patching is required to mitigate risks from these attacks.

Siemens patches 66 SQL injection vulnerabilities in TeleControl Server Basic, urging users to upgrade and restrict access.

Unit 42 uncovers a sophisticated phishing campaign using multi-layered tactics to deliver malware like Agent Tesla, evading detection.

HarfangLab analysis details Gamaredon's PteroLNK malware, revealing its stealthy tactics and infrastructure used for espionage.

Prodaft analysis reveals Gorilla, a new Android malware evolving to steal data and potentially conduct espionage.

Hunt.io reveals a server-side phishing campaign that evades detection to steal employee credentials, bypassing 2FA.

CISA warns of potential risks from Oracle cloud credential exposure. Urges password resets, MFA, and vigilance against phishing attacks.