
 Do Son
DieNet, a new hacktivist group, is leveraging DDoS-as-a-service for rapid-fire attacks on critical infrastructure. NETSCOUT reports on their tactics and targets.
cybersecurity

SonicWall urges urgent updates to SMA 100 Series devices after critical post-auth vulnerabilities expose systems to file deletion and command injection.

A zero-day privilege escalation vulnerability (CVE-2025-29824) in Microsoft CLFS was exploited by Balloonfly (Play ransomware) before the official patch.

CYFIRMA's analysis details Gunra Ransomware's sophisticated techniques, including evasion and data exfiltration, impacting global industries.

A critical vulnerability (CVE-2025-2605) in Honeywell MB-Secure alarm panels allows attackers to execute OS commands. Update to the latest version now.

IBM patches CVE-2024-51466 and CVE-2024-40695 in Cognos Analytics to prevent system compromise, sensitive data leaks, and remote code execution.

MediaTek’s May 2025 bulletin reveals high-severity modem flaw CVE-2025-20666 & Android bugs risking denial of service & local privilege escalation

A critical vulnerability (CVE-2025-2774) in Webmin allows remote attackers to escalate privileges and execute code as root. Update to version 2.302 now.
Cisco Talos reports on AiTM attacks that bypass MFA by using reverse proxies to steal credentials and session cookies, leading to account takeover.

CVE-2025-47154 (CVSS 9.0) is a use-after-free flaw in the Ladybird browser engine that attackers can exploit. Update to the fixed build now.

Sophos researchers detail a complex campaign using Cobalt Strike, DLL sideloading, and clever techniques like expired certificates

4Chan is back online after a data breach blamed on outdated software and underfunding. The forum seeks volunteers for support.
Citizen Lab reveals a malware campaign targeting Uyghur exiles by hijacking trusted language software, exposing new digital transnational repression tactics.
Quick Agent vulnerabilities could let attackers execute code or steal files from Ricoh MFPs. Update now to secure systems from critical remote attacks.
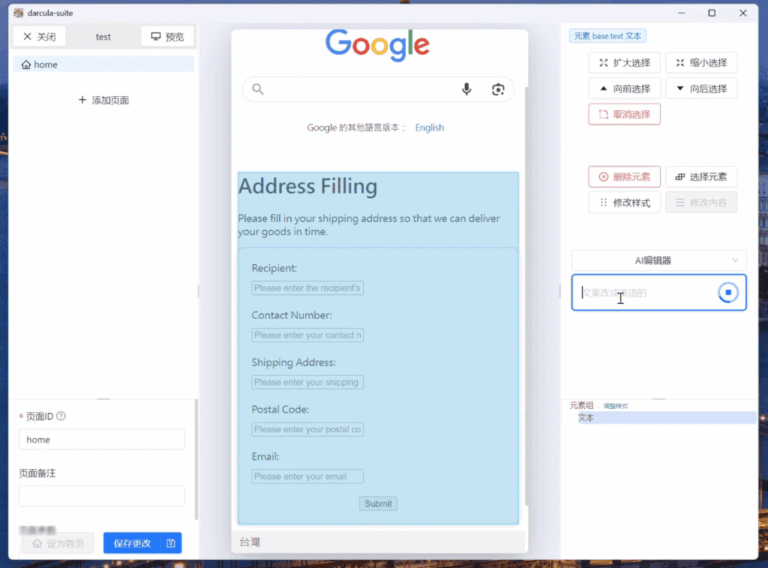
Darcula-Suite integrates AI to supercharge phishing-as-a-service operations, enabling faster, scalable, and more convincing phishing campaigns worldwide.
DslogdRAT malware exploited Ivanti Connect Secure via CVE-2025-0282, using web shells and C2 channels to evade detection and persist in networks.

Kimsuky revives PebbleDash malware using spear-phishing and patched RDP DLLs for stealthy access and control, warns new ASEC March 2025 report.

A critical vulnerability (CVE-2025-34028) in Commvault Command Center allows remote code execution. Patch immediately or isolate vulnerable instances.

Volexity uncovers Russian threat actors abusing Microsoft 365 OAuth flows via phishing, impersonation, and device registration to access email accounts.

A new phishing campaign delivers FormBook malware via Word docs, exploiting CVE-2017-11882. The fileless attack uses process hollowing to evade detection.

Critical RCE vulnerability (CVE-2025-32433) in Erlang/OTP affects Cisco products. Unauthenticated attackers can execute code remotely. Patch now!

A deep dive into a sophisticated multi-stage malware attack using Cloudflare to deliver AsyncRAT. Learn how attackers evade detection and compromise systems.