
 Do Son
A newly uncovered software supply chain campaign by the threat group Banana Squad has compromised more than...
cybersecurity

A new report from Check Point Research exposes a sophisticated malware campaign that has weaponized the modding...

Recently, Cisco Talos unveiled a new Python-based remote access trojan (RAT) dubbed PylangGhost, used exclusively by a...

A newly surfaced report from Picus has shed light on Silver Fox (a.k.a. Void Arachne or The...

A newly disclosed vulnerability in FreeIPA, an identity management solution used to centrally manage Linux and UNIX...

The U.S. Cybersecurity and Infrastructure Security Agency (CISA) has issued an urgent security advisory warning fuel infrastructure...

In a concerning development for AI infrastructure security, XLab has uncovered an active exploitation campaign targeting ComfyUI—a...

As more online service platforms adopt Passkey technology, Meta has finally followed suit, announcing the introduction of...

If your laptop is equipped with an NPU unit, you can take advantage of the newly introduced...

Two newly disclosed vulnerabilities in the Versa Director SD-WAN orchestration platform could allow authenticated attackers to execute...

A newly disclosed critical vulnerability in Versa Director, a centralized network and security management platform, may allow...

Cisco’s ClamAV, one of the most widely used open-source antivirus engines, has released versions 1.4.3 and 1.0.9...

Security researchers at Wordfence have uncovered a vulnerability in the popular AI Engine plugin for WordPress, which...
Cisco has disclosed a vulnerability in its Meraki MX and Z Series devices, affecting the Cisco AnyConnect...

Two newly disclosed vulnerabilities in Apache Traffic Server (ATS)—a core component of many cloud and content delivery...

A security vulnerability was found in Linux PAM (Pluggable Authentication Modules). Tracked as CVE-2025-6020, the flaw affects...

Trend Micro researchers have uncovered a stealthy new attack method that fuses misconfigured Docker remote APIs with...

Threat actors are ramping up attacks on poorly managed MySQL servers, particularly those running in Windows environments,...

A Server-Side Request Forgery (SSRF) vulnerability has been discovered in the @opennextjs/cloudflare package, potentially allowing unauthenticated users...
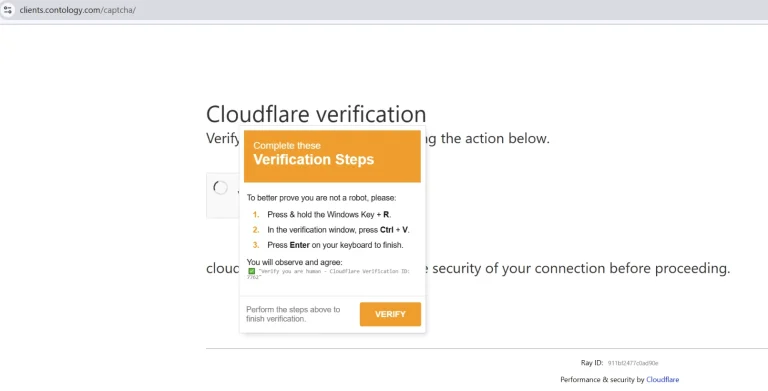
Elastic Security Labs has revealed a highly sophisticated multi-stage attack chain exploiting a social engineering method dubbed...

A critical vulnerability has been disclosed in KAON’s KCM3100 Wi-Fi gateway devices that could allow attackers to...

A fresh wave of targeted cyberattacks is sweeping across Europe, leveraging invoice-themed phishing emails and weaponizing legitimate...