
 Do Son
Unit 42 details the cyber fallout of Operation Epic Fury. Despite internet blackouts, autonomous hacktivists claim breaches of Israeli defense networks.
infosec

Socket uncovers "StegaBin," a North Korean malware campaign hiding C2 URLs in Pastebin essays to steal developer secrets via 26 typosquatted npm packages.

Google’s March 2026 Android update fixes 129 flaws, including CVE-2026-21385—a high-severity Qualcomm vulnerability currently being exploited in the wild.

An unpatched zero-day flaw (CVE-2026-2256) in the MS-Agent framework allows hackers to use prompt injection to execute OS commands and hijack AI systems.
Akamai SIRT reveals Zerobotv9, a new Mirai-based botnet targeting enterprise n8n workflow platforms and Tenda routers via critical vulnerabilities.


Infoblox uncovers a novel phishing tactic abusing the .arpa TLD. Attackers hijack internet "plumbing" to bypass firewalls and deliver brand-impersonation scams.

OpenAI’s Feb 2026 report reveals "cyber special operations," Cambodian "Date Bait" scams, and Russian content farms using AI to automate global disruption.
Zscaler unmasked APT37's "Ruby Jumper" campaign, which uses weaponized USBs and cloud services to bypass network isolation and steal data from air-gapped systems.

G DATA reveals how pirated gaming site PiviGames distributes ACRStealer via "spaghetti code" HijackLoader and DLL sideloading, causing total account takeovers.

Vitess patches critical flaws (CVE-2026-27969 & 27965) where poisoned backup manifests lead to path traversal and RCE during restoration. Update to v23.0.3 now.
Langflow 1.8.0 patches a critical 9.8 CVSS RCE vulnerability (CVE-2026-27966) where a hardcoded "allow_dangerous_code" setting enables prompt injection attacks.

Vikunja v2.0.1 patches critical flaws (CVE-2026-27575 & 28268) where "immortal" reset tokens and persistent sessions allow attackers to hijack accounts forever.
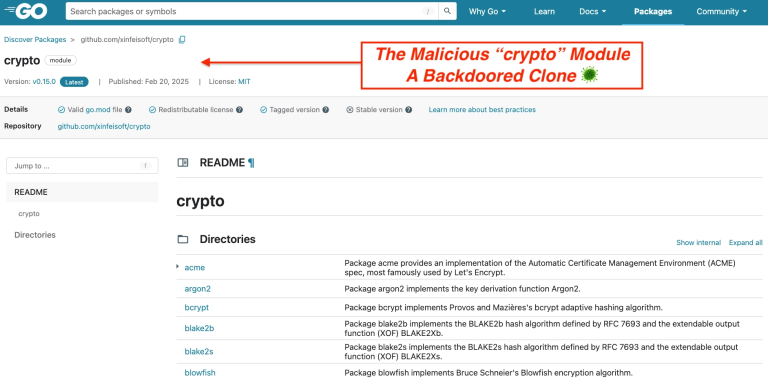
Socket uncovers a malicious Go module mimicking golang.org/x/crypto. It steals passwords via ReadPassword and deploys the Rekoobe backdoor on Linux systems.
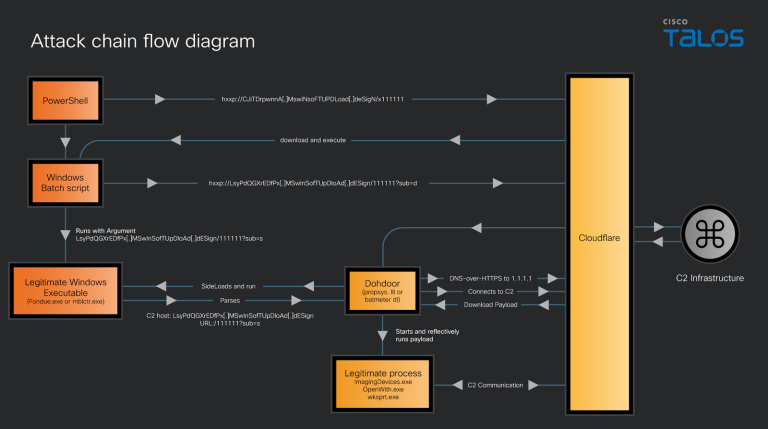
Cisco Talos uncovers "Dohdoor," a stealthy backdoor used by UAT-10027. It abuses DNS-over-HTTPS via Cloudflare to spy on U.S. healthcare and education sectors.
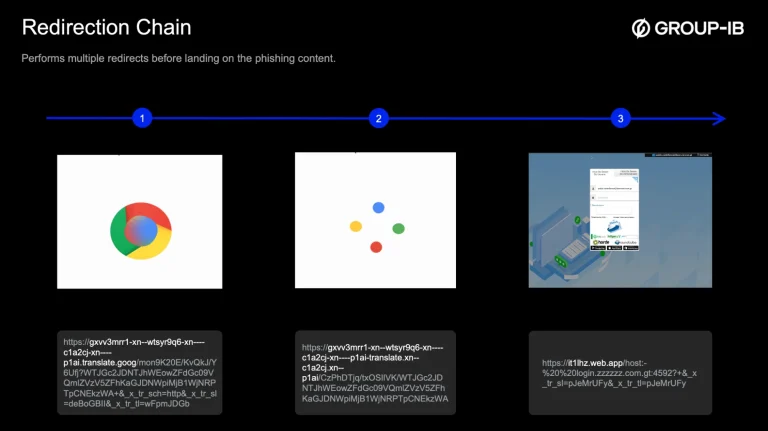
Group-IB uncovers "GTFire," a massive credential-harvesting operation abusing Google Firebase and Translate to bypass security filters in 100+ countries.
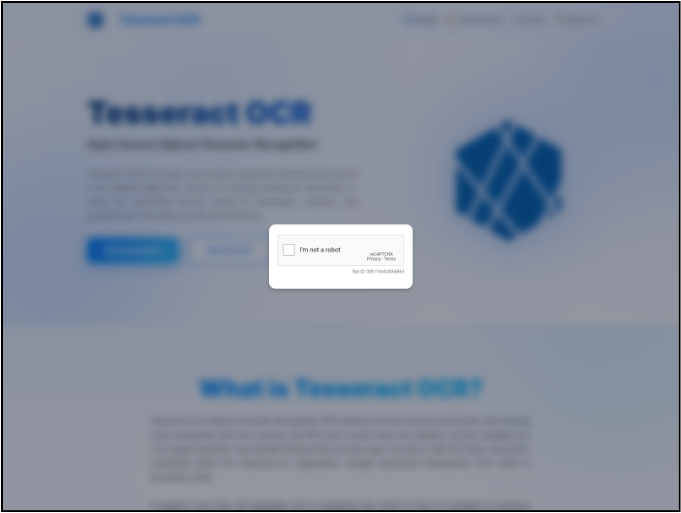
CYJAX uncovers "OCRFix," a stealthy campaign using fake Tesseract OCR sites, ClickFix social engineering, and EtherHiding to bypass security via blockchain.

OneUptime 10.0.7 patches a critical 10.0 CVSS vulnerability (CVE-2026-27728). Attackers can use traceroute probes to execute root commands and steal data.
Node.js library basic-ftp patches a critical 9.1 CVSS path traversal flaw (CVE-2026-27699). Malicious FTP servers can overwrite any file on the client machine.
Angular patches a critical 9.2 CVSS SSRF vulnerability (CVE-2026-27739). Attackers can manipulate Host headers to steal credentials and probe internal networks.

The Scattered Lapsus$ Hunters "supergroup" is paying $1,000 per successful vishing call. Discover how they use female recruits to bypass corporate IT security.
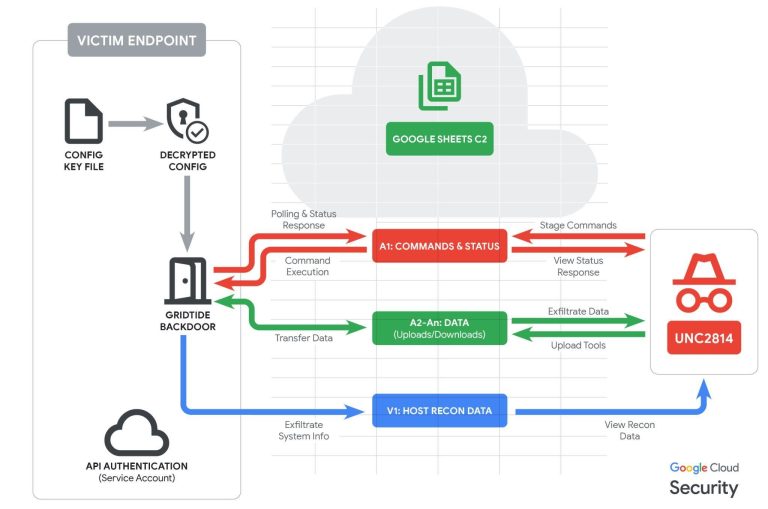
Google and Mandiant disrupt UNC2814, a China-nexus group using the GRIDTIDE backdoor to hide command-and-control traffic inside Google Sheets across 42 nations.