
 Do Son
IceWarp urges immediate patching for critical flaws allowing unauthorized server access, XSS, and arbitrary file reading. Update your instances today.
infosec

Unit 42 warns of active attacks on critical BeyondTrust flaw CVE-2026-1731. Hackers bypass auth for RCE and data theft. Patch self-hosted instances now.
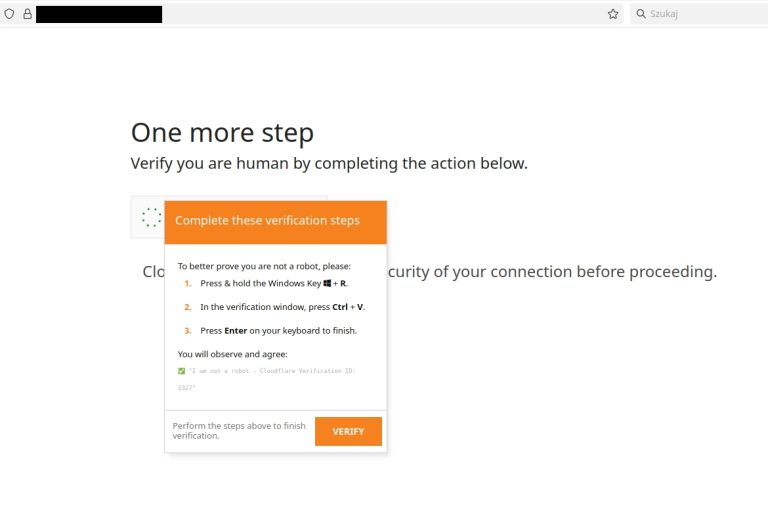
CERT Polska reveals how a fake "ClickFix" CAPTCHA campaign tricked users into deploying evasive Latrodectus and Supper malware. Protect your network now.
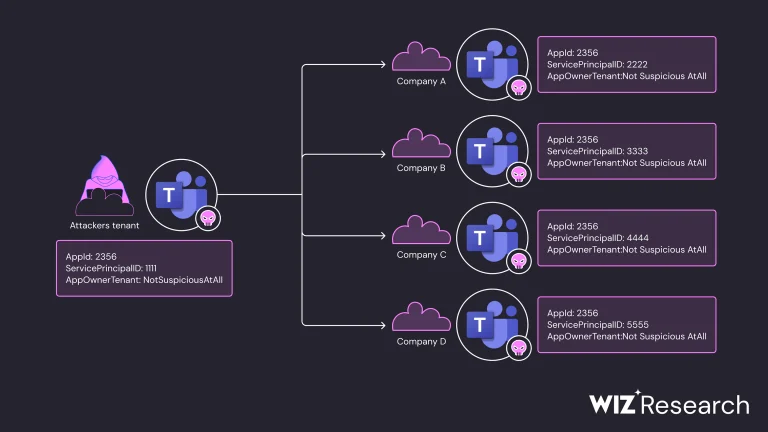
Wiz Research exposes a stealthy threat using malicious OAuth apps and Cyrillic homoglyphs to bypass Microsoft Entra ID security. Protect your cloud tenant.
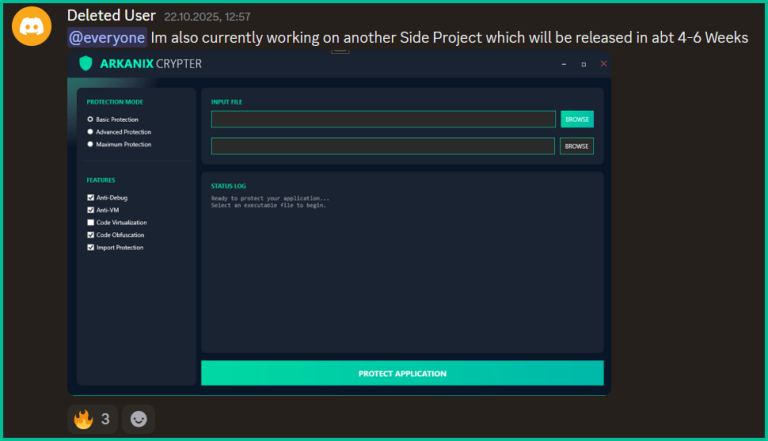
Kaspersky exposes Arkanix Stealer, a fast-moving MaaS operation leveraging Discord, tiered subscriptions, and AI-assisted development for quick data theft.
The FBI warns of a massive surge in ATM jackpotting attacks. Cybercriminals are using Ploutus malware to bypass the XFS layer and drain cash reserves.
Insikt Group exposes GrayCharlie compromising WordPress sites & US law firms. Attackers use "ClickFix" fake CAPTCHAs to deploy the NetSupport RAT.

A critical PDF Object Injection flaw (CVE-2026-25755) in jsPDF allows attackers to bypass AcroJS sandboxes. Update to version 4.2.0 immediately.
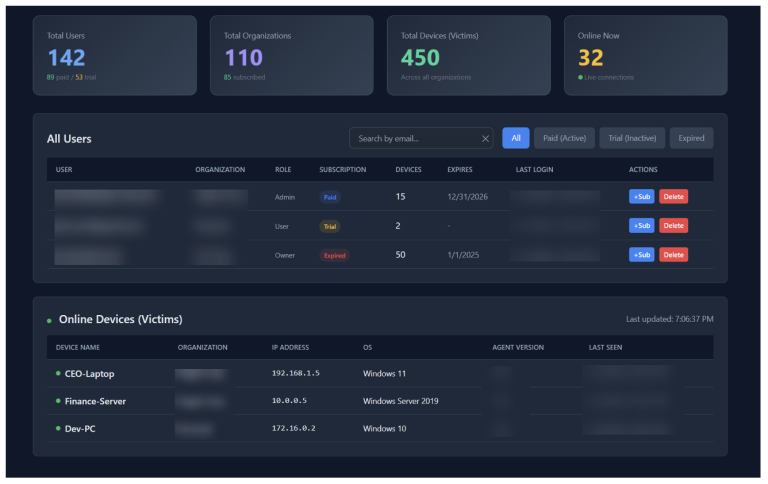
Proofpoint exposes TrustConnect, a new Malware-as-a-Service masquerading as an IT tool. The AI-assisted fake RMM software replaces dismantled threats.

A critical Windows Error Reporting flaw (CVE-2026-20817) allows local privilege escalation to SYSTEM. With the PoC publicly disclosed, update immediately.
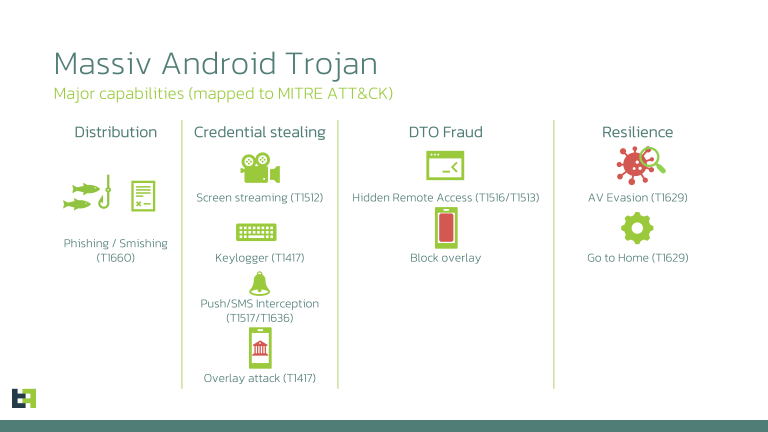
ThreatFabric exposes Massiv, a new Android banking Trojan hiding in fake IPTV apps. The malware uses accessibility permissions for full device takeover.

Ukrainian hacker Oleksandr Didenko receives a 60-month sentence for orchestrating a massive laptop farm scheme aiding North Korean IT operatives.

Apache Tomcat rolls out urgent updates for versions 9, 10, and 11 to fix legacy HTTP/0.9 protocol confusion and SNI certificate bypass flaws. Patch now.

Texas AG Ken Paxton sues TP-Link, alleging the Wi-Fi giant's routers act as Trojan horses for CCP surveillance. State bans TP-Link gear for employees.

Critical VS Code Live Server flaw CVE-2025-65717 (CVSS 9.1) lets attackers steal source code and credentials via malicious links. Protect your workspace now.

Google's VP Vijaya Kaza reveals 1.75M bad apps blocked in 2025. Android 16 introduces one-line tapjacking protection to fight AI-powered cyber threats.

Splunk Enterprise Windows flaws (CVSS 7.7) CVE-2026-20143 & CVE-2026-20140 allow system takeover via DLL and Python search path hijacking. Patch immediately.
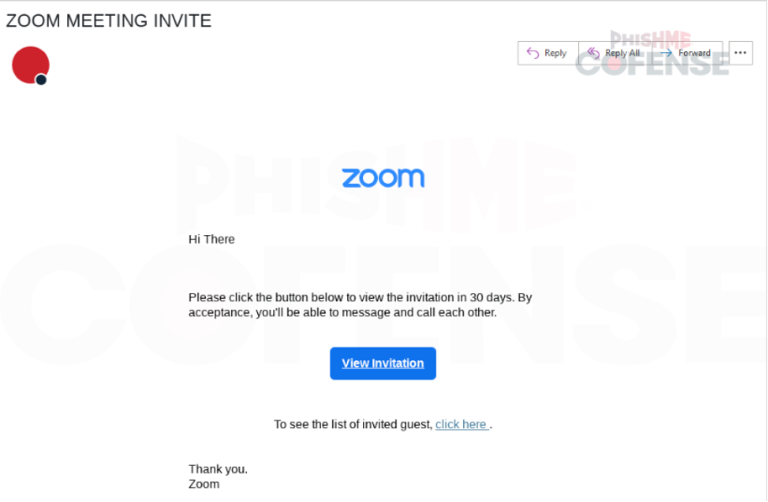
Cybercriminals are using fake DocuSign emails and the JWrapper framework to stealthily deploy SimpleHelp remote access tools. Learn how to spot the threat.

NVIDIA warns of 7.8-rated vulnerabilities in Megatron Bridge. Learn how "educational" tutorials could let attackers hijack your AI training infrastructure.

Urgent: PostgreSQL patches 5 flaws, including 3 critical RCEs (CVSS 8.8). Attackers can execute code as OS user via text manipulation. Update v14-18.
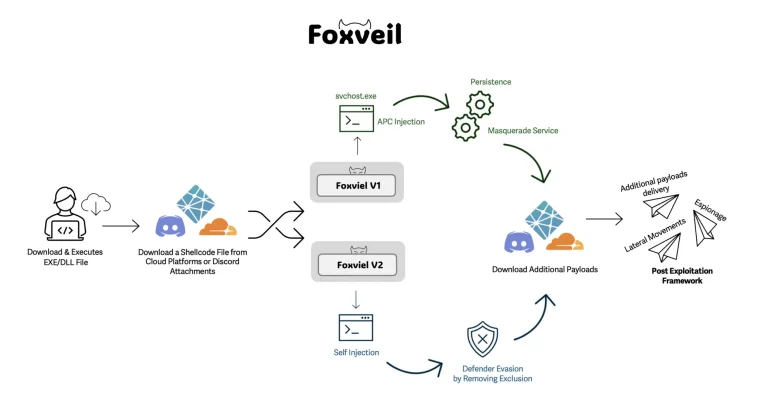
Cato CTRL discovers Foxveil, a new malware loader abusing Cloudflare, Netlify & Discord to bypass defenses. Active since Aug 2025. Learn the signs.

Lotus Blossom hijacked Notepad++ updates to target admins. The supply chain attack deployed Chrysalis backdoor. Update to v8.9.1 immediately.