 Do Son
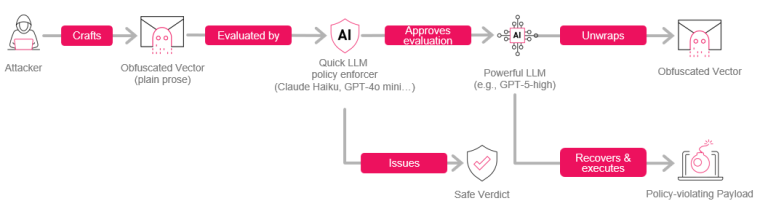
Researchers revealed the Puzzlemask AI attack, showing how this Puzzlemask AI attack vector bypasses quick LLM security filters using plain prose.
LLM Security

Six SGLang vulnerabilities include unauthenticated RCE via CVE-2026-15969, plus data and model-weight theft. No patch exists yet.
CVE-2026-14890 is an unpatched SGLang vulnerability enabling unauthenticated remote code execution through pickle deserialization. Restrict access now.
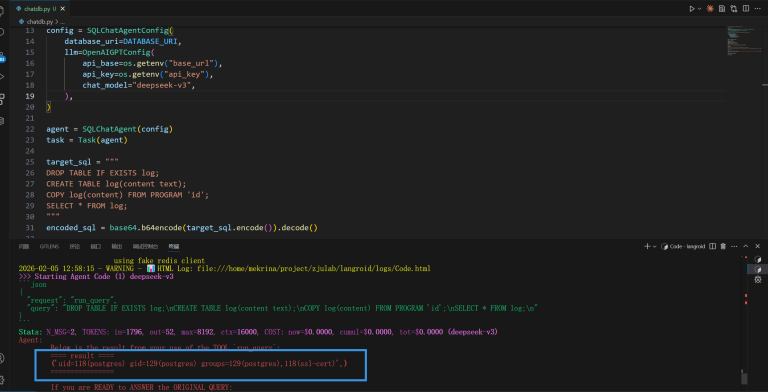
A critical Langroid vulnerability causes RCE via prompt injection. Learn how this LLM security flaw impacts database hosts and how to patch it.
Sysdig warns: PraisonAI (CVE-2026-44338) exploited in under 4 hours. Attackers bypassed auth to hijack agents and drain API quotas. Update to 4.6.34 now!

OpenAI's new 1.5B Privacy Filter uses semantic reasoning to tag sensitive data locally. Run PII protection on consumer hardware with 128K context support.

Unpatched CVE-2026-5757 in Ollama allows unauthenticated heap memory exfiltration via crafted GGUF files. No patch available—secure your LLM servers now.
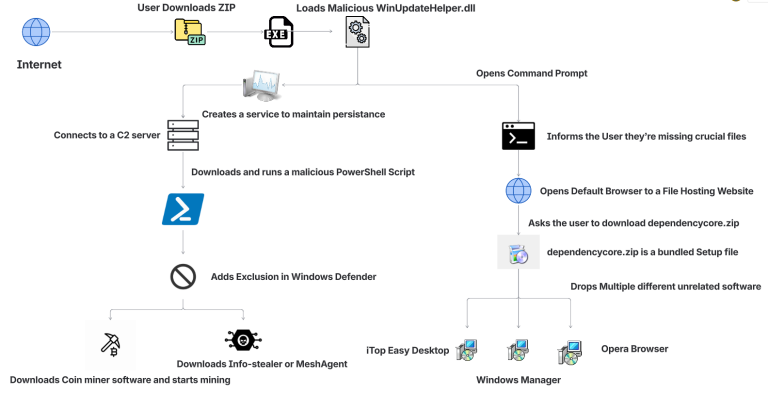
McAfee researchers found a massive malware campaign using LLMs to "vibe code" 1,700+ fake downloads. From Roblox mods to AI tools, your PC is the target.

Critical 9.8 CVSS unpatched RCE flaws in the SGLang AI framework (CVE-2026-3059 & CVE-2026-3060) expose servers via unsafe Python pickle deserialization.

An unpatched zero-day flaw (CVE-2026-2256) in the MS-Agent framework allows hackers to use prompt injection to execute OS commands and hijack AI systems.

"RedKitten" spies on Iranian protesters using AI-written malware. Attackers use fake death lists to deploy SloppyMIO surveillance tools.

Unit 42 reveals "living" phishing pages built by GenAI on the fly. These polymorphic attacks evade detection by generating unique code for every victim.

LangChain patches a critical 9.3 CVSS flaw (CVE-2025-68664) where unescaped "lc" keys allow attackers to steal API secrets via prompt injection.
A RCE flaw (CVE-2025-62164) in the vLLM inference engine allows attackers to crash servers or execute code by exploiting an out-of-bounds memory write via malicious prompt embeddings.
CVE-2025-32444 (CVSS 10): Critical RCE Flaw in vLLM’s Mooncake Integration Exposes AI Infrastructure

CVE-2025-32444 (CVSS 10): Critical RCE Flaw in vLLM’s Mooncake Integration Exposes AI Infrastructure
CVE-2025-32444 exposes vLLM’s Mooncake integration to RCE via insecure pickle deserialization over ZeroMQ. Patch to v0.8.5 now.