
 Do Son
North Korea's Lazarus Group is waging a covert cyberespionage campaign, poisoning 234+ open-source packages on npm/PyPI to steal secrets from CI/CD pipelines and developer environments.
malware

Kaspersky exposes a stealthy cyberespionage campaign targeting Russian IT firms and global businesses, using DLL hijacking, social media C2, and obfuscation to deploy Cobalt Strike.

Sophos uncovers a new infection chain for GOLD BLADE's RedLoader malware, combining LNK files, WebDAV, and DLL sideloading to bypass defenses and deploy payloads stealthily.

Check Point Research exposes JSCEAL, a stealthy malware campaign using malvertising and fake apps to steal crypto credentials and wallets via compiled JavaScript payloads.

Trellix uncovers 0bj3ctivityStealer, a sophisticated info-stealer using phishing, custom PowerShell, and steganography to evade detection and exfiltrate sensitive data.

Netskope uncovers XWorm 6.0, a new variant using VBScript droppers, AMSI bypass, and critical process marking to evade detection and force system reboots if terminated.

A new stealthy campaign uses Windows LNK files to deploy the REMCOS backdoor via multi-stage PowerShell commands, bypassing antivirus and gaining full system control.

Security researcher Vasilis Orlof exposes QWINS LTD, a suspected bulletproof hosting provider registered in the UK, allegedly fueling global malware campaigns with Lumma, Mirai, and more.

Hybrid Analysis reveals SHUYAL, a new stealthy infostealer that harvests browser credentials, system data, and screenshots, exfiltrating it all via a Telegram bot.

A phishing attack compromised the 'is' npm library maintainer, leading to malicious versions being published with backdoors for remote code execution. Update immediately!

Socket discovered 10 malicious npm packages from Toptal's GitHub, exfiltrating GitHub tokens and wiping systems. The compromise vector is under investigation.

Wiz Research uncovers Soco404, an evolving cryptojacking operation exploiting cloud misconfigurations and PostgreSQL to stealthily mine cryptocurrency across Linux and Windows.

CYFIRMA uncovers EdskManager RAT, a sophisticated remote access trojan using HVNC, multi-stage execution, and advanced persistence for covert, long-term system access.

Akamai confirms Coyote, a Latin America-focused banking trojan, is the first malware to exploit Microsoft's UI Automation (UIA) framework in the wild for credential theft.

Arch Linux users are urged to uninstall and reinstall Firefox, LibreWolf, or Zen Web from AUR immediately due to malicious versions containing the CHAOS RAT trojan.

Weeks after a major takedown, Lumma Stealer has resurfaced with new stealth tactics, exploiting cracked software, fake CAPTCHAs, and GitHub to resume its credential-stealing operations.

The Mimo threat actor has broadened its scope to Magento, employing advanced persistence, fileless execution, cryptojacking, and proxyjacking in a sophisticated new campaign.

AmateraStealer (formerly ACRStealer) has significantly evolved, using low-level NTAPIs, Heaven's Gate, and multi-layered encryption to evade detection and steal sensitive data.

Greedy Sponge, a financially motivated group, is back with an upgraded AllaKore RAT and SystemBC, targeting Mexican organizations for banking credentials and financial fraud.
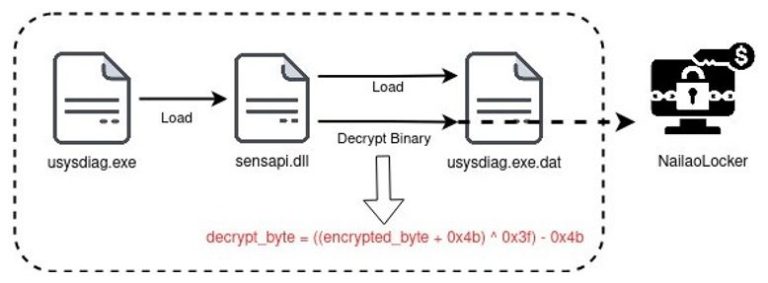
FortiGuard Labs unveils NailaoLocker, a new ransomware using Chinese SM2 encryption and a built-in, non-functional decryptor, suggesting a prototype or decoy.

JPCERT/CC details a sophisticated, ongoing malware campaign exploiting Ivanti Connect Secure (CVE-2025-0282, -22457) using MDifyLoader, Cobalt Strike, vshell, and Fscan for stealthy persistent access.

LAB52 uncovers a sophisticated phishing campaign delivering DeedRAT, a modular backdoor by Chinese APTs, targeting Southeast Asian governments via vulnerable AV software.