 Do Son
The Android SMS of Death flaw crashes telephony services via malformed WAP Push messages, triggering persistent bootloops without user interaction.
mobile security
The Google Registered App Stores program brings seamless one-click app installs and background updates to verified third-party Android marketplaces.
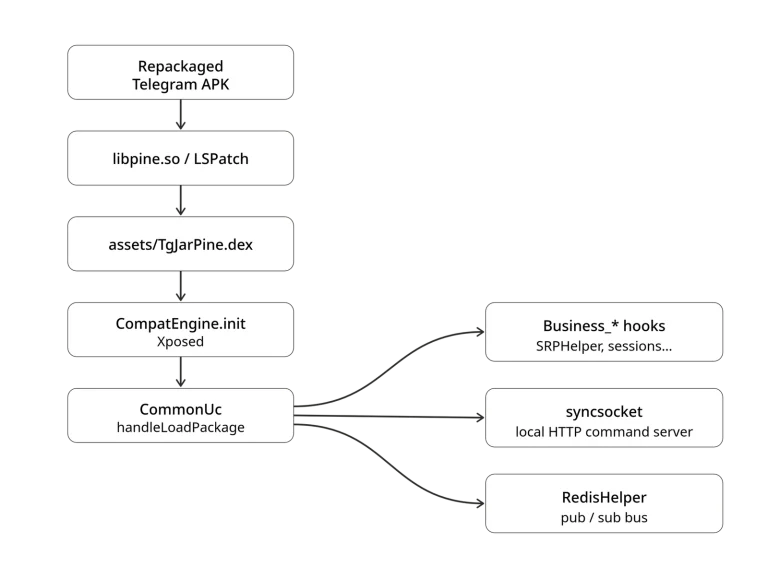
Researcher Ovi exposes uCreator Android spyware. The YingGai uCreator Android spyware platform uses VirtualApp and LSPatch to hijack 20 mobile apps.
Details and a PoC are public for CVE-2026-113380, a Signal call vulnerability in RingRTC that keeps calls live after hang-up. Update now.
Android phone number verification now links your numbers to every Google account on the device. Here is how to turn it off.
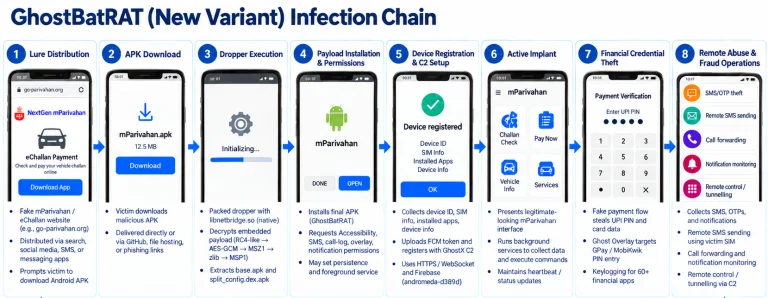
Cyble reveals the GhostX ecosystem where Android GhostBat RAT and the new GhostBat RAT variant use Ghost Overlay to steal PINs from 60 Indian apps.

ThreatFabric uncovers the Hirudo banking trojan. The Android Hirudo banking trojan replaces real banking apps with patched copies to steal funds.
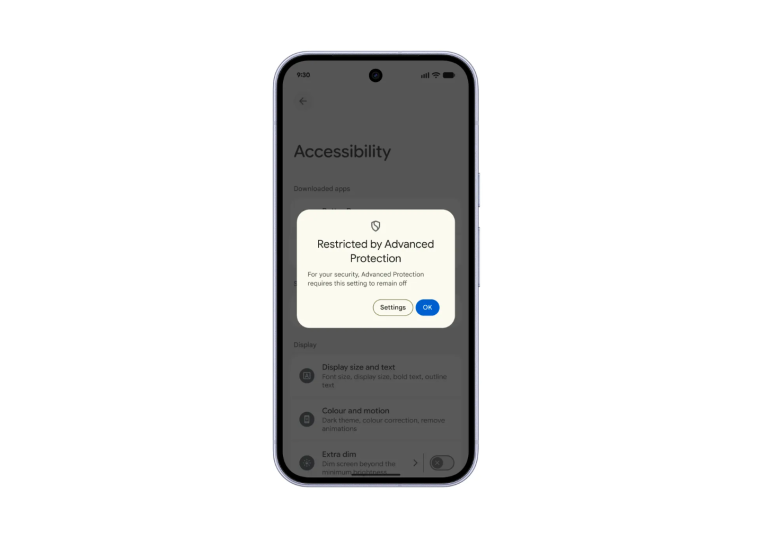
Discover how Google fortified Android Advanced Protection in version 17, introducing intrusion logging, USB security, and AccessibilityService restrictions.
MediaTek security bulletin for October 2026 fixes 31 flaws, including critical MediaTek modem vulnerability CVE-2026-20519. Update now.
Critical Capacitor vulnerability CVE-2026-103922 (CVSS 9.3) affects a package with 5.5M weekly downloads. Update to a patched release now.

CVE-2026-28576 (CVSS 10) is a SQL injection in the Android Contacts Provider. A public PoC dumps all contacts with no permissions. Patch Android 17 now.
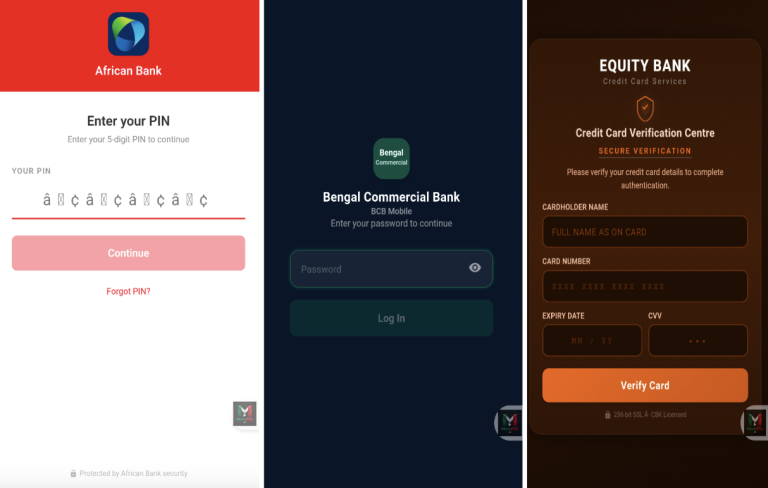
The new ToxicPanda 2.0 banking Trojan attacks target hundreds of financial apps globally. Learn how this ToxicPanda 2.0 banking Trojan steals credentials.
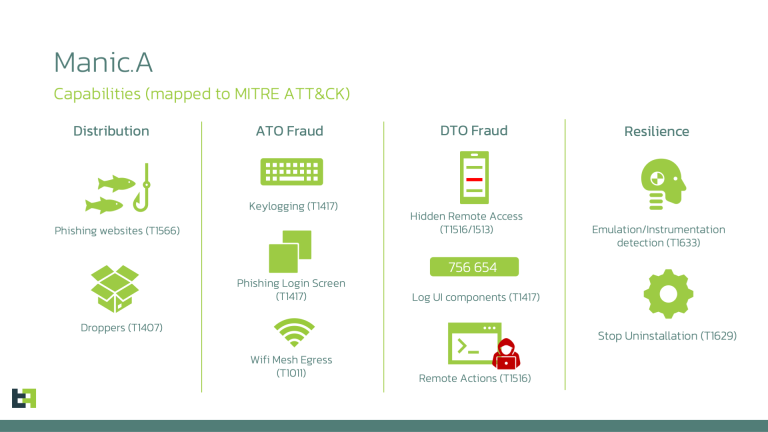
A new Manic Android malware campaign combines banking fraud and spyware, using a unique offline mesh relay to steal data even without internet access.

Samsung One UI 9 permanently locks a phone after 13 wrong passcodes, forcing a factory reset. Accidental lockouts remain very unlikely by design.

A major VoLTE security flaw leaves millions at risk. Learn how this Verizon IMS vulnerability allows undetected call hijacking and message spoofing.

A serious Cordova vulnerability allows data spoofing. This InAppBrowser callback flaw lets remote attackers bypass iOS boundaries undetected.

A sophisticated Android carrier billing fraud campaign hit users worldwide. Learn how fake apps trigger premium SMS abuse and how to stay safe.

HUMAN's Satori team disrupted Trapdoor, an Android ad fraud ring using 455 apps and hidden WebViews to fake 659 million daily ad bids.
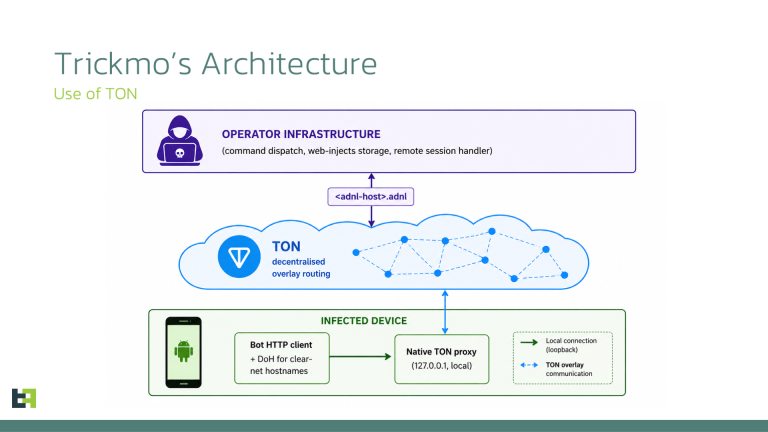
ThreatFabric uncovers TrickMo Variant C, a new Android banking trojan using the decentralized TON network to evade detection and turn phones into proxies.
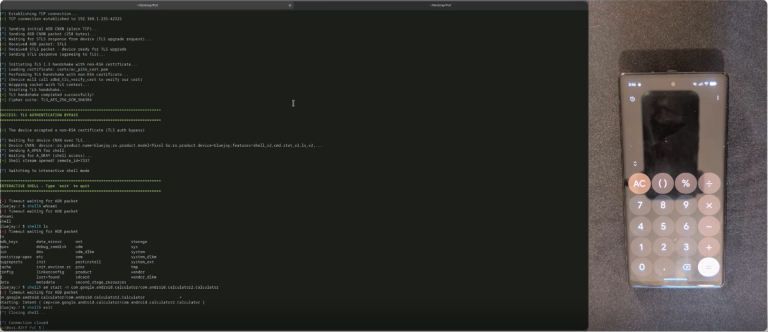
BARGHEST reveals CVE-2026-0073: a zero-click Android ADB bypass over Wi-Fi. Public PoC and exploit details are now live. Secure your mobile device today!

Ivanti confirms active exploitation of EPMM (CVE-2026-6973). Attackers are using old credentials to hijack mobile management. Patch to v12.8.0.1 immediately!