
 Do Son
Cisco Talos exposes Pheno, a malware plugin that hijacks Microsoft Phone Link to steal SMS and 2FA codes without touching your phone. Secure your PC today!
mobile security

Bitdefender uncovers a massive smishing campaign targeting drivers with fake toll and parking fines. Over 79,000 messages sent across 12 countries.
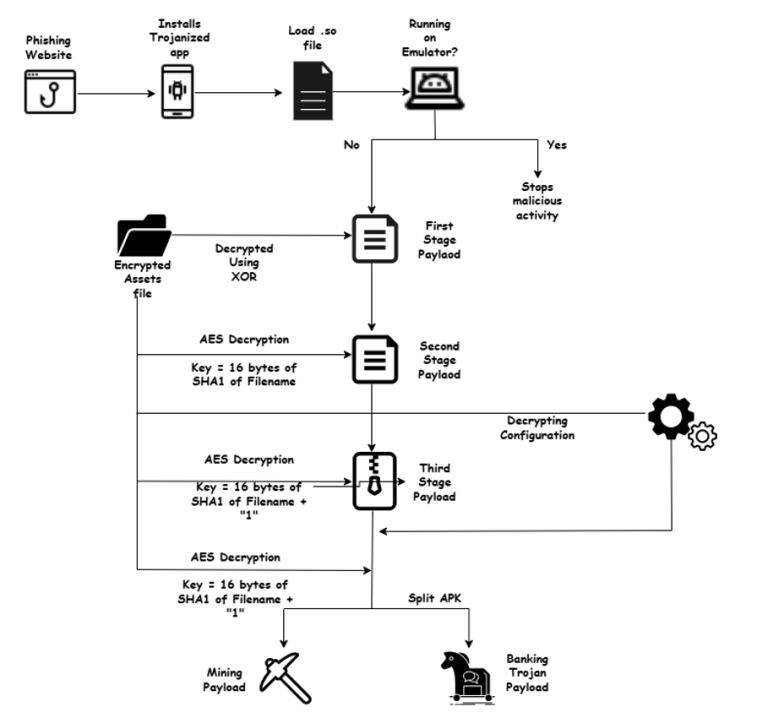
Cyble reveals MiningDropper, a modular Android threat delivering RATs and infostealers via multi-stage payloads. Protect your mobile devices now.

Microsoft warns of a 50M-user flaw in EngageSDK affecting crypto wallets. An intent redirection bug could leak private data. Update to v5.2.1 now!

McAfee unmasks Operation NoVoice: a sophisticated Android rootkit that survives factory resets to clone WhatsApp sessions and seize full device control.

Google’s April 2026 Android bulletin fixes a critical zero-interaction DoS in the Framework and high-severity StrongBox HSM flaws. Update your device now.

Sophos uncovers Keenadu, a persistent Android firmware backdoor embedded in core libraries that gives attackers total control via the Zygote process.
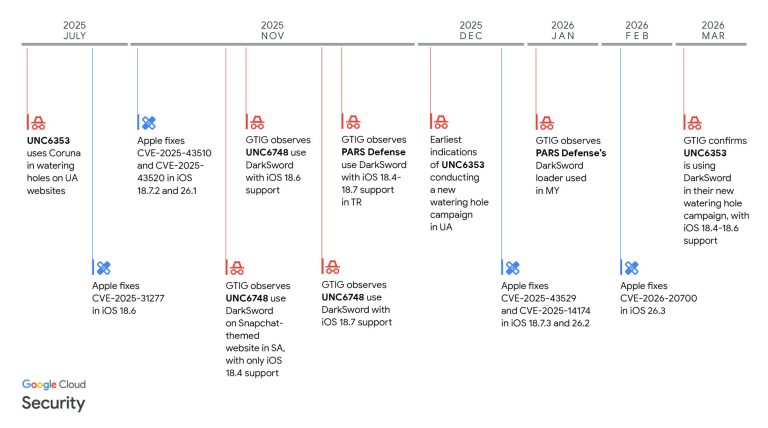
Google uncovers DarkSword, a sophisticated iOS full-chain exploit used globally to deploy spyware via zero-day vulnerabilities. Update to iOS 26.3 now.
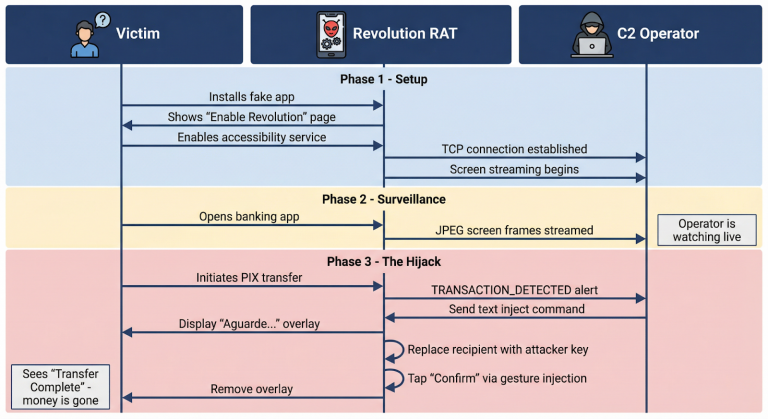
Zimperium's zLabs exposes PixRevolution, a novel Android banking trojan using real-time surveillance to hijack Brazil's PIX instant payments.
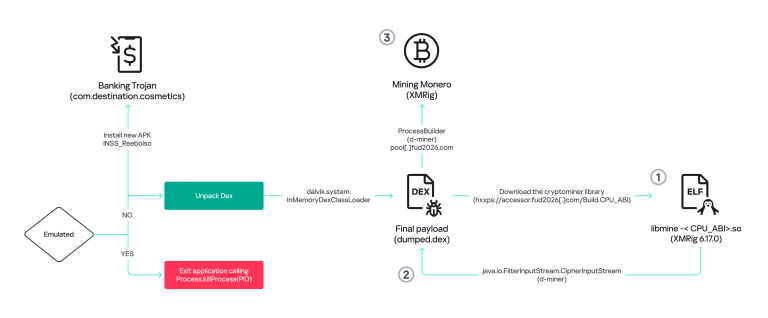
Kaspersky uncovers BeatBanker, an Android malware in Brazil using an audio loop to evade detection while mining crypto and stealing banking credentials.
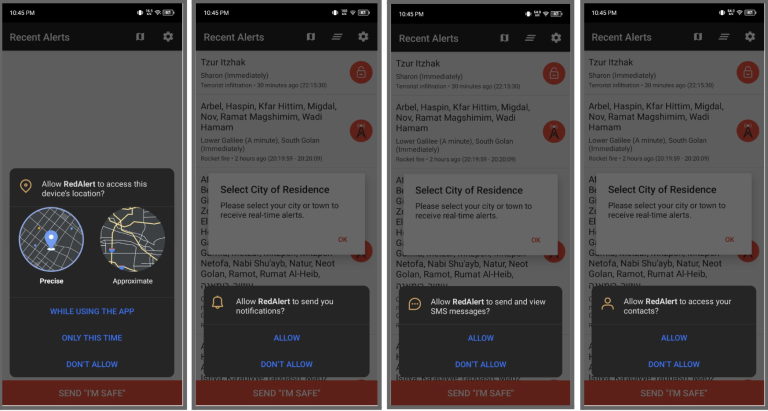
CloudSEK exposes a smishing campaign spreading a trojanized "Red Alert" app. The fake emergency tool tracks locations and steals data during air raids.

In a historic first, NATO has certified retail iPhones and iPads running iOS 26 for "Restricted" data, proving Apple’s consumer hardware is officially war-ready.
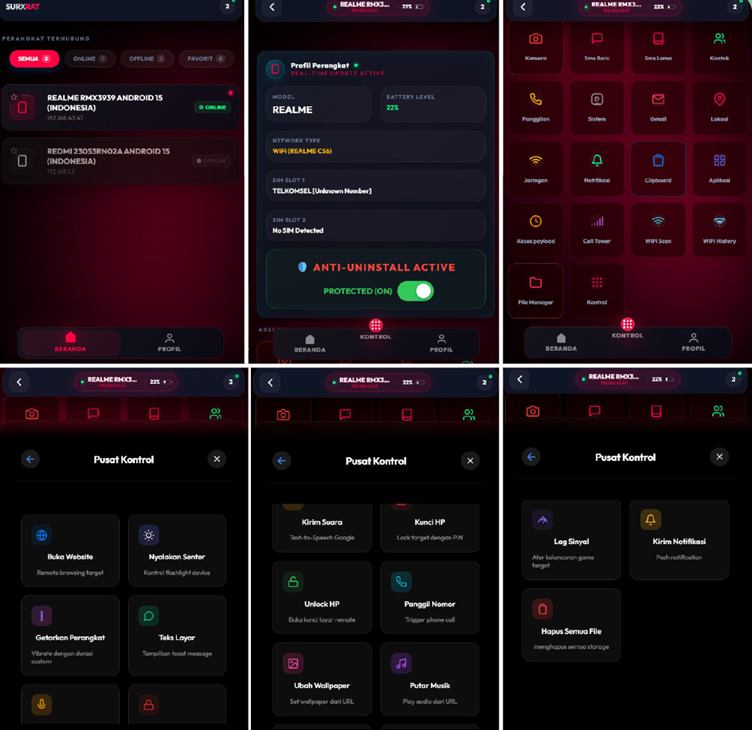
Cyble Research unmasks SURXRAT V5, a professionalized Android RAT experimenting with AI-assisted modules and hybrid monetization via Firebase infrastructure.
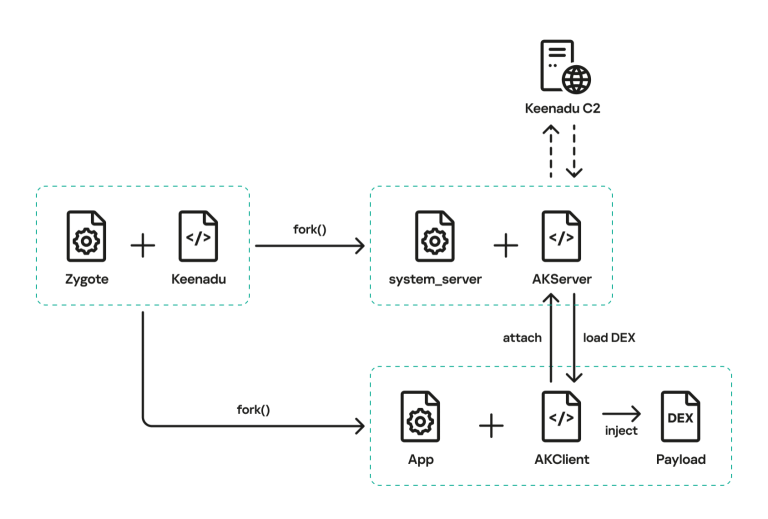
Kaspersky uncovers Keenadu, a firmware-level Android backdoor infecting the Zygote process. This pre-installed malware gives attackers full control.

Ivanti EPMM under attack via zero-days CVE-2026-1281 & 1340. Hackers use bash scripts to plant dormant backdoors. Patch immediately.

New Telegram phishing campaign abuses the "This is me" feature for account takeover. CYFIRMA reveals a global framework evading detection. Stay alert.

In a troubling convergence of trusted developer infrastructure and cybercrime, Bitdefender researchers have uncovered a sophisticated Android...

Ivanti confirms critical EPMM RCE flaws (CVE-2026-1281) are exploited in the wild. Unauthenticated attackers can compromise MDM. Patch immediately.

New Android anti-theft updates use AI to detect "snatch-and-run" theft and instantly lock your screen. Identity Check adds biometric layers to stop thieves.
Public PoC exploit for Android CVE-2024-23700 allows critical privilege escalation without user interaction. WearOS & Custom ROMs are at risk.

Scammers target PNB MetLife users via mobile phishing. Attackers use Telegram bots to steal data & manipulate clipboards for UPI fraud.

Jamf reveals Predator spyware's advanced anti-analysis tactics. It now detects Corellium, hides recording icons, and tracks why infections fail.